
Tag:

AI generated code

4 articles

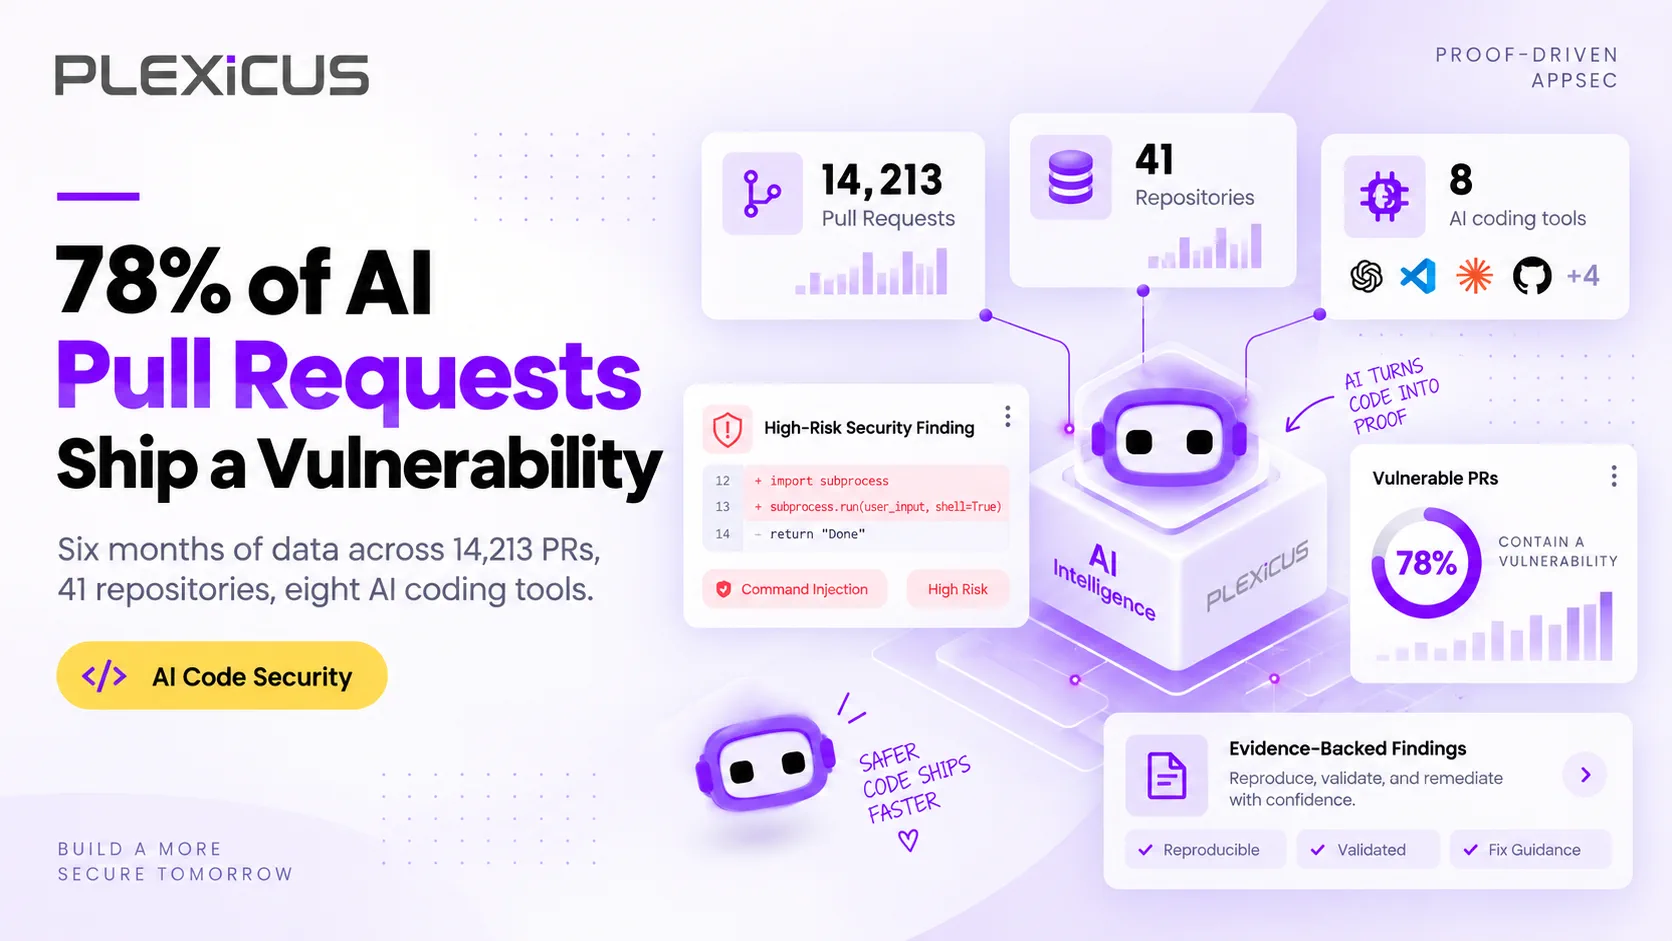
78% of AI-Generated PRs Contain a Vulnerability. Here's What We're Seeing.
AI Code Security

78% of AI-Generated PRs Contain a Vulnerability. Here's What We're Seeing.

Across thousands of AI-generated pull requests scanned in the past six months, 78% contained at least one vulnerability that survived the human review pass. The failure modes are not random. They cluster. Here is the data, the incidents, and what your team can do about it.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Vibe Coding セキュリティガバナンス:Codex、Claude Code、Cursor、AIコーディングエージェントを安全に導入する方法
Learn

Vibe Coding セキュリティガバナンス:Codex、Claude Code、Cursor、AIコーディングエージェントを安全に導入する方法

AIコーディングツールは開発者の生産性を向上させていますが、開発の高速化には、より優れた可視性、強力なレビューワークフロー、信頼性の高い修正プロセスが必要です。これは、Codex、Claude Code、Cursor、Windsurf、その他のAIコーディングエージェントを導入するチーム向けの実践的なガバナンスガイドです。

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
AIネイティブ修復によるVibe Codingセキュリティ
Learn

AIネイティブ修復によるVibe Codingセキュリティ

検出だけではAIスピードの開発に対応できません。AIネイティブ修復は次の層です。SDLCのあらゆる段階でAI生成コードの脆弱性を修正、検証、追跡するチームを支援します。

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Vibe Coding セキュリティ:AI生成コードを出荷前に保護する
Learn

Vibe Coding セキュリティ:AI生成コードを出荷前に保護する

AIコーディングツールは、ほぼすべての新規コードの半分を記述しています。そして、そのコードの45%には少なくとも1つの脆弱性が含まれています。Vibe Codingセキュリティは、AIによって作成されたソフトウェアを保護し、リスクを本番環境に到達する前に検出、優先順位付け、修復する実践です。

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

Teams with fewer than 50 developers: start a 14-day Trial instead of booking a demo. Start a 14-day Trial →

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)