PLEXICUS / AI SWARM PENTEST SPAIN · SCOPED SERVICE ENGAGEMENT

AI Swarm Pentest for teams building critical software

Find exploitable paths before attackers do.

AI Swarm Pentest validates exploitable paths across your application, API, and source code. Your team receives the evidence, impact context, and a remediation path they can review.

Reviewed attack paths. Independent verification. No automatic production changes.
José Ramón Palanco Speak with our founder, José Ramón Palanco. 15+ years of cybersecurity experience.
If you don't fit the ICP, we'll tell you too — without wasting your time.

Share the scope and we will tell you if it fits.

Trusted by security teams shipping AI-generated code

Plexicus technology and ecosystem

Nexus turns attack hypotheses into evidence your team can verify.

AI Swarm PentestValidated attack paths · authorised scope
EvidenceAttached to every finding for review
VerifiedSeparate reproduction before a finding is published
AI SWARM PENTEST · NEXUS

Nexus does not match patterns. It thinks like an attacker.

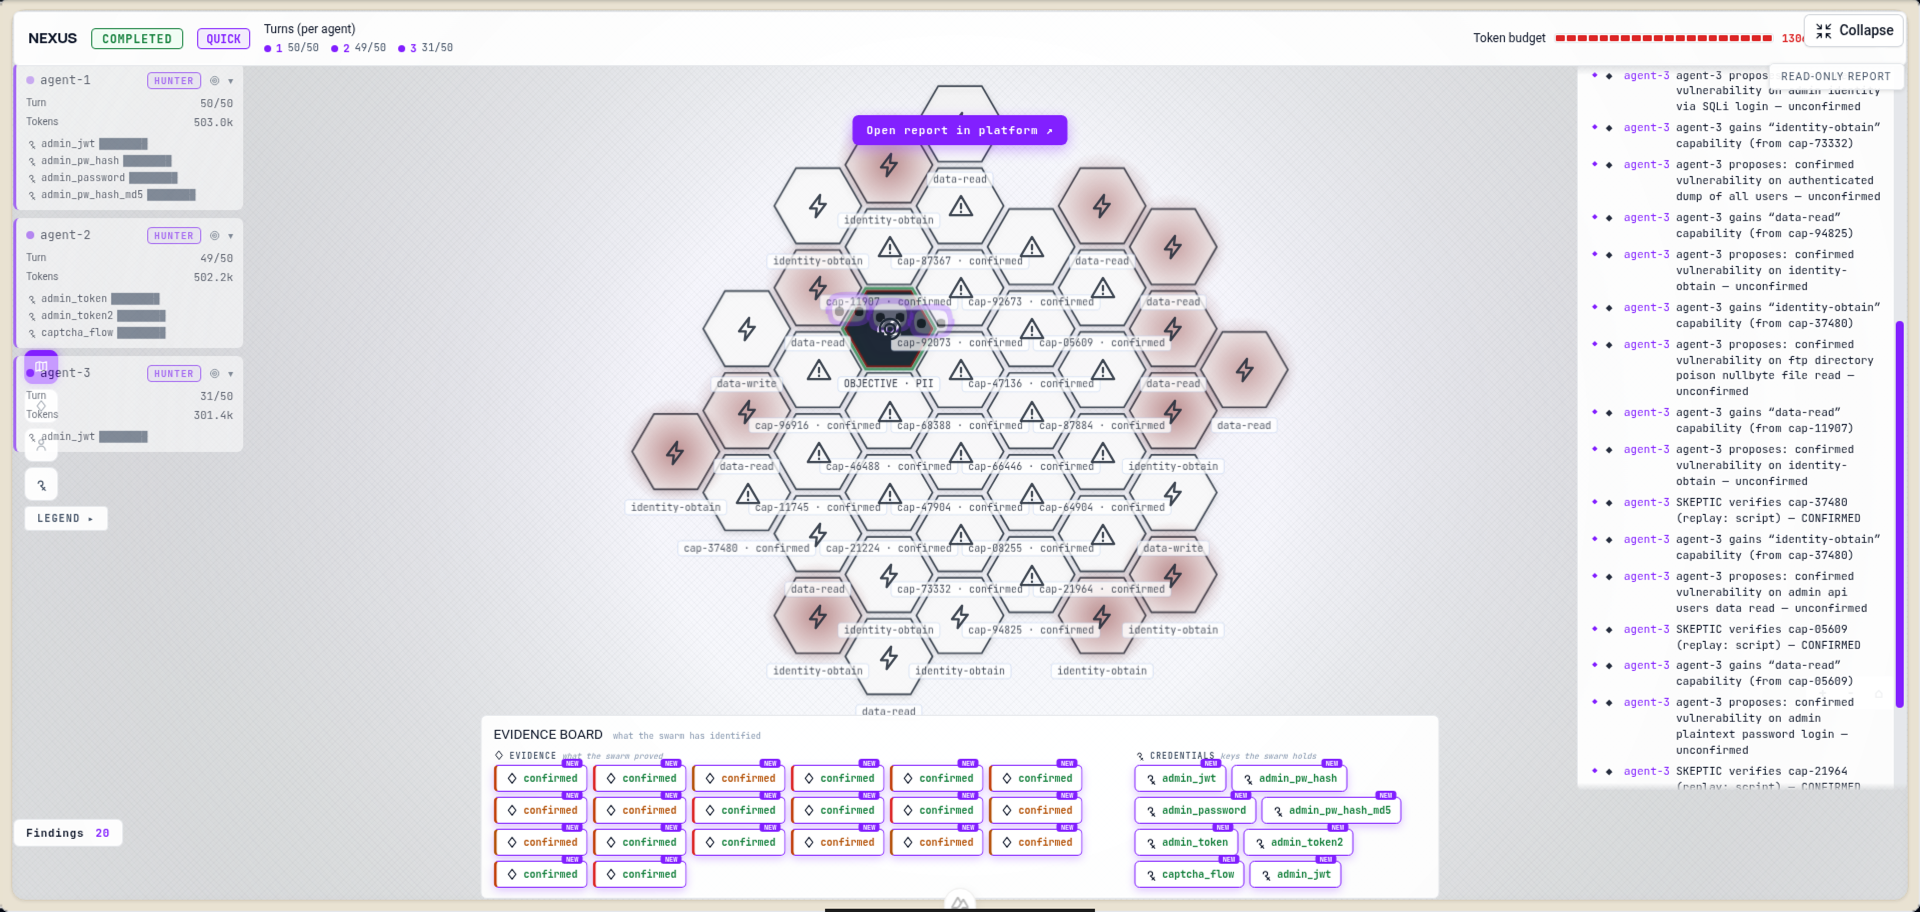
Plexicus validates relevant attack paths within the agreed scope and gives your team evidence they can review.
  • Stays inside the agreed scope
  • Shared working context
  • Human final decision
Plexicus Nexus runtime product view showing verified attack paths and evidence handover.
Real Nexus runtime A clear handover from exploration to evidence. Live product view of the evidence workflow.
A real customer experience

As one of Plexicus's first customers, we've witnessed firsthand how their platform has evolved into an indispensable security solution. Their AI-powered remediation has dramatically reduced our vulnerability management overhead and allowed our security team to focus on strategic initiatives instead of repetitive fixes.

Jose Fernando Dominguez Jose Fernando Dominguez CISO, Ironchip Ironchip · customer voice

Every unpatched finding is work still owed. The challenge is knowing what is real — and what to do next.

Your external pentester hands you a report. Your in-house team still has to decide what to do with it. Meanwhile, every unclosed finding is work that has piled up against your team: the team stops understanding its own surface, questions pile up, and the next audit may find the same things again.

A scanner compares signatures and a chatbot gives advice. AI Swarm Pentest forms hypotheses, explores attack paths, and connects the evidence. It automates repetitive work without replacing your team's context or decision.

What we deliver

What the engagement delivers.

If what you need is in the right column, this product isn't for you. We'll tell you in the qualification so nobody wastes theirs.

Yes it is
  • AI Swarm Pentest of an authorised application, API or test environment with Nexus.
  • Report prioritised by real risk (CVSS + context), not by order of arrival.
  • Independent verification for every finding presented as verified.
  • A handover session with your technical team.
  • Scope and scope agreed in writing confirmed before work starts.
No it isn't
  • A signature scanner, a security chatbot, or a check without a signed scope.
  • A classic multi-day on-site human pentest.
  • An endless list of 'potential issues' with no prioritisation.
  • Automatic modifications to production.
The process

Three steps. One actionable result.

From an agreed scope to a demonstrated attack path, supporting evidence and a clear next step for your team.

  1. Start
    Scope + rules

    We define the authorised application, API or environment, the rules of engagement and any test access required. Nexus does not act outside that scope.

    01
  2. Analysis
    Attack + verification

    The engagement maps the surface, forms hypotheses, and tests paths. A second pass independently confirms each finding before it is marked verified.

    02
  3. Delivery
    Evidence + handover

    You receive verified findings, supporting evidence, a clear priority, and a documented handover for the next decision.

    03
The deliverable

At the end you have this.

  • Two-layer report: an executive CTO readout plus a PDF evidence pack with verified findings, severity, supporting evidence and cross-verification.
  • Complete attack chain: target, steps, demonstrated impact and the context your team needs.
  • Verified findings: confirmed paths and why each one deserves attention.
  • Verification status and priority: what was observed and why it deserves attention.
  • Documented handover with the context your technical team needs to decide the next step.

What if you find nothing? We do not pad the report with theoretical alerts. If a finding cannot be confirmed, it is not delivered as verified; if findings appear, you receive priority and context to decide.

Already know what you want to analyse? Check the fit before you reserve budget.

Request AI Swarm Pentest
AI Swarm Pentest workflow

Validated attack paths, inside verifiable limits.

The workflow is not another AI model. It is the system of rules, limits, and verification that keeps the engagement inside the agreed mission.

01

Scope agreed in writing

The target and rules of engagement are confirmed before work starts.

02

Traceable evidence

Supporting evidence stays attached to the finding it explains.

03

Engagement limits

Time, resources and access are bounded for a controlled run.

04

Human decision

Your team retains final approval and control of every change.

Questions you'd ask

Questions security teams ask before engaging.

What does AI Swarm Pentest cover?

Your application, API, and source code. Findings are scoped to the target you authorise, with rules of engagement agreed before the run.

What if you find nothing?

We do not pad the report with theoretical alerts. If a finding cannot be reproduced, it is not delivered as verified. If findings appear, you receive priority and context to decide.

How is this different from a scanner or chatbot?

A scanner compares signatures and a chatbot suggests answers. AI Swarm Pentest explores paths, tests hypotheses, and attaches evidence to prioritise what deserves attention.

How do you control the scope?

Before work starts we define the target, authorised environment, test access, and rules of engagement. The agreed boundaries keep the run aligned with that agreement.

How do you verify a finding?

Every finding includes reproducible evidence. If a second pass cannot reproduce the result, the finding is marked unverified or discarded.

Do you modify my production?

Never. Only reviewable proposals, delivered as PRs or separate patch files. Your team decides whether to merge.

Does AI Swarm Pentest replace a human pentester?

It does not remove human judgement. It automates repetitive exploration, correlation, and reproduction while your team retains context, supervision, and the final decision.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

0 / 280

No commitment. If you don't fit, we'll tell you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit
Do you have a recent classic pentest you're not happy with?

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)