


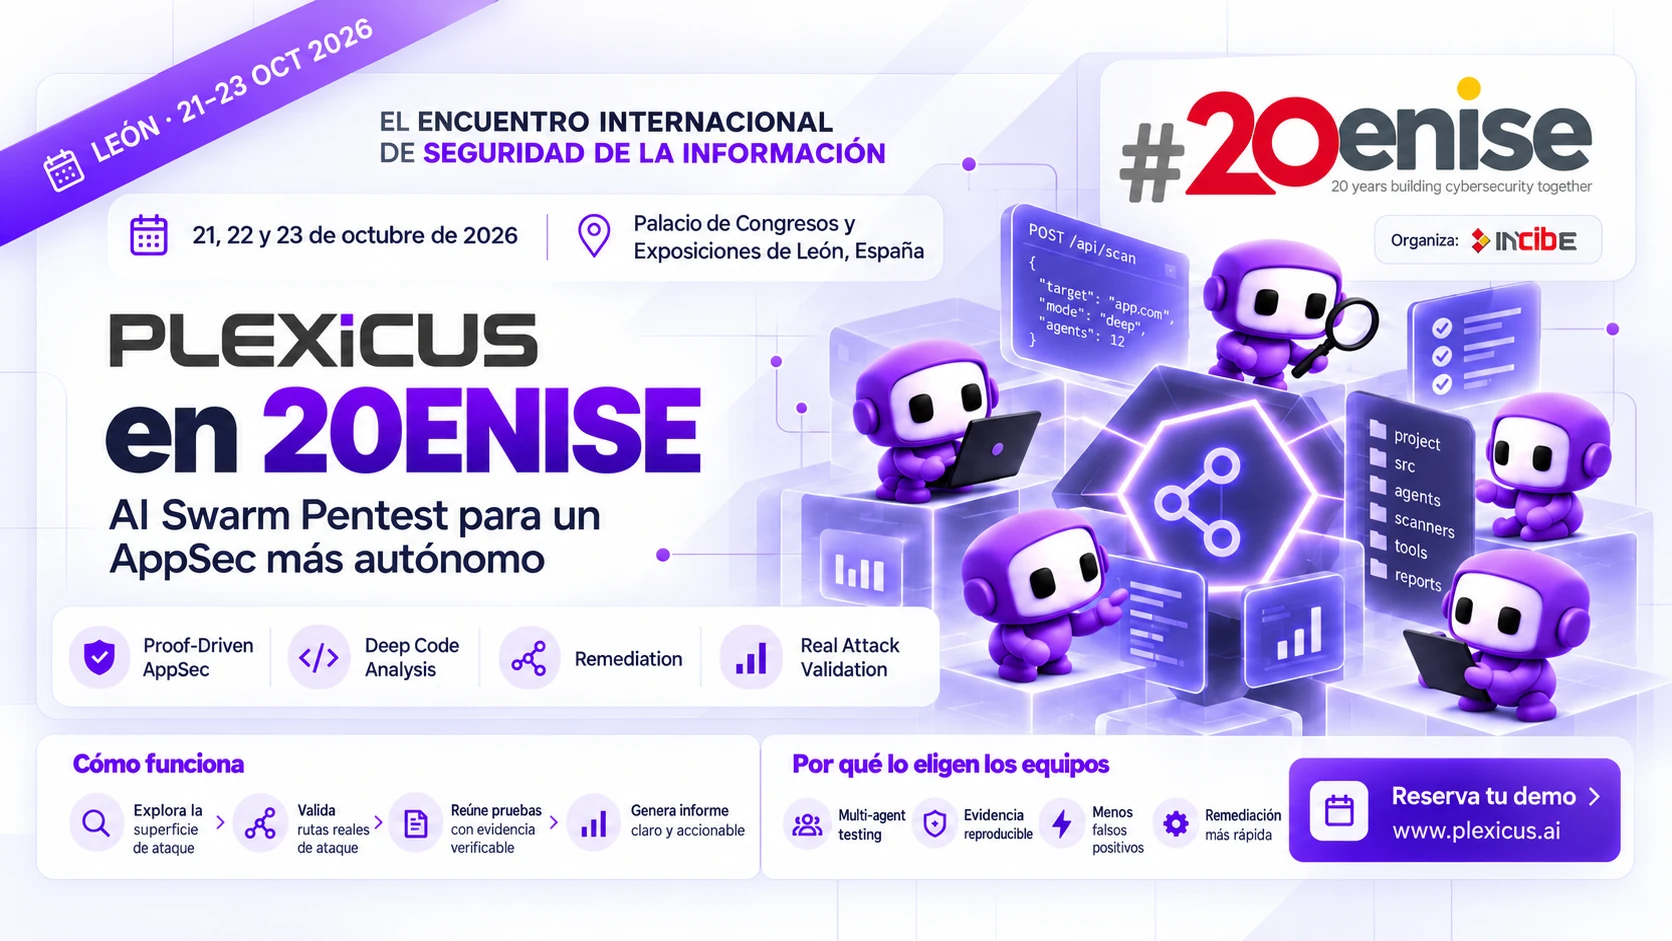
Exhibitor · #20ENISE · León
Visit Plexicus at Stand 148
Live talk at Speakers' Corner 3 · Wed 21 October, 17:20
José Ramón PalancoCEO of Plexicus, S.L.
- Date
- 21–23 October 2026
- Venue
- Palacio de Congresos y Exposiciones, León, Spain
Know what is real. Understand what it affects. Fix it with evidence.
 Cursor
 Copilot
 Claude
 Devin
 Windsurf
 Replit
 Lovable
 Codex
 v0
Trusted by security teams across every codebase


Exhibitor · #20ENISE · León
José Ramón PalancoCEO of Plexicus, S.L.
A guided slice of the Plexicus platform: AI Swarm Pentest explores an authorized attack path, Deep Code Analysis adds context, and Remediation ships a reviewed fix.

What Plexicus has saved you, and what is still on the table.
Validate real risk, understand impact, and remediate with evidence across every codebase.
Evidence attached to every finding.
Code context for every finding.
Reviewed, merge-ready patches.
Plexicus tests your authorized application surface, validates the paths that matter, and hands your team evidence they can review and act on.
Independent checks examine the application, API, and code paths within the agreed scope.
Findings move forward only when the supporting evidence can be reviewed.
Your team receives impact context, remediation guidance, and a reviewer-ready handover.
Scoped with your team. No production changes without review.
Deep Code Analysis
Deep Code Analysis connects code, data flow, and business impact so your team can focus on findings that matter.
Request validation finding
The endpoint accepts user input without the validation the workflow requires. The team can review the evidence and proposed control.
The issue could let an attacker reach an unintended operation. Impact and scope are shown for review.
sample-project · review context
request input Review priority findings against the agreed scope, with supporting evidence and a clear next action.
Drafts a reviewer-ready change for the priority finding, scoped to your team's review workflow.
manual stepcontext clearedreviewer control addedvalidation rule attachedevidence includedhanded back to your teamready for reviewchange returned to reviewerDrafts a remediation for review. Your team decides whether to merge.
Remediation
Plexicus prepares the work — your team owns the merge.
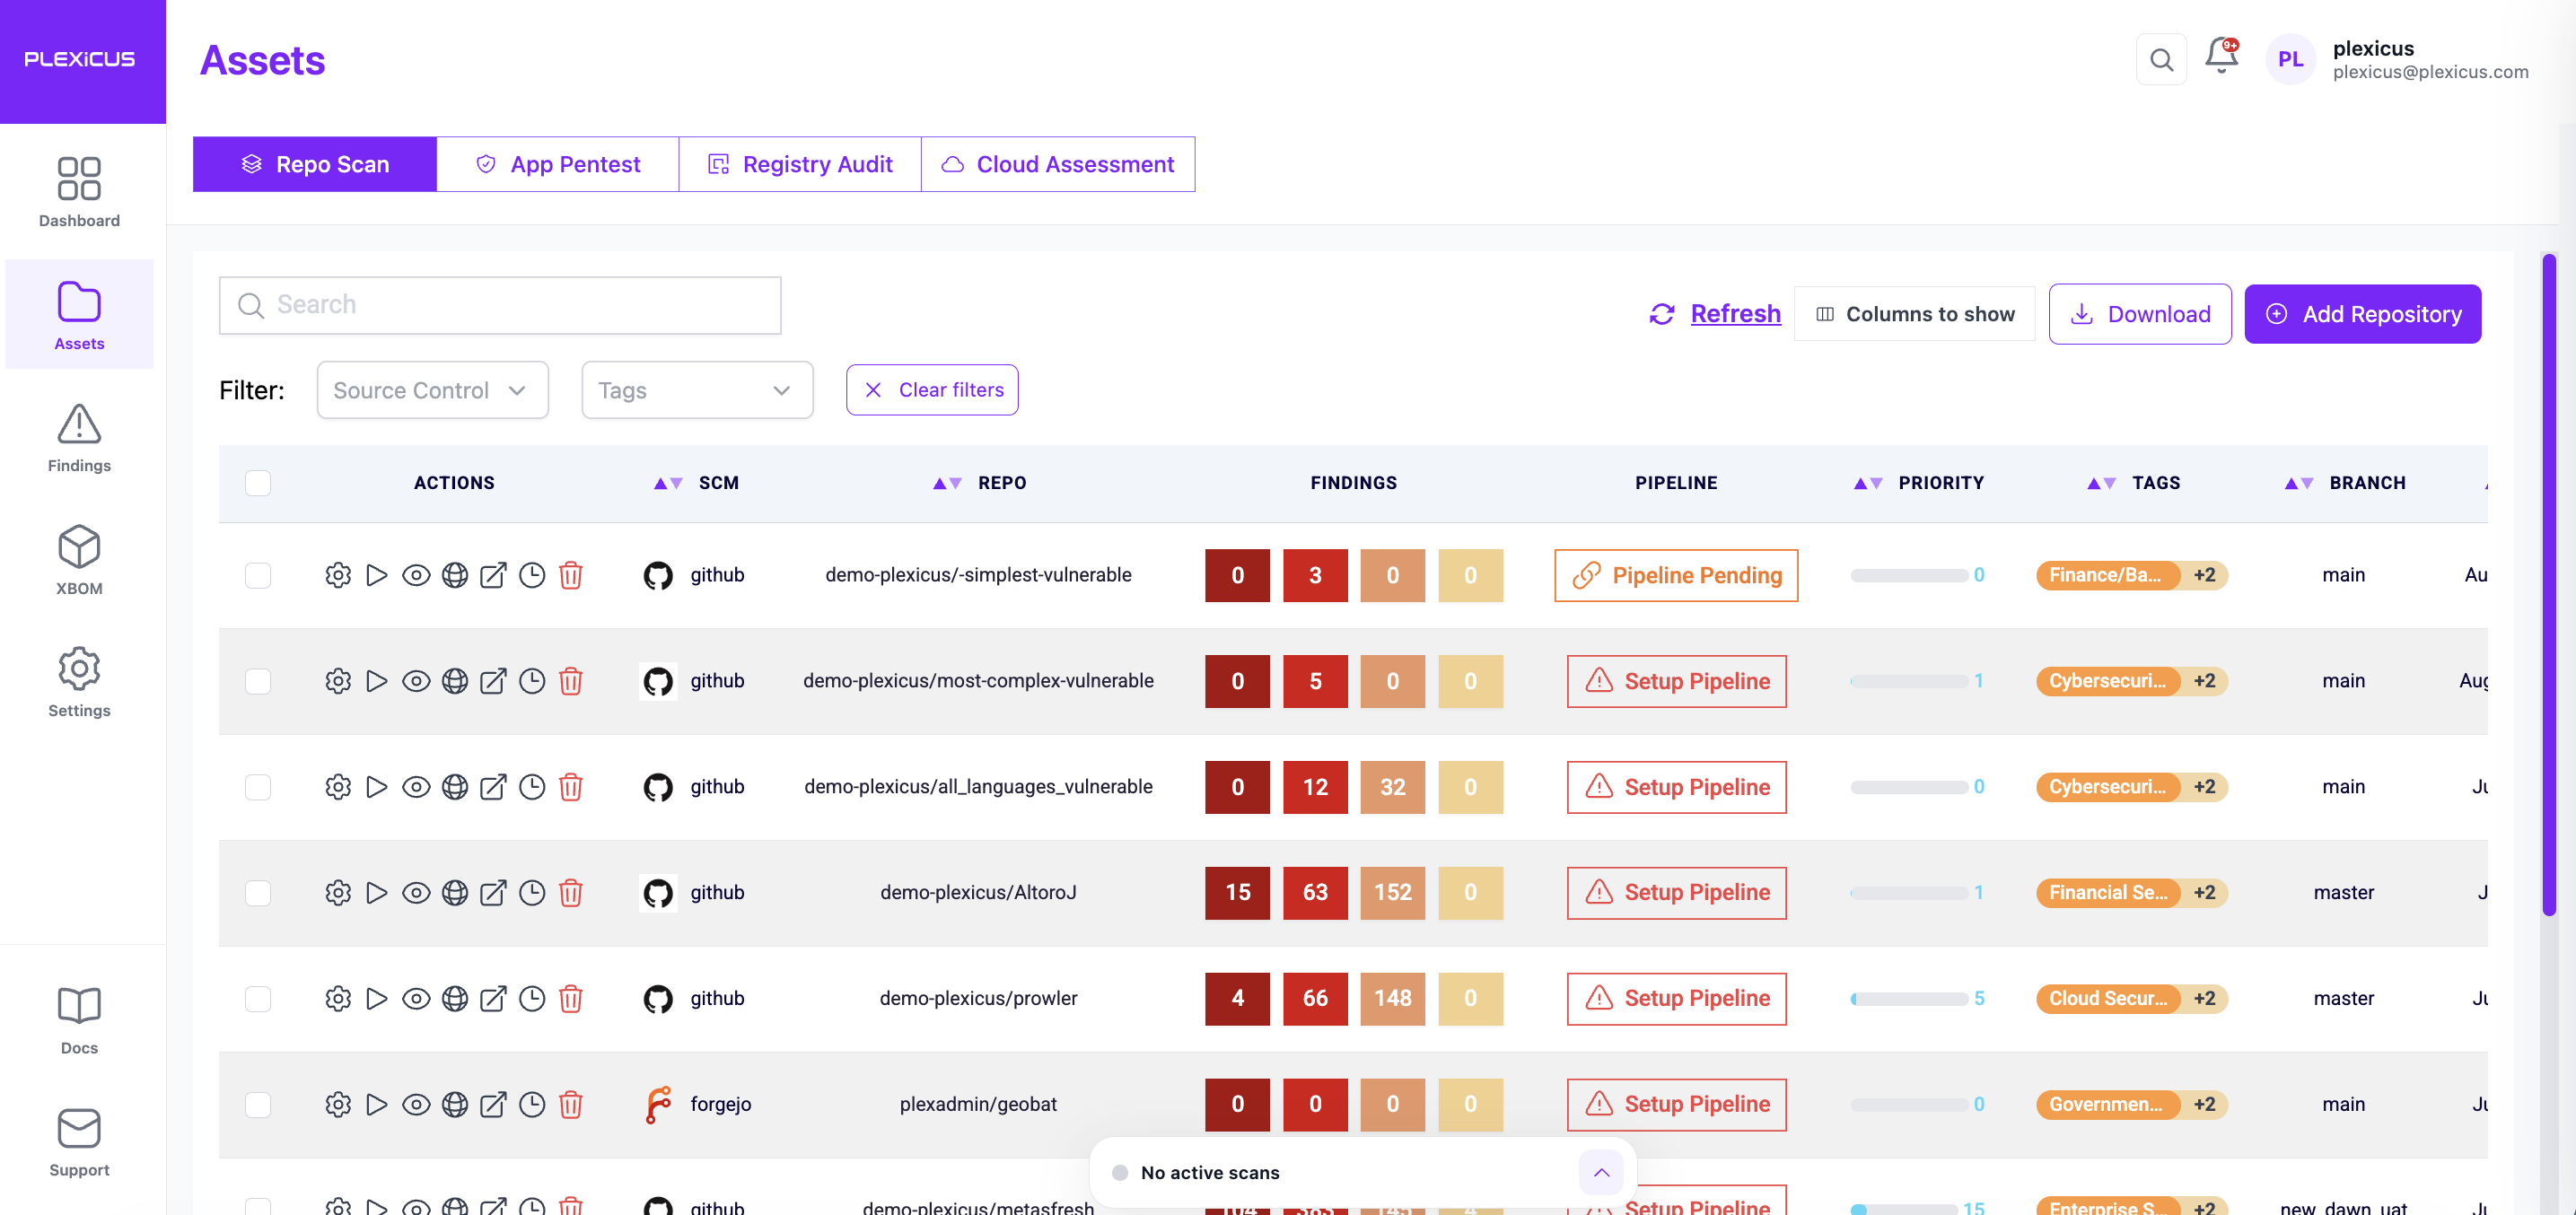
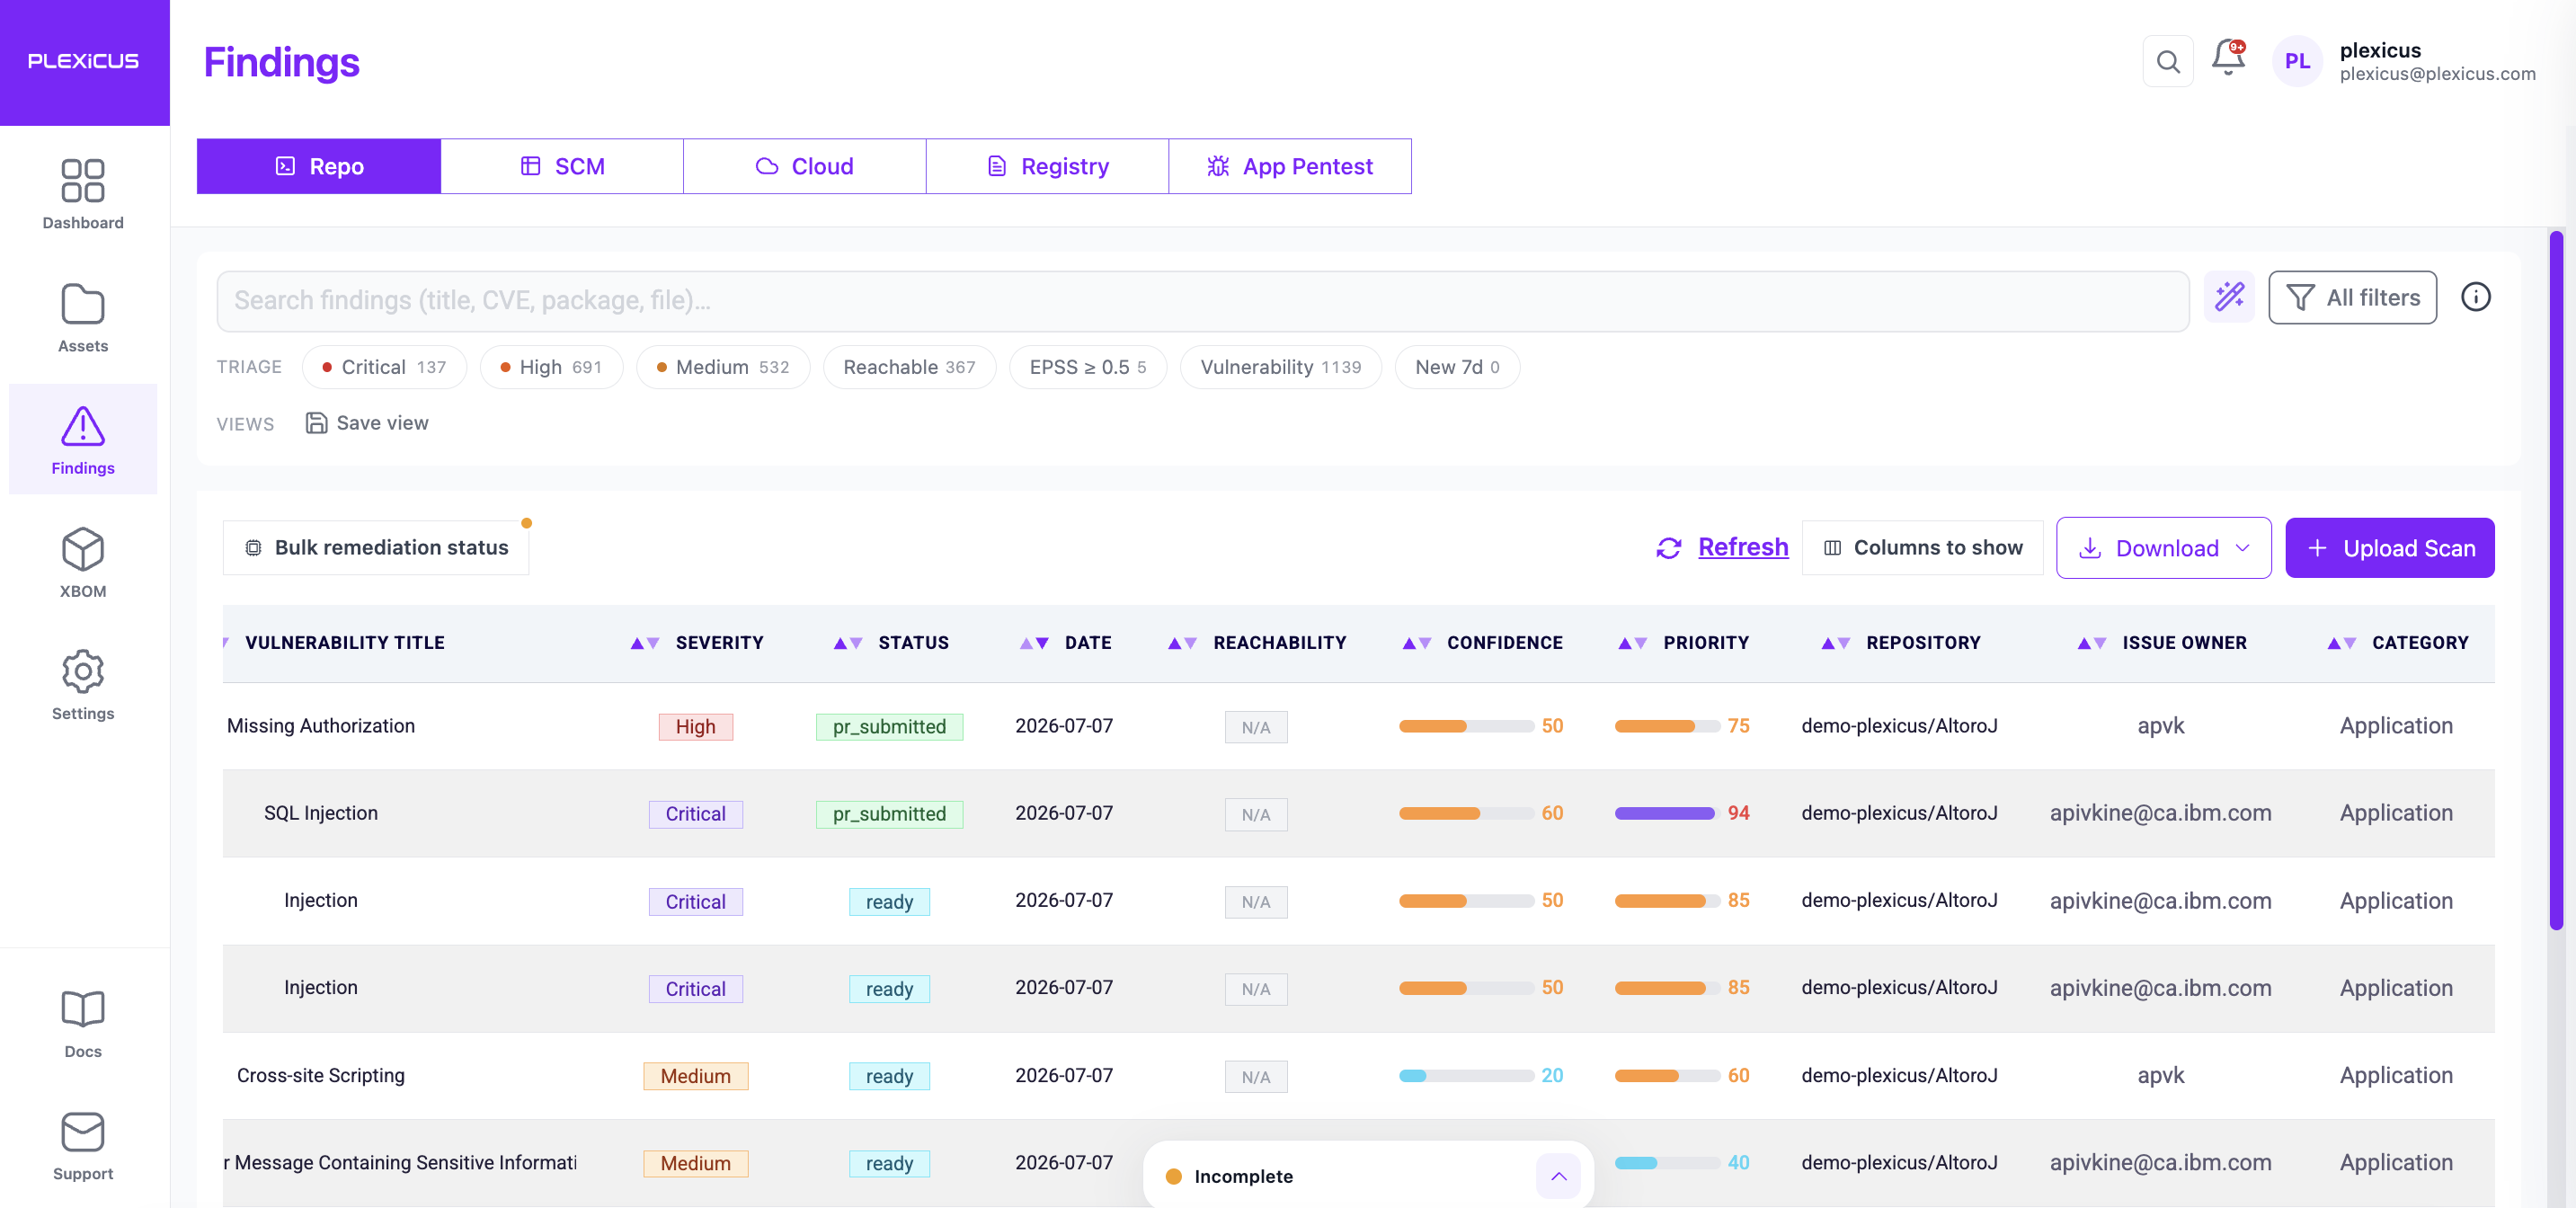
app.plexicus.ai — findings table with severity, status, reachability, confidence, and priority per row.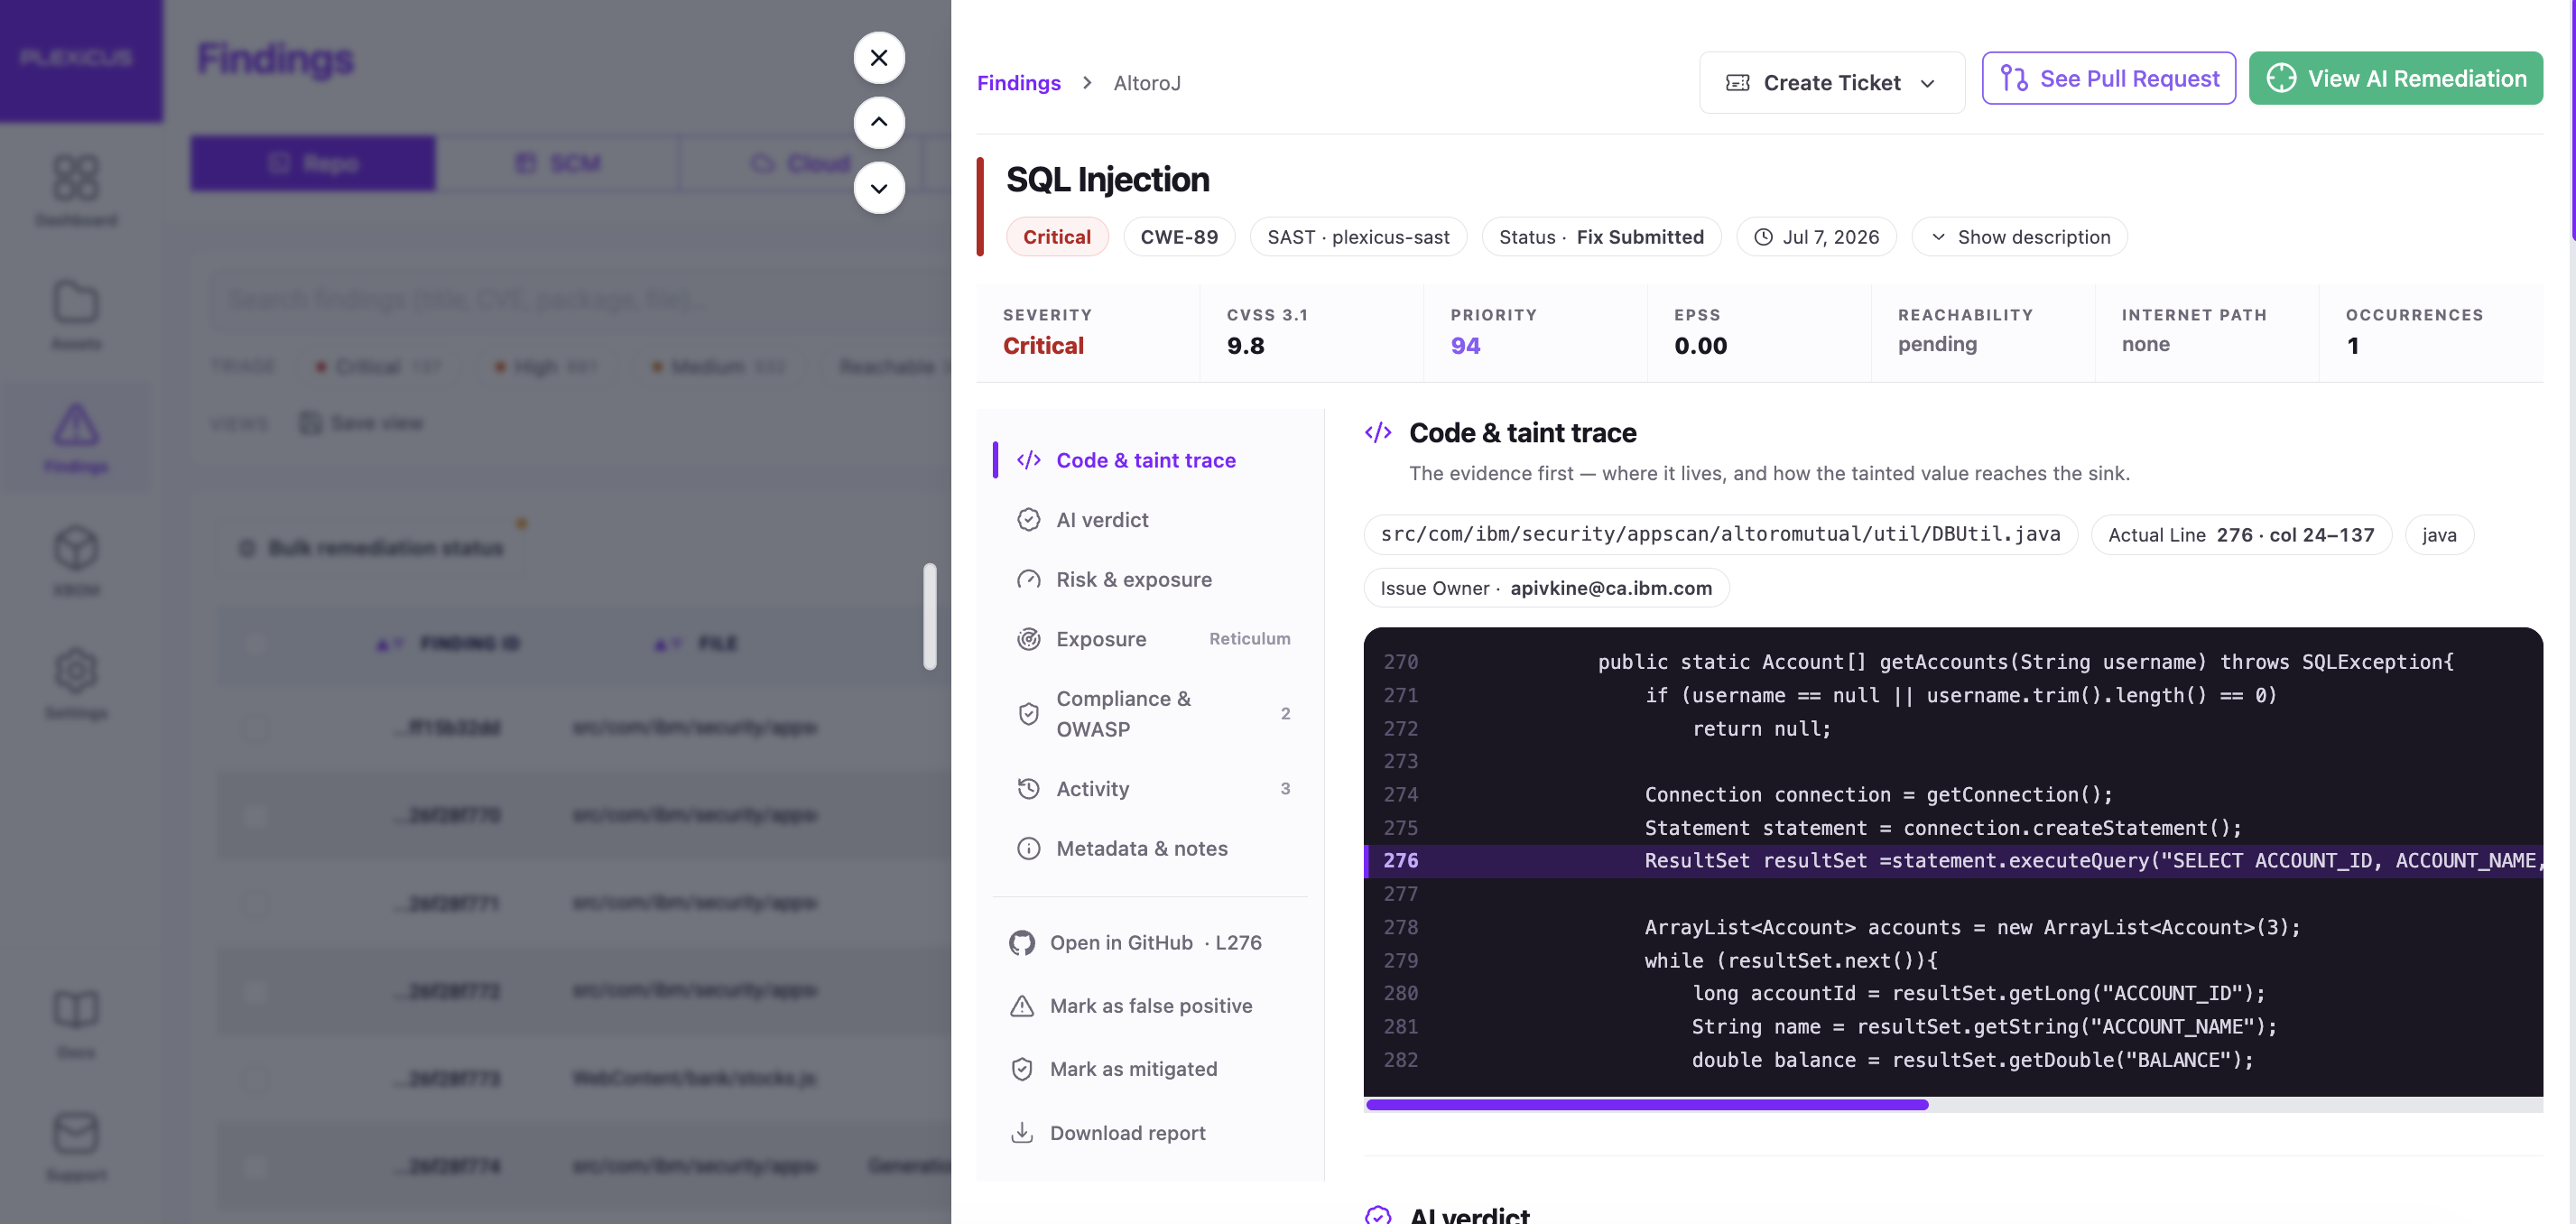
app.plexicus.ai — finding detail with code & taint trace, the evidence first, showing how the tainted value reaches the sink.For the security leader
Evidence chain attached to each closed finding.
SaaS, self-hosted, on-premises, or air-gapped.
Zero data retention. No training on customer code. EU residency by default.
Structured onboarding, custom SLAs, security documentation.
SOC 2 Type II certified. CPSTIC qualification in progress.
Every finding goes straight to a fix, a ticket or an approval the moment it appears. Your team steps in only where judgment matters.

SBOM + CBOM + AIBOM, with VEX statements, watchlists, diffs and CycloneDX / SPDX / PDF export. Built for EU CRA, CISA 2025, PCI DSS 6.3.2 and EU AI Act.
One source
SBOM · CBOM · AIBOM
Changes traced
VEX and inventory diffs
Ready to act
CycloneDX · SPDX · PDF
SBOM, CBOM and AIBOM side by side, with the evidence each component needs.
Cloudflare’s open-source coding-agent skill uses coverage-led hunting, independent validation, and structured evidence. Here is what the workflow can—and cannot—establish.
AI can help analysts navigate compiled software, but a decompiler output is not a vulnerability report. See how REA changes analysis, why reverse- engineering agents need protection, and how teams can validate findings.
An editorial guide to security MCP integrations for AI-assisted development: repository findings, scanning, web testing, supply chain analysis, and cloud security.
Reviews from engineering and security teams using Proof-Driven AppSec.
Plexicus is the most innovative AI-native platform we've evaluated. Their pace of evidence-backed remediation context is what sets them apart.


The AI agent gives our team verified findings with the evidence attached. Our engineers review with confidence instead of chasing noise.

As one of Plexicus's first customers, we've witnessed firsthand how their platform has evolved into an indispensable security solution. Reviewed changes with prioritized context have dramatically reduced our vulnerability management overhead and allowed our security team to focus on strategic initiatives.

Plexicus's powerful vulnerability management allows us at Puffin Security to deliver more advanced cybersecurity services to our clients, creating a perfect security partnership.

Plexicus has streamlined our remediation review process — our team has more hours back every week to focus on the changes that matter.

The integration is seamless, and the reviewed change workflow with full evidence attached has made our security review cycle measurably faster.

Plexicus has become an essential part of our security toolkit. It's like having an expert security engineer available 24/7.

Since implementing Plexicus, we've seen a dramatic improvement in our security posture with less effort from our team. Verified findings with evidence attached are what we wanted from a modern security platform.

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.
