
Tag:

AI generated code

4 articles

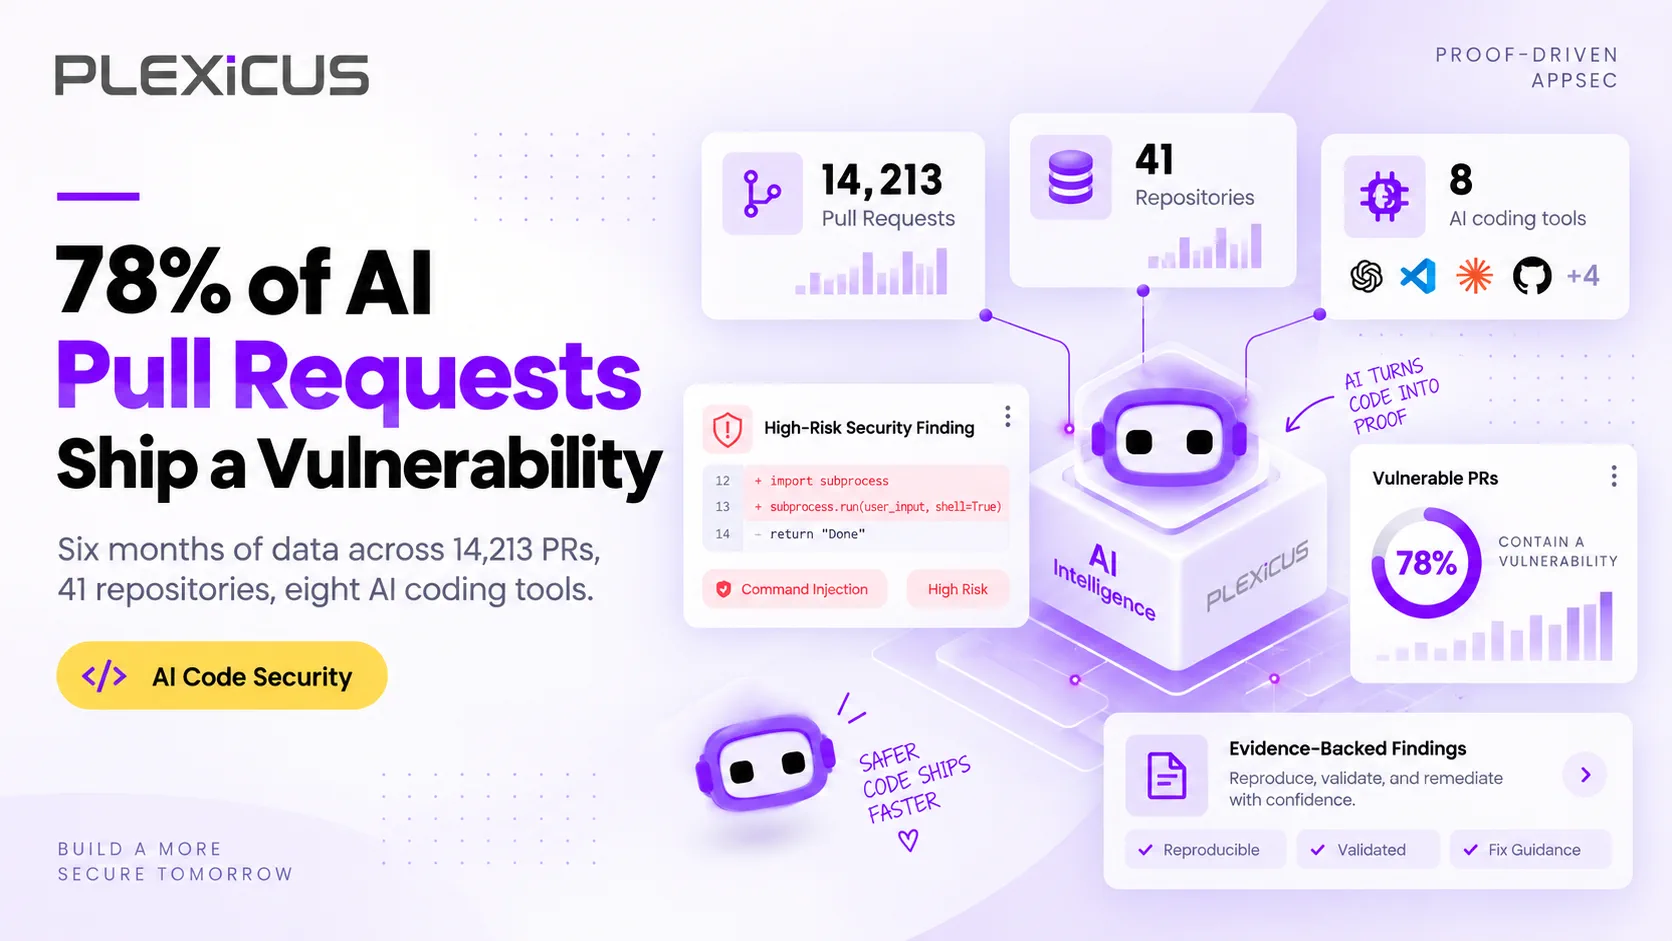
78% of AI-Generated PRs Contain a Vulnerability. Here's What We're Seeing.
AI Code Security

78% of AI-Generated PRs Contain a Vulnerability. Here's What We're Seeing.

Across thousands of AI-generated pull requests scanned in the past six months, 78% contained at least one vulnerability that survived the human review pass. The failure modes are not random. They cluster. Here is the data, the incidents, and what your team can do about it.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Quản trị Bảo mật Vibe Coding: Cách Áp dụng An toàn Codex, Claude Code, Cursor và các Tác nhân Mã AI
Learn

Quản trị Bảo mật Vibe Coding: Cách Áp dụng An toàn Codex, Claude Code, Cursor và các Tác nhân Mã AI

Các công cụ mã AI đang giúp nhà phát triển nhanh hơn — nhưng phát triển nhanh hơn cũng đòi hỏi khả năng hiển thị tốt hơn, quy trình đánh giá mạnh mẽ hơn và khắc phục đáng tin cậy hơn. Đây là hướng dẫn quản trị thực tế cho các nhóm áp dụng Codex, Claude Code, Cursor, Windsurf và các tác nhân mã AI khác.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Bảo mật Vibe Coding: Đảm bảo Mã do AI Tạo ra Trước Khi Đưa vào Sản xuất
Learn

Bảo mật Vibe Coding: Đảm bảo Mã do AI Tạo ra Trước Khi Đưa vào Sản xuất

Các công cụ viết mã AI đang viết gần một nửa tổng số mã mới. Và 45% trong số đó được đưa vào sản xuất với ít nhất một lỗ hổng. Bảo mật vibe coding là hoạt động bảo vệ phần mềm do AI tạo ra — phát hiện, ưu tiên và khắc phục rủi ro trước khi chúng đến môi trường sản xuất.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

Teams with fewer than 50 developers: start a 14-day Trial instead of booking a demo. Start a 14-day Trial →

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)