
When a Critical Finding Lands, the Next Step Is Already Written
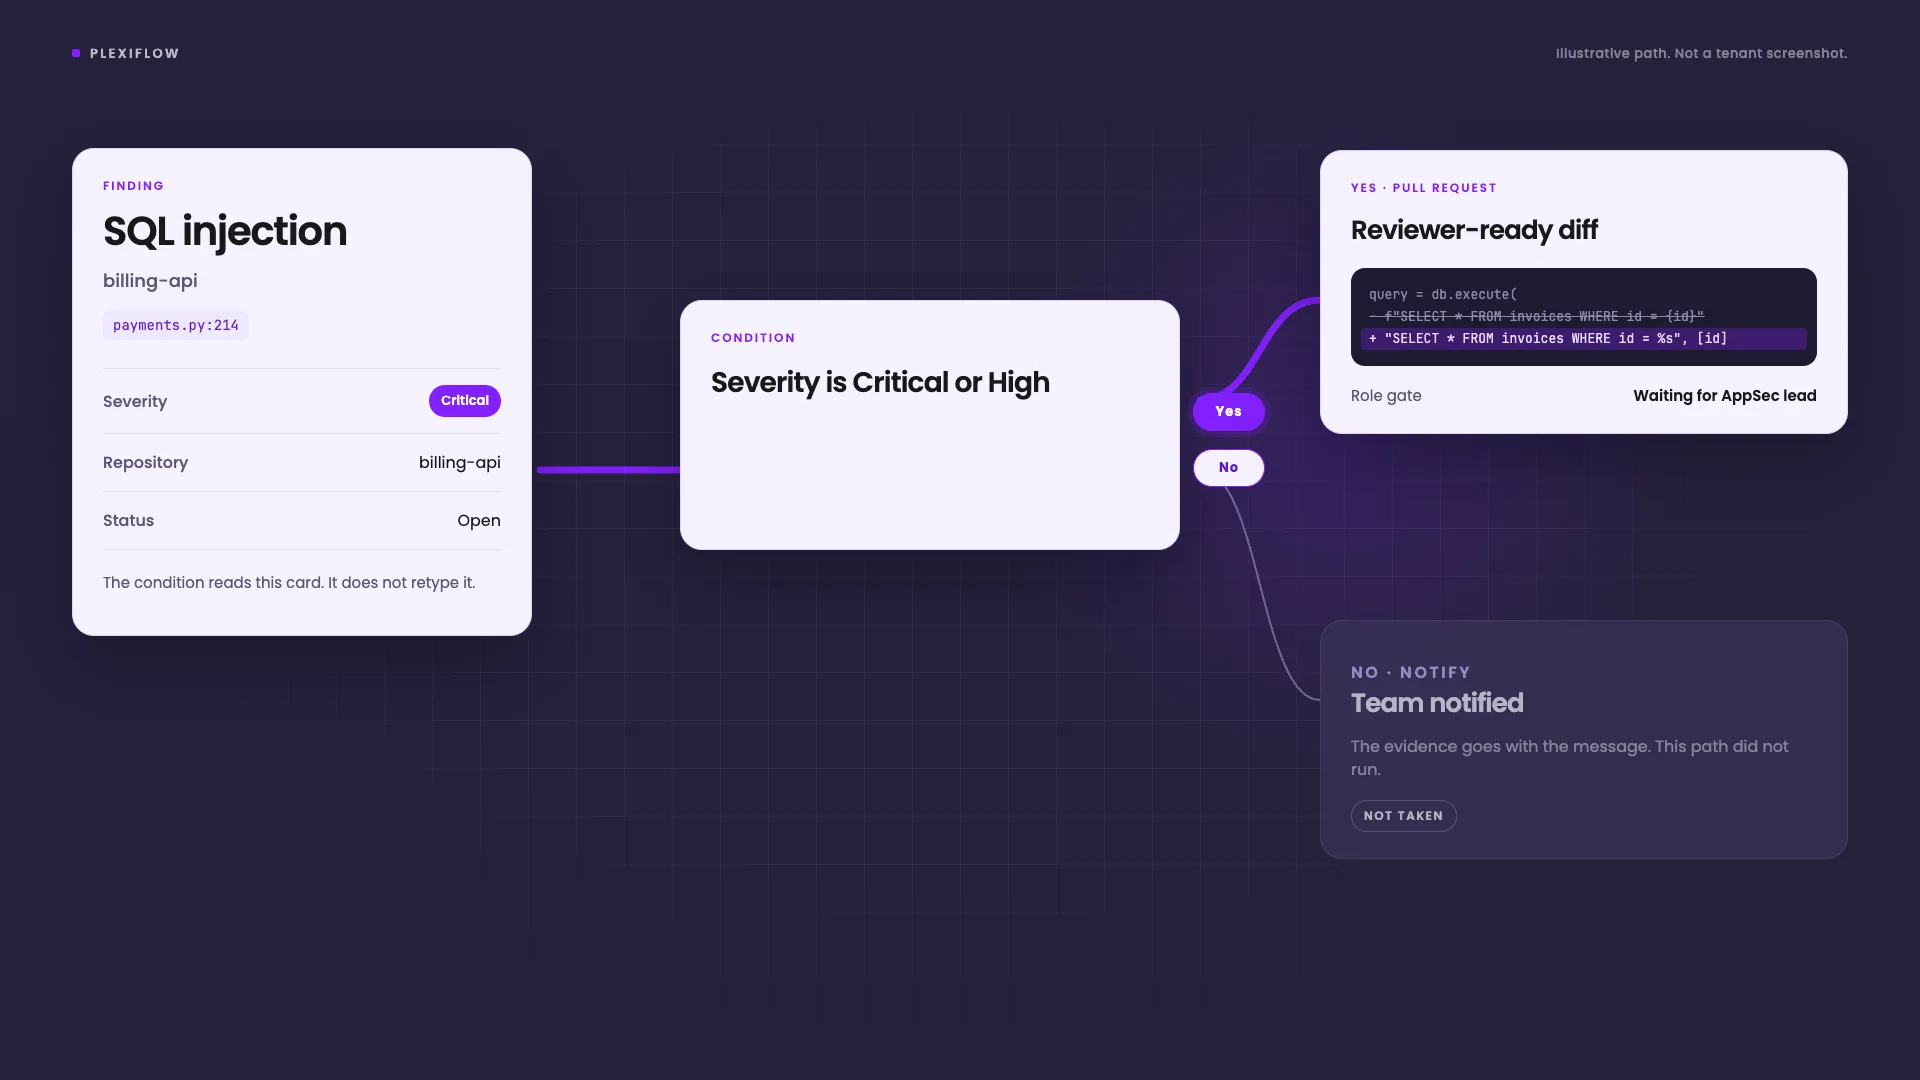
A finding should not wait in a list. PlexiFlow runs the path you already wrote: branch on severity, ask the named role, then start a fix or notify the team.
Josuanstya Lovdianchel is a Business Operations and Product professional with 4+ years of experience spanning product management, growth strategy, and AI-driven automation. He has shipped products end-to-end at scale — most notably at detikcom, Indonesia's largest digital media platform, where he delivered an ERP contributor platform to 100+ users with 100% adoption within one month of launch and led cross-functional teams across Engineering, AI, and Design. A certified Microsoft Azure practitioner with hands-on Python skills, he brings a data-first approach to every problem — from analyzing 10,000+ user reviews to surface product strategy, to building AI-powered notification systems targeting double-digit CTR uplifts. At Plexicus, he applies the same product and automation mindset to business operations, turning complex workflows into scalable systems.
A finding should not wait in a list. PlexiFlow runs the path you already wrote: branch on severity, ask the named role, then start a fix or notify the team.
Open-source AI pentesting has split into distinct categories: autonomous application pentesters, multi-agent orchestration platforms, verification-first agents, and MCP tool layers. We reviewed 10 actively developed projects and explained what each one is genuinely good at.
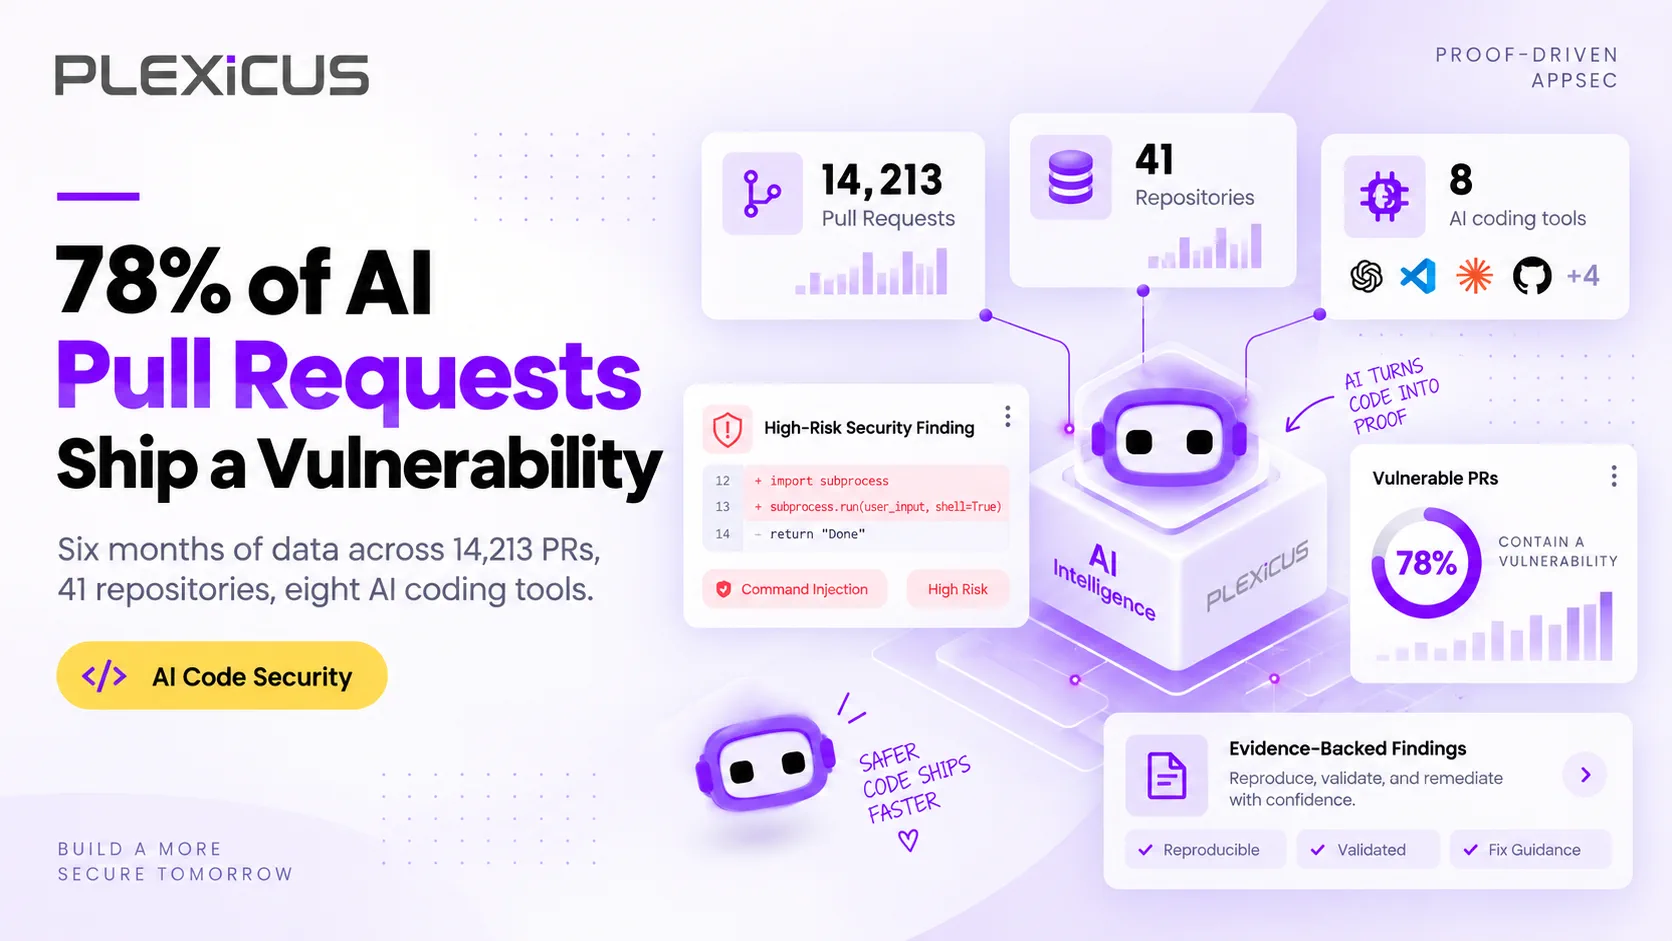
78% of 14,213 AI-assisted pull requests we scanned contained a vulnerability that survived human review. Here is how we measured it, the flaw classes, and what fixes it.
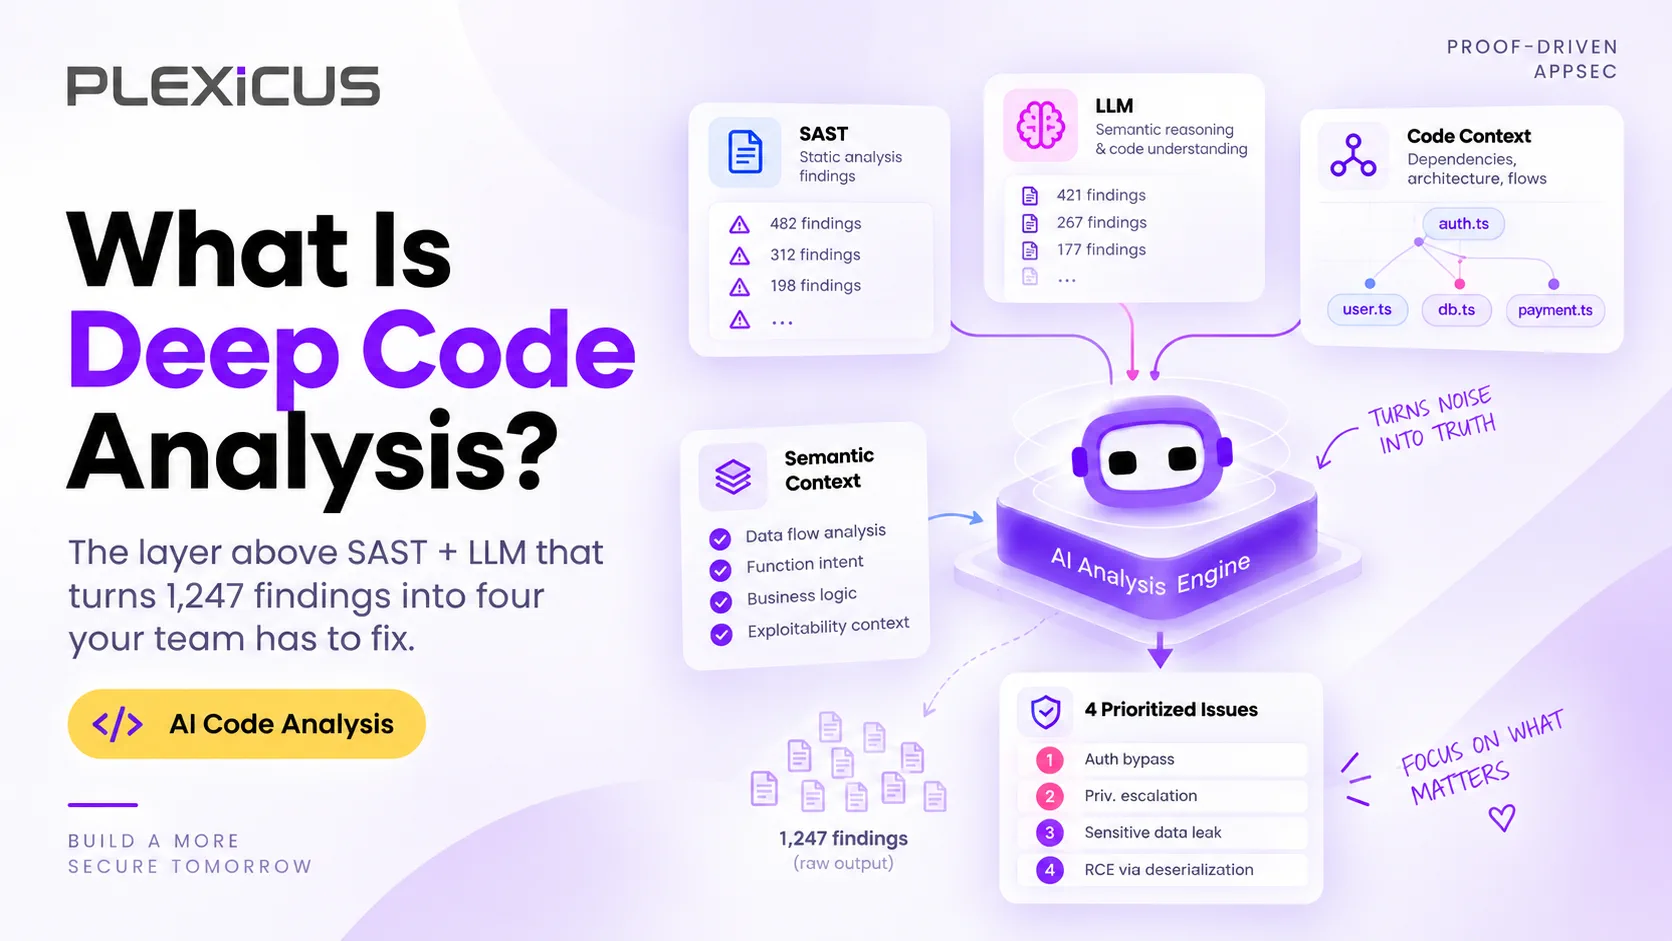
SAST false positives bury real bugs, and an LLM wrapper does not fix that. Deep Code Analysis uses reachability analysis to prove which findings are real, reachable, and worth fixing.
AI 编码工具正让开发者变得更快——但更快的开发也需要更好的可见性、更强的审查工作流以及更可靠的修复措施。这是一份面向采用 Codex、Claude Code、Cursor、Windsurf 及其他 AI 编码代理的团队的实用治理指南。
仅靠检测已无法跟上AI驱动的开发速度。AI原生修复是下一层防线——帮助团队在SDLC的每个阶段修复、验证并追踪AI生成代码中的漏洞。
AI 编码工具正在编写近一半的新代码。其中 45% 的代码在发布时至少包含一个漏洞。Vibe Coding 安全是一种保护由 AI 创建的软件安全的实践——在风险到达生产环境前进行检测、优先级排序和修复。
Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.