Dependabot Can Update AI Agent Skills. Who Reviews What Changed?
Dependabot can propose version updates for agent dependencies. The change puts skills and instructions into an existing review workflow.
José Ramón Palanco is the CEO/CTO of Plexicus, a pioneering company in ASPM (Application Security Posture Management) launched in 2024, offering AI-powered remediation capabilities. Previously, he founded Dinoflux in 2014, a Threat Intelligence startup that was acquired by Telefonica, and has been working with 11paths since 2018. His experience includes roles at Ericsson`s R&D department and Optenet (Allot). He holds a Telecommunications Engineering degree from the University of Alcala de Henares and a Master`s in IT Governance from the University of Deusto. As a recognized cybersecurity expert, he has been a speaker at various prestigious conferences including OWASP, ROOTEDCON, ROOTCON, MALCON, and FAQin. His contributions to the cybersecurity field include multiple CVE publications and the development of various open source tools such as nmap-scada, ProtocolDetector, escan, pma, EKanalyzer, SCADA IDS, and more.
Dependabot can propose version updates for agent dependencies. The change puts skills and instructions into an existing review workflow.
A GitHub Actions policy change puts privileged pull request workflows under scrutiny. Here is what maintainers can do before enforcement.
An internal DeepSeek evaluation separates exploit capability from operational restraint. Define scope, evidence and cleanup before autonomous testing.
Separate PHP runtime exposure from application findings, verify worker replacement and keep remediation evidence reviewable with Plexicus.
EMBRACE is a useful reminder that an embedded browser does not automatically keep the security boundaries of a standalone browser.
Turn AI security benchmark claims into a scoped evaluation with reproducible findings, reviewed patches and deployment retests.
A source review of three high-severity n8n alerts shows why scan provenance and credential context matter before declaring a leak.
Review browser-loaded scripts, test integrity controls and retain deployment evidence after the Convertr analytics-script incident.
Map embedded Wasmtime dependencies to shipped artifacts, choose the correct advisory fix and verify rebuilt deployments with a Plexicus evidence workflow.
A practical evidence workflow for testing authorization boundaries, connecting code context to impact, and reviewing remediation with Plexicus.
Quantum readiness starts with knowing where cryptography lives. Singapore’s 2026 milestones make discovery urgent, while SBOMs alone cannot show every algorithm, runtime setting or supplier dependency that may need a migration plan.
Cloudflare’s open-source coding-agent skill uses coverage-led hunting, independent validation, and structured evidence. Here is what the workflow can—and cannot—establish.
AI can help analysts navigate compiled software, but a decompiler output is not a vulnerability report. See how REA changes analysis, why reverse- engineering agents need protection, and how teams can validate findings.
Three systems asserted a condition and none of them checked whether it still held. A registry reported a package was attested. An evaluation harness reported a model was offline. An assistant reported a package would work.
An editorial guide to security MCP integrations for AI-assisted development: repository findings, scanning, web testing, supply chain analysis, and cloud security.
How specialized attack agents share context, challenge hypotheses, and independently verify attack paths inside the Plexicus Proof-Driven AppSec workflow.
A complete guide to application security in 2026, from secure design and software supply chains to testing, exploit validation, remediation, and Proof-Driven AppSec.
A fruit-fly connectome offers a vivid test of a security principle: a demo is not proof until controls show what the advertised system contributes.
DevDay 2026 connected persistent agents, cloud coding, plugins, events, and shared work. Here is what shipped, what is still coming, and where AppSec boundaries lie.
Opus 5.5 motion-graphics demos reveal an agentic loop: plan, write code, run it, inspect, revise. Claude cybersecurity now depends on verification keeping pace.
Jev AI returns typed decisions instead of prose. That could change where semantic judgment fits in security workflows, if teams keep policy, fallbacks, verification, and human review.
MAESTRO is the Cloud Security Alliance's 7-layer framework for agentic AI threat modeling, applied by the OWASP GenAI Security Project. This guide turns each layer into a pentest checklist.
AI penetration testing in 2026 splits into three lanes: autonomous pentest agents, BAS platforms and AI-assisted PTaaS. We compared 15 tools on signed-scope evidence, replay and pricing.
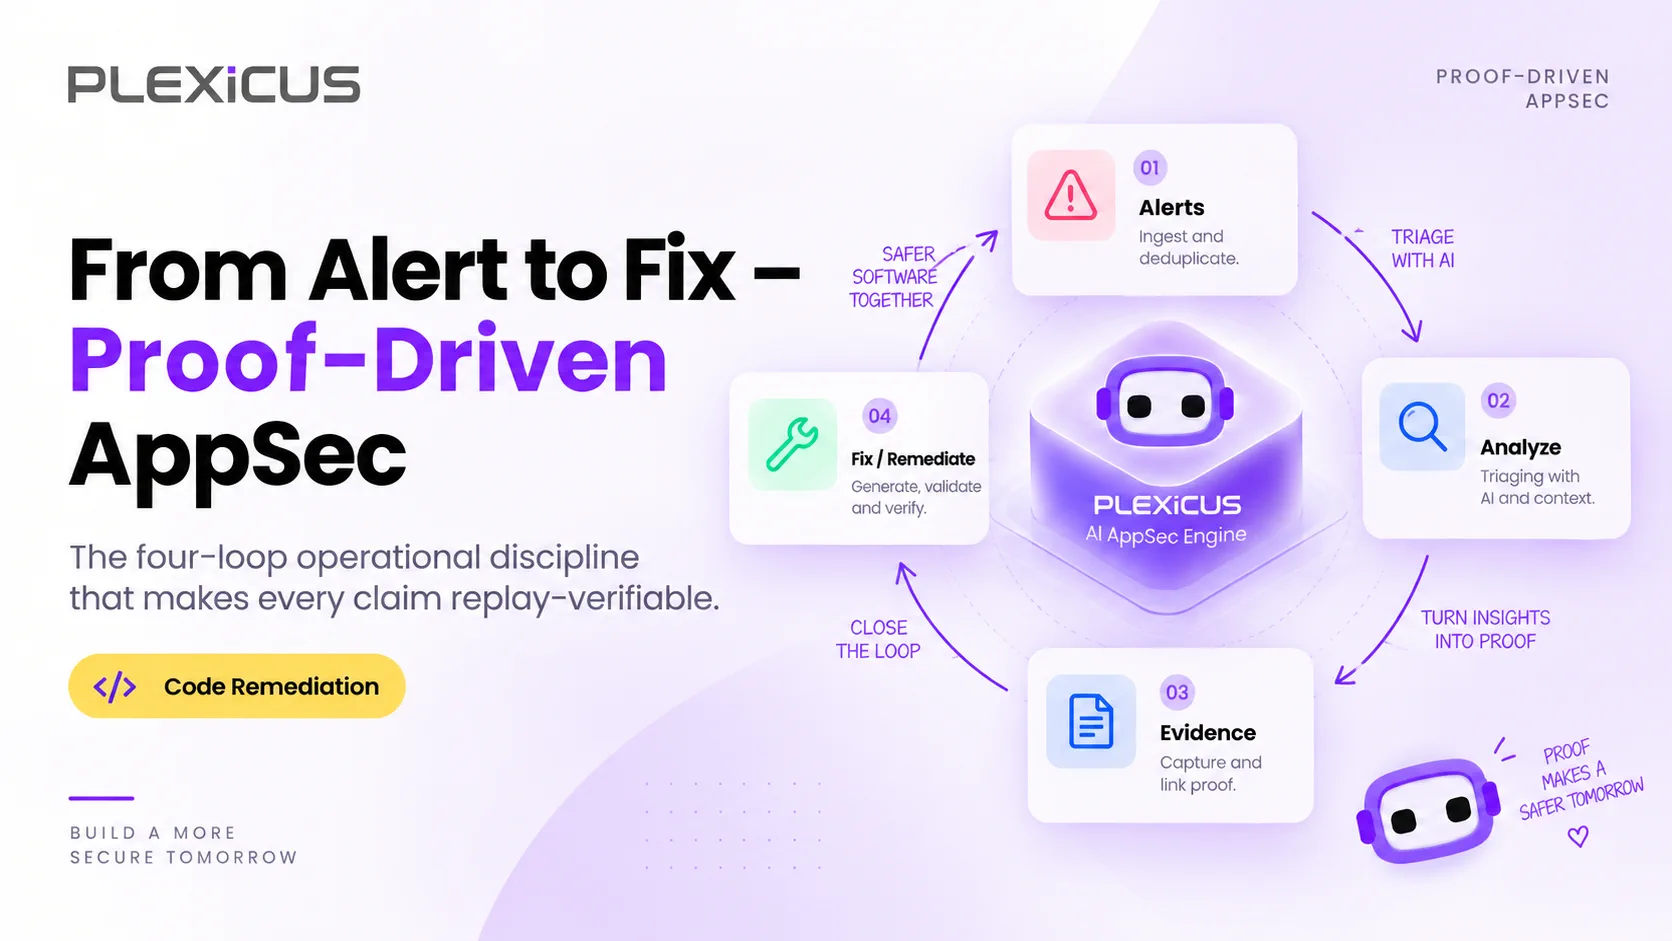
Proof-Driven AppSec is a vulnerability remediation process that closes the loop from alert to merged fix once, with replayable evidence at every step: detect, verify, fix, audit.
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.
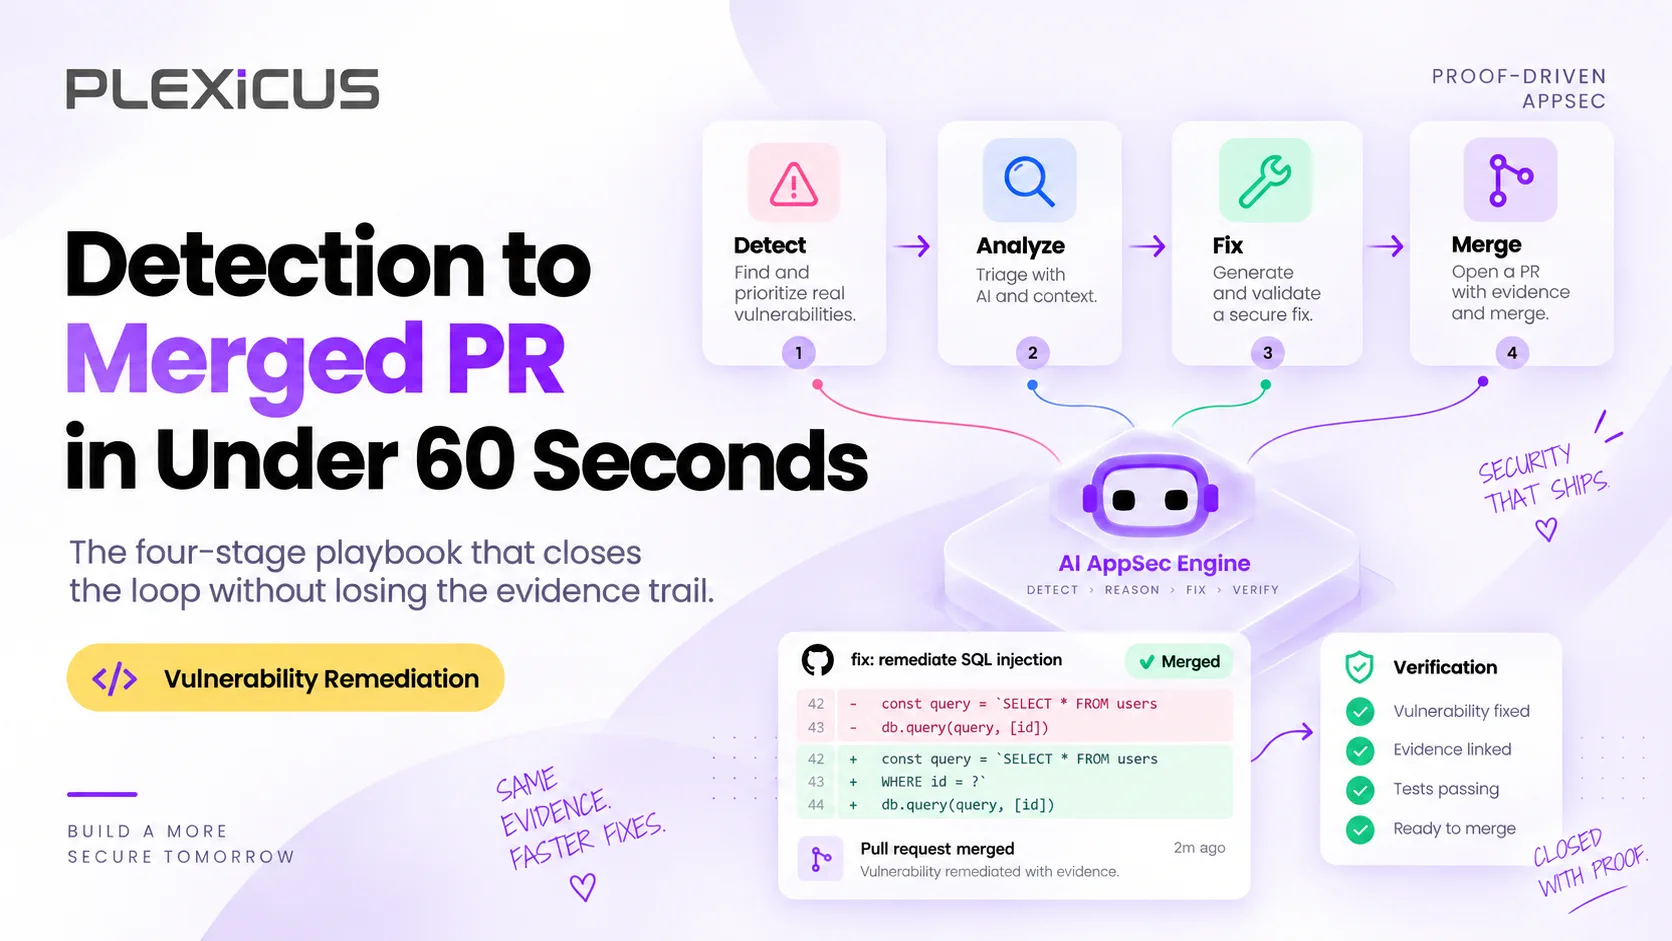
A four-step automated vulnerability remediation playbook that turns a verified finding into a tested, reviewer-ready PR in under 60 seconds, with the evidence attached.
تشغيل `trivy image` ليس DevSecOps—إنه توليد ضوضاء. الهندسة الأمنية الحقيقية تتعلق بنسبة الإشارة إلى الضوضاء. يوفر هذا الدليل تكوينات جاهزة للإنتاج لـ 17 أداة قياسية في الصناعة لوقف الثغرات دون إيقاف الأعمال، منظمة في ثلاث مراحل: ما قبل الالتزام، حراس بوابة CI، وفحص وقت التشغيل.
تثبيت أداة الأمان هو الجزء السهل. يبدأ الجزء الصعب في 'اليوم الثاني'، عندما تقوم تلك الأداة بالإبلاغ عن 5000 ثغرة جديدة. يركز هذا الدليل على إدارة الثغرات: كيفية تصفية التنبيهات المكررة، وإدارة الإيجابيات الكاذبة، وتتبع المقاييس التي تقيس النجاح فعليًا. تعلم كيفية الانتقال من 'العثور على الأخطاء' إلى 'إصلاح المخاطر' دون إرهاق فريقك.
SAST و DAST هما طرق اختبار أمان تُستخدم لحماية التطبيقات من الهجمات. لمعرفة كيف يساعد كل منهما في أمان التطبيقات، دعونا نلقي نظرة على اختلافاتهما وأين يتناسبان في سير عملك
قارن بين أدوات ASPM الرائدة مثل Plexicus وCycode وWiz وApiiro لأتمتة اختبار أمان التطبيقات وإدارة الثغرات الأمنية
اكتشف أفضل أدوات أمان API للكشف عن الثغرات، وقف هجمات API، وحماية تطبيقاتك من خلال الفحص والاختبار المتقدم.
تعتمد التطبيقات الحديثة بشكل كبير على المكتبات الخارجية والمفتوحة المصدر. هذا يسرع من عملية التطوير، ولكنه يزيد أيضًا من خطر الهجمات. كل تبعية يمكن أن تقدم مشاكل مثل الثغرات الأمنية غير المرقعة، التراخيص الخطرة، أو الحزم القديمة. تساعد أدوات تحليل تكوين البرمجيات (SCA) في معالجة هذه المشاكل.
هناك العشرات من أدوات SAST في السوق، تتراوح من مفتوحة المصدر إلى مستوى المؤسسات. التحدي هو: أي أداة SAST هي الأفضل لفريقك؟
أمن تطبيقات الويب ضروري لحماية تطبيقاتك من الهجمات السيبرانية التي تستهدف البيانات الحساسة وتعرقل العمليات. يغطي هذا الدليل أهمية أمن تطبيقات الويب، الثغرات الشائعة، أفضل الممارسات وطرق الاختبار، مما يساعدك على تأمين تطبيقك، ضمان الامتثال والحفاظ على ثقة المستخدمين
أصبح اختراق الأمان الكابوسي حقيقة للعديد من الشركات الأوروبية. تعرف على 15 اتجاهًا تحويليًا في DevSecOps يجب أن تعرفها لتبقى بعيدًا عن قائمة الاختراقات.
تخرج Plexicus من برنامج تسريع Startup Wise Guys دفعة الربيع 2025.
إذا كنت تقوم ببناء أو تشغيل برامج اليوم، فمن المحتمل أنك تتعامل مع الخدمات المصغرة، والوظائف الخالية من الخوادم، والحاويات، والحزم الخارجية، وكم هائل من مربعات الامتثال. كل جزء متحرك يولد نتائجه الخاصة، ولوحات المعلومات، والتنبيهات الحمراء الغاضبة. قبل فترة طويلة، يصبح وضوح المخاطر مثل القيادة في ضباب سان فرانسيسكو في الساعة 2 صباحًا - تعرف أن الخطر موجود، لكن لا يمكنك رؤيته بوضوح.
حصلت بليكسيكوس على استثمار بقيمة 150,000 دولار من مايكروسوفت لتوسيع بنيتها التحتية السحابية. سيساهم هذا التمويل في تحسين أداء النظام وقابليته للتوسع والموثوقية، مما يمكن بليكسيكوس من دعم المزيد من الشركات بحلول مؤسسية مدعومة بالذكاء الاصطناعي.
اكتشف كيف يعزز تكامل BlackDuck الجديد في Plexicus أمان المصادر المفتوحة من خلال الكشف عن الثغرات الأمنية في الوقت الفعلي، وأتمتة تحديد أولويات المخاطر، وتدفقات عمل DevSecOps السلسة.
تطلق بليكسيكوس منصة أمنية مدعومة بالذكاء الاصطناعي لمعالجة الثغرات الأمنية في الوقت الحقيقي. تكتشف الوكلاء المستقلون التهديدات وتحدد أولوياتها وتصلحها فورًا.
تعاون جديد بين بليكيسوس وسيفيروس يهدف إلى تعزيز أمن التطبيقات في 19 دولة في أمريكا اللاتينية وإيبيريا. يجلب هذا التعاون في مجال الأمن السيبراني حلول إدارة وضعية أمن التطبيقات المتقدمة (ASPM) إلى المنظمات التي تسعى للدفاع بشكل استباقي ضد التهديدات السيبرانية.
تعتبر الأطر مثل DORA وISO 27001 وNIST SP 800-53 أساسية لإدارة وضع أمان التطبيقات القوية، حيث تساعد المؤسسات على تلبية المعايير وتقليل المخاطر والحفاظ على الامتثال التنظيمي.
Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.