FREE TOOL

Free SAST Tool
for secure code scanning.

Scan your GitHub source code to detect security vulnerabilities — and review AI-suggested context for each finding. No storage. No AI training. 100% free.

See a sample report

No Credit Card Required. Zero Config

Read docs
  • Fast static-analysis scans
  • 20+ languages & frameworks
  • No code stored
  • No AI training
  • Free forever, no credit card
3 STEPS

Run a Security Code Scan

Step 1

Connect your GitHub repository

Sign in and authorize read-only access in one click.

Step 2

Run a Security Code Scan

Our static analysis engine checks your source code for vulnerabilities.

Step 3

Get a Report

Instantly see vulnerabilities with severity levels, CVE details, and priorities to fix
RESULTS

What You’ll Get From Your Free Code Vulnerability Scan

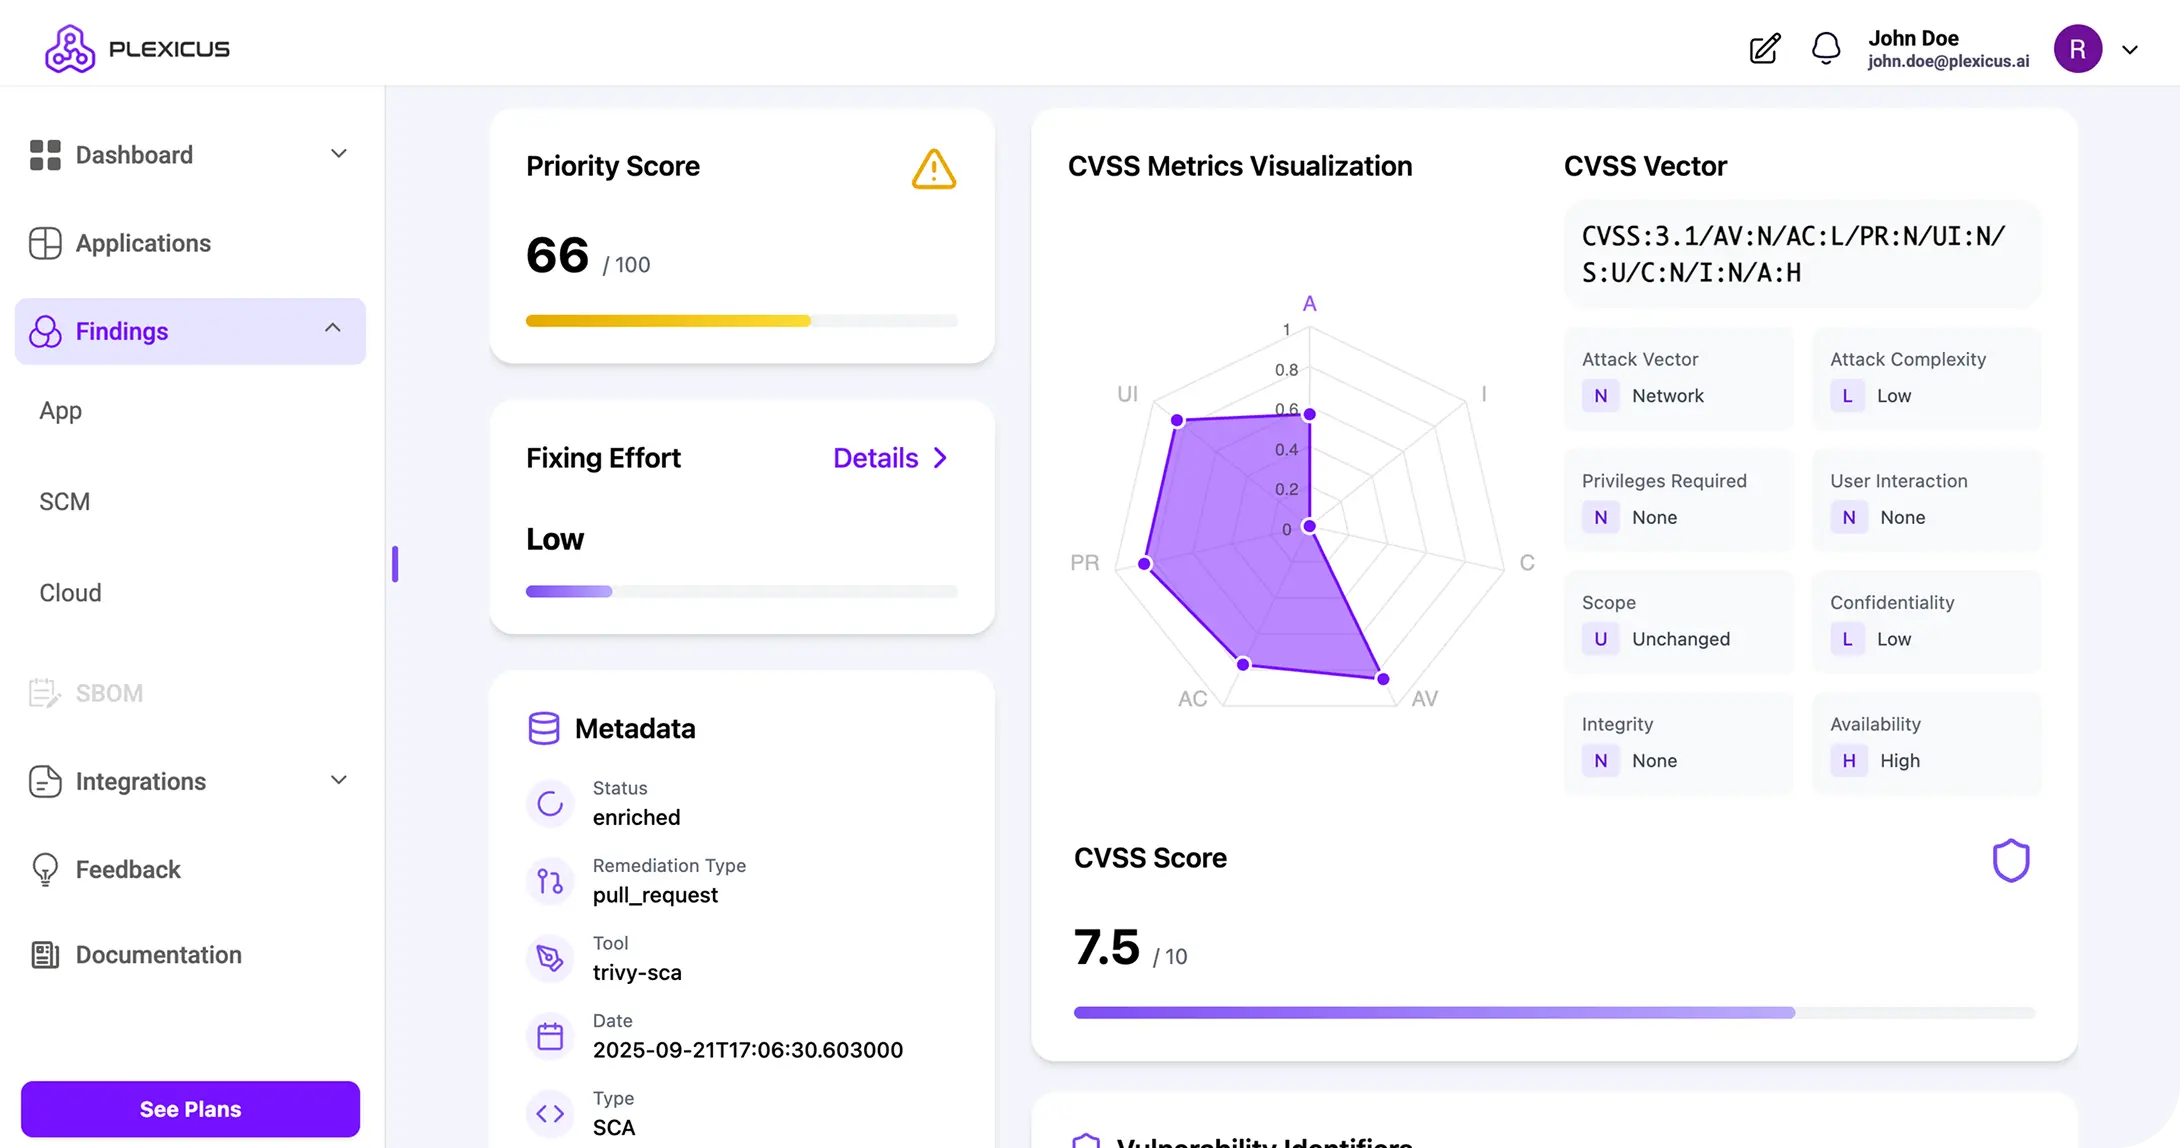
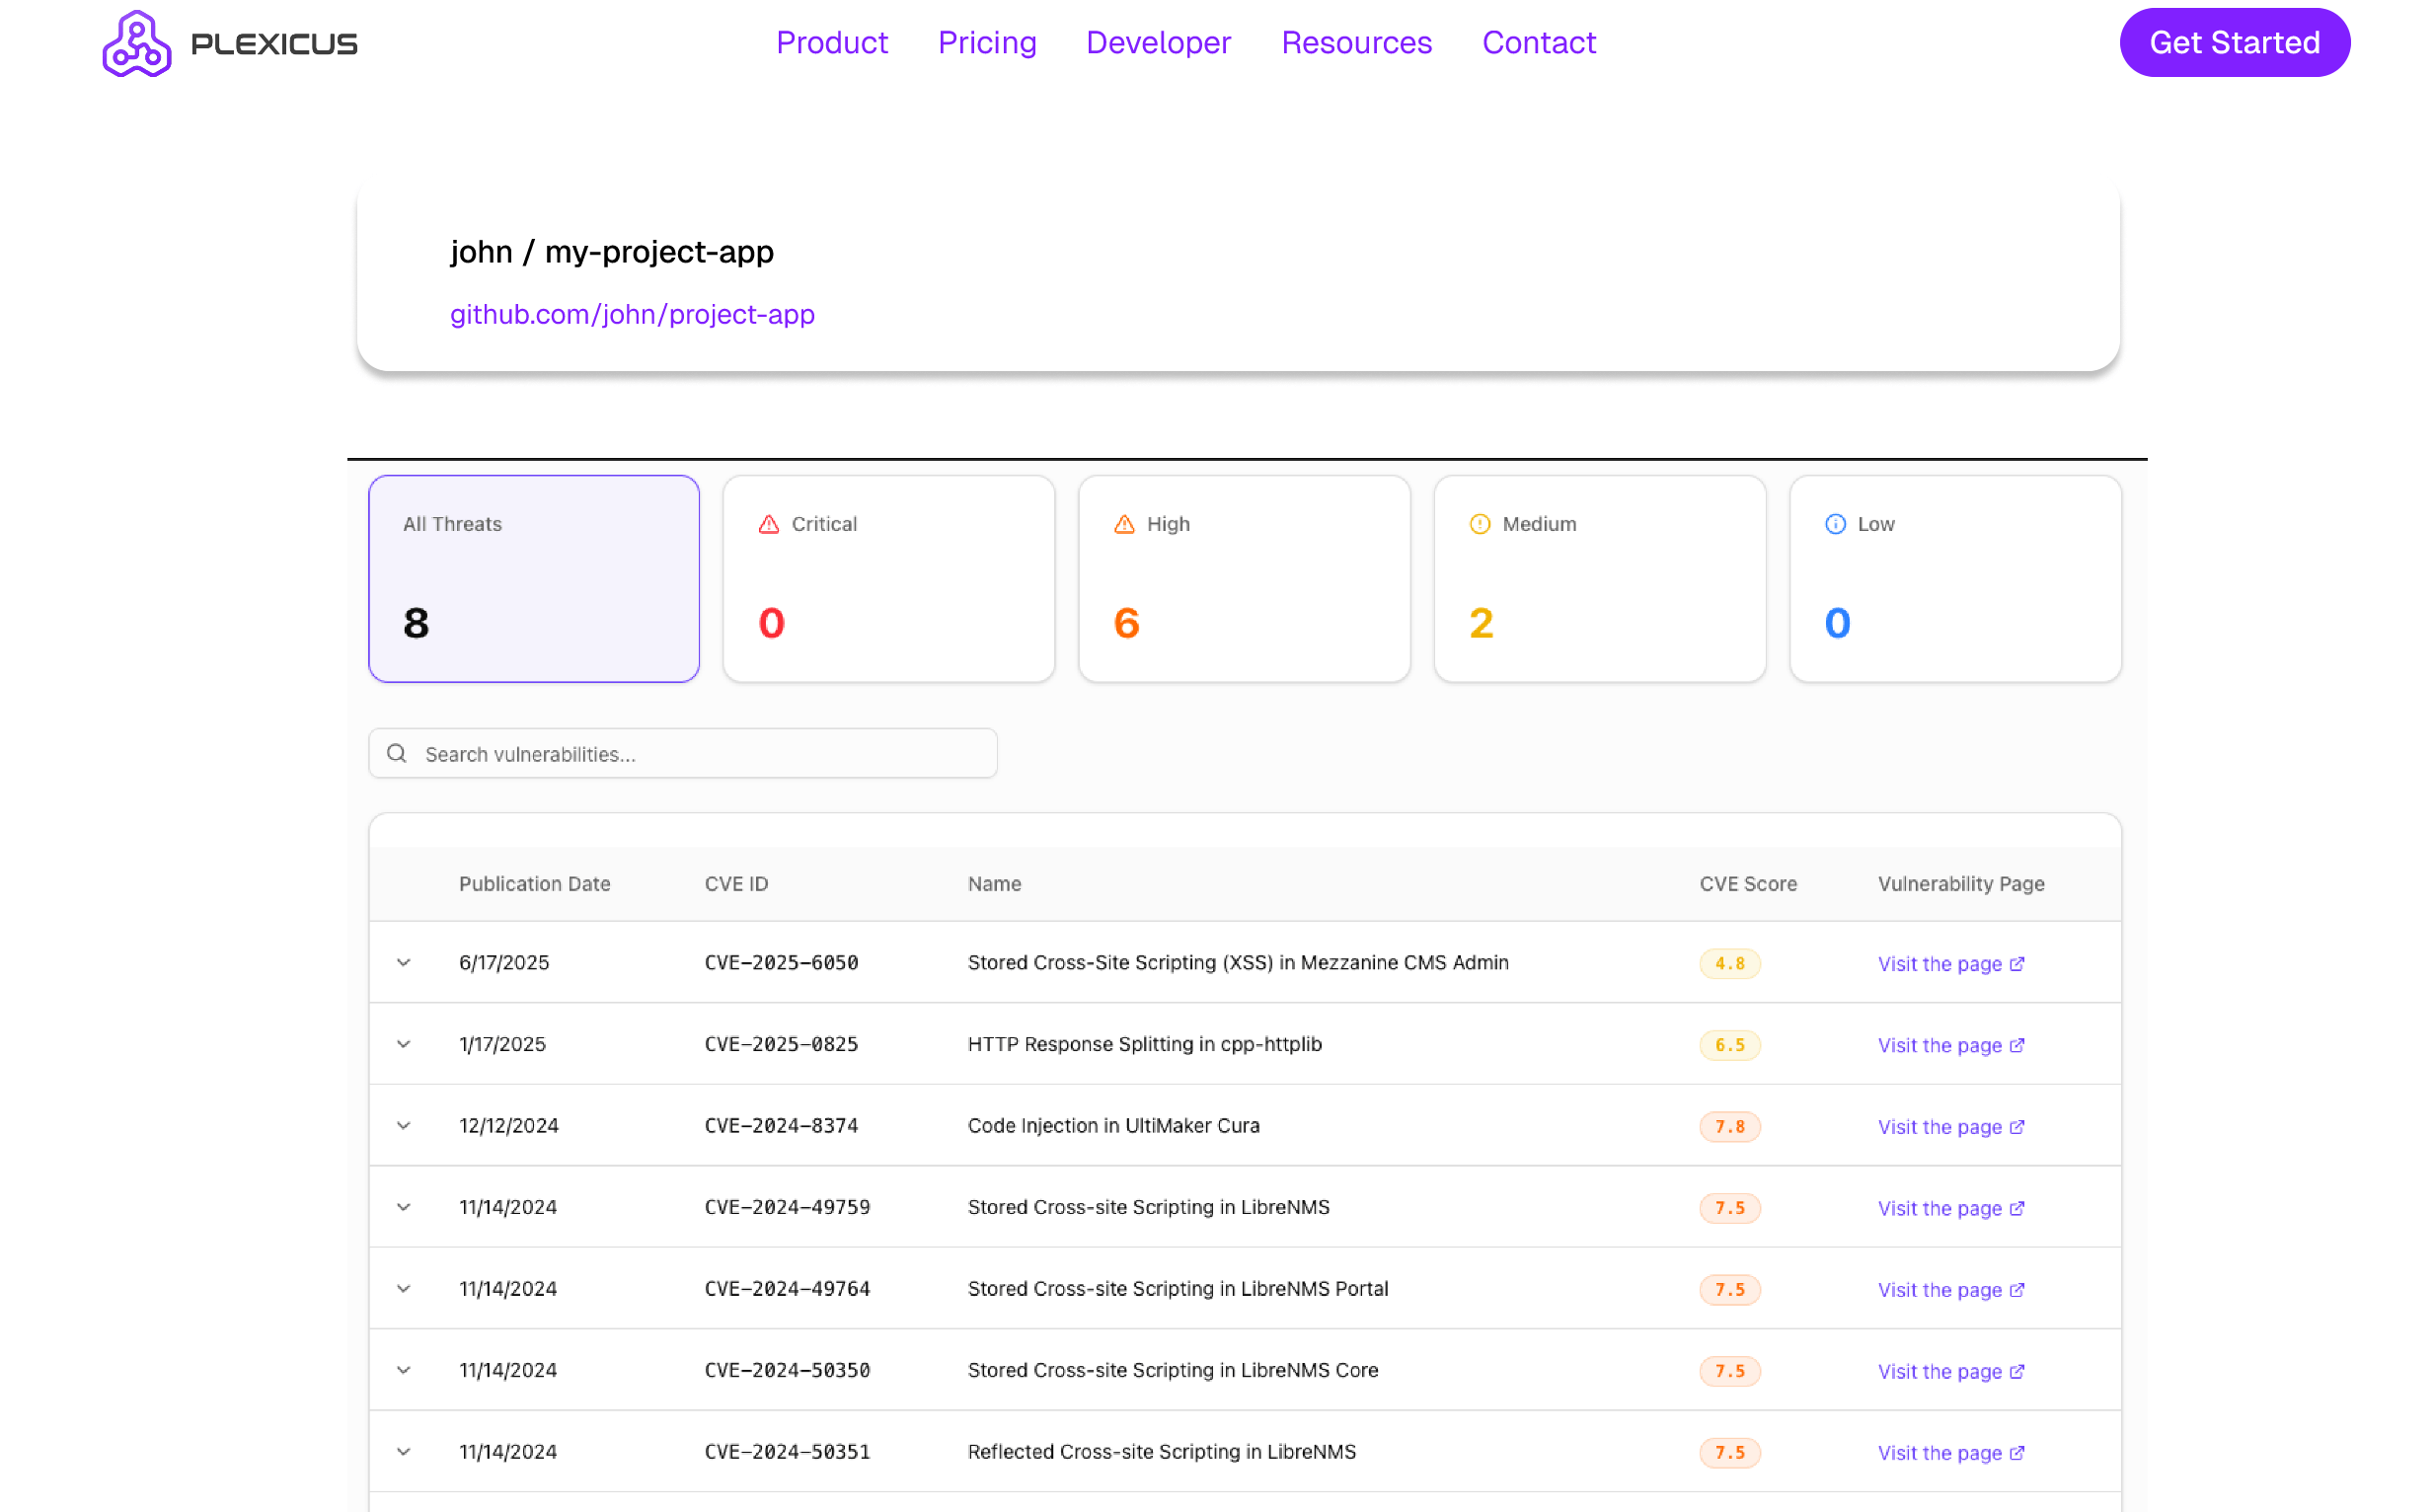
SAST scan result dashboard
Your free report includes
  • List of detected vulnerabilities
  • Severity breakdown (Critical, High, Medium, Low)
  • CVE references and CVSS scoring
PRIVACY FIRST

Your Code Stays Yours

No code storage

Scans run temporarily and are deleted immediately.

No AI training

Your code is never used to train AI models.

Secure SCM integration

Read-only access ensures your repo stays safe.

FAQ

Frequently Asked Questions

Is Free SAST Tool really free?

Yes. It’s free forever — no credit card, no expiration. Advanced features available on the Continuous Program.

Do you keep my code?

No. Scans run temporarily and your code is deleted as soon as the analysis completes.

Do you use my code for AI training?

Never. Your code is yours. We don’t use it for AI

What languages are supported?

We support a wide range of programming languages and frameworks, including Python, Java, JavaScript/TypeScript, C/C++, C#, PHP, Ruby, Go, Swift, Kotlin, Rust, Terraform, Kubernetes, Dockerfiles, CloudFormation, Bash/Shell, SQL, YAML/JSON, Objective-C, and more

Which Git providers are supported?

The free scan connects to GitHub today, with one-click read-only access. GitLab and Bitbucket are coming soon — the full Plexicus platform already supports all three.

FREE SAST TOOL

Ready to validate what matters?

Book a deeper, human-reviewed pentest for the same repository you've scanned — evidence-bound findings, reproducible on demand.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit
Do you have a recent classic pentest you're not happy with?

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)