GitHub Will Block pull_request_target by Default in Public Repositories
A GitHub Actions policy change puts privileged pull request workflows under scrutiny. Here is what maintainers can do before enforcement.
17 articles
A GitHub Actions policy change puts privileged pull request workflows under scrutiny. Here is what maintainers can do before enforcement.
Separate PHP runtime exposure from application findings, verify worker replacement and keep remediation evidence reviewable with Plexicus.
EMBRACE is a useful reminder that an embedded browser does not automatically keep the security boundaries of a standalone browser.
Cloudflare’s open-source coding-agent skill uses coverage-led hunting, independent validation, and structured evidence. Here is what the workflow can—and cannot—establish.
AI can help analysts navigate compiled software, but a decompiler output is not a vulnerability report. See how REA changes analysis, why reverse- engineering agents need protection, and how teams can validate findings.
Three systems asserted a condition and none of them checked whether it still held. A registry reported a package was attested. An evaluation harness reported a model was offline. An assistant reported a package would work.
An editorial guide to security MCP integrations for AI-assisted development: repository findings, scanning, web testing, supply chain analysis, and cloud security.
How specialized attack agents share context, challenge hypotheses, and independently verify attack paths inside the Plexicus Proof-Driven AppSec workflow.
A complete guide to application security in 2026, from secure design and software supply chains to testing, exploit validation, remediation, and Proof-Driven AppSec.
A fruit-fly connectome offers a vivid test of a security principle: a demo is not proof until controls show what the advertised system contributes.
DevDay 2026 connected persistent agents, cloud coding, plugins, events, and shared work. Here is what shipped, what is still coming, and where AppSec boundaries lie.
Opus 5.5 motion-graphics demos reveal an agentic loop: plan, write code, run it, inspect, revise. Claude cybersecurity now depends on verification keeping pace.
MAESTRO is the Cloud Security Alliance's 7-layer framework for agentic AI threat modeling, applied by the OWASP GenAI Security Project. This guide turns each layer into a pentest checklist.
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.
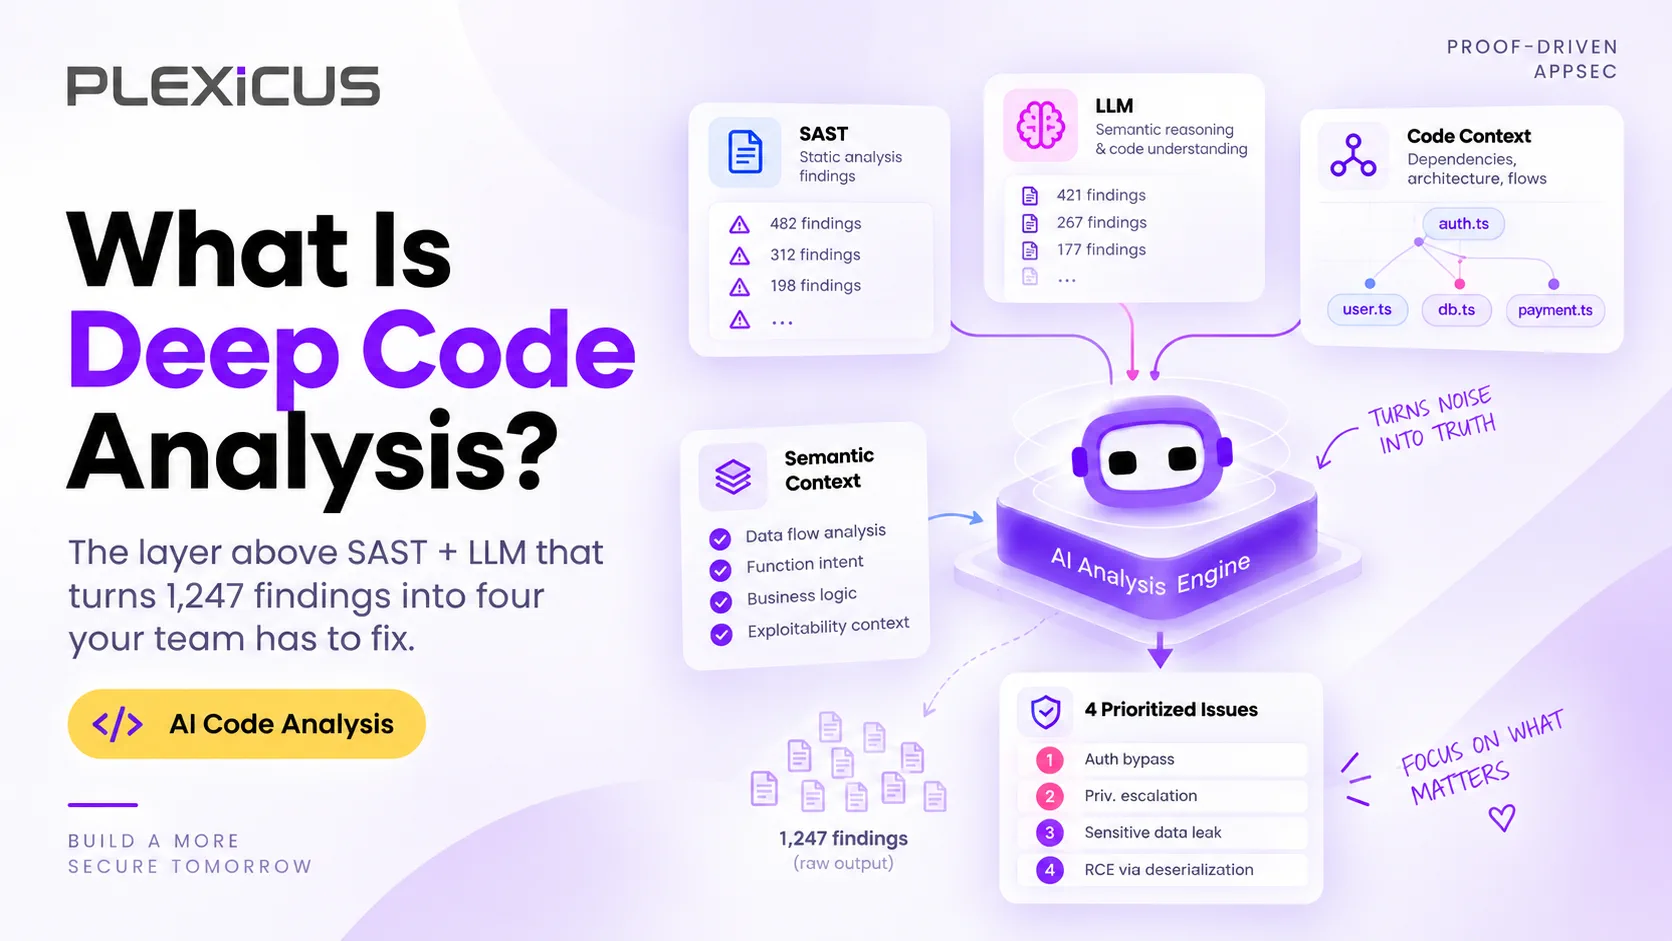
SAST false positives bury real bugs, and an LLM wrapper does not fix that. Deep Code Analysis uses reachability analysis to prove which findings are real, reachable, and worth fixing.
Se stai costruendo o gestendo software oggi, probabilmente stai destreggiando micro-servizi, funzioni serverless, container, pacchetti di terze parti e una valanga di caselle di controllo per la conformità. Ogni parte in movimento genera le proprie scoperte, dashboard e allarmi rossi arrabbiati. Prima o poi, la visibilità del rischio sembra guidare nella nebbia di San Francisco alle 2 del mattino: sai che il pericolo è là fuori, ma non riesci a vederlo chiaramente.
Una nuova collaborazione tra Plexicus e Céfiros mira a migliorare la sicurezza delle applicazioni in 19 paesi in America Latina e Iberia. Questa collaborazione sulla sicurezza informatica porta soluzioni avanzate di Application Security Posture Management (ASPM) alle organizzazioni che cercano di difendersi proattivamente dalle minacce informatiche.

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.