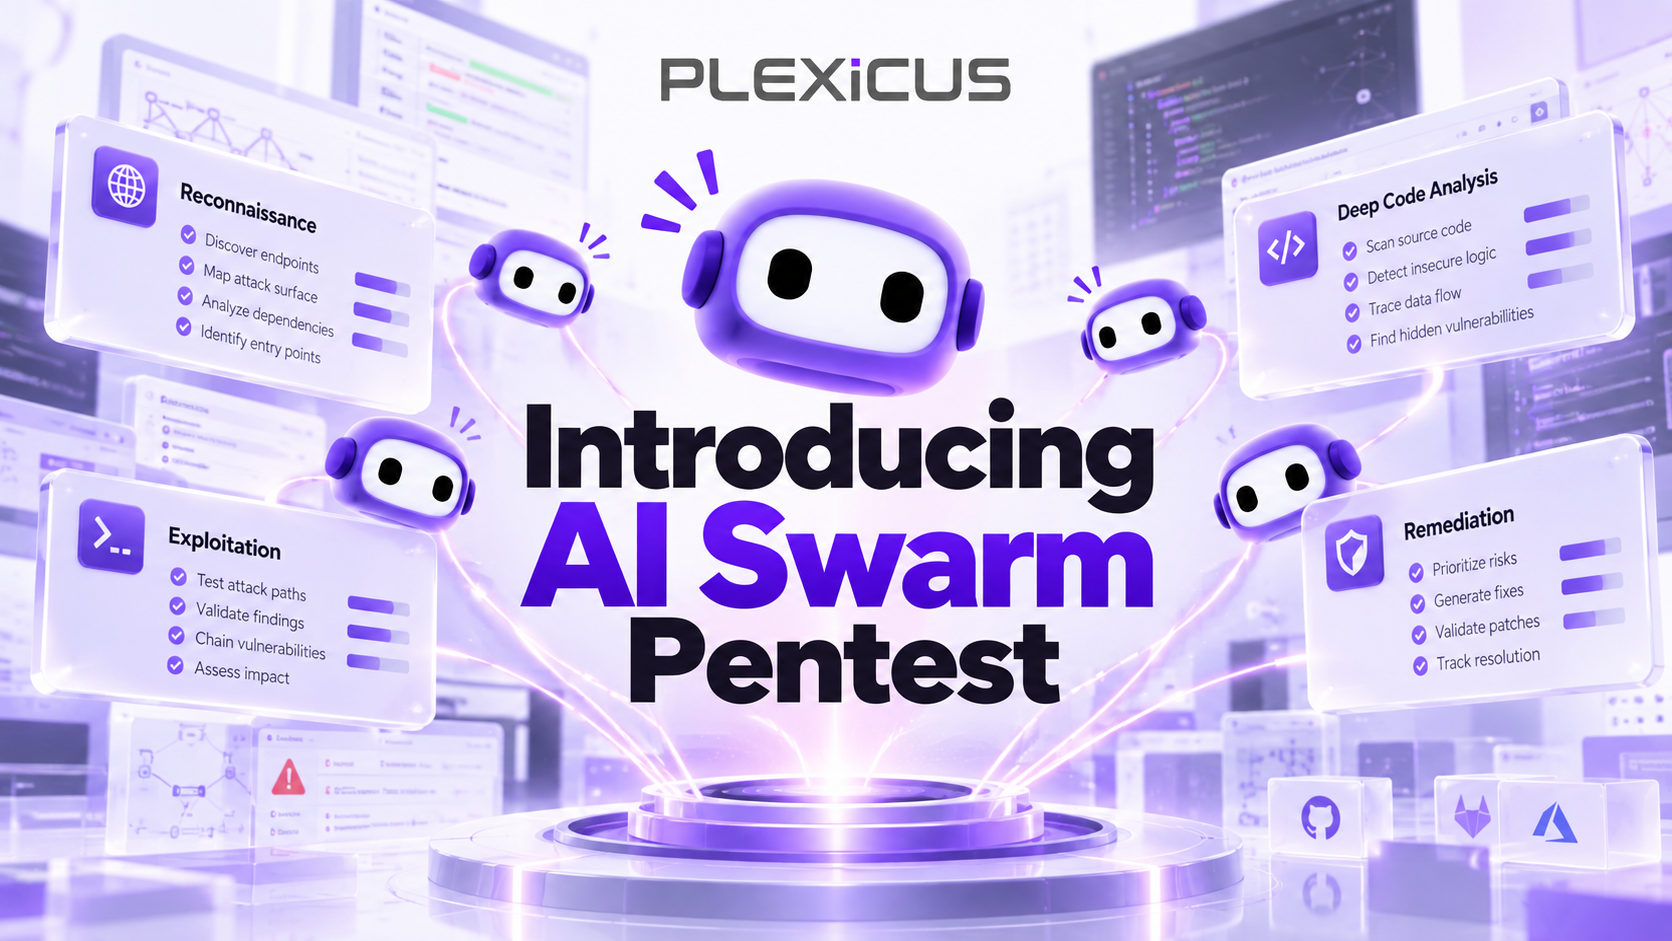
Introducing AI Swarm Pentest: From One AI Pentester to an Orchestrated Team of Attack Agents
How specialized attack agents share context, challenge hypotheses, and independently verify attack paths inside the Plexicus Proof-Driven AppSec workflow.
10 articles
How specialized attack agents share context, challenge hypotheses, and independently verify attack paths inside the Plexicus Proof-Driven AppSec workflow.
A complete guide to application security in 2026, from secure design and software supply chains to testing, exploit validation, remediation, and Proof-Driven AppSec.
A fruit-fly connectome offers a vivid test of a security principle: a demo is not proof until controls show what the advertised system contributes.
DevDay 2026 connected persistent agents, cloud coding, plugins, events, and shared work. Here is what shipped, what is still coming, and where AppSec boundaries lie.
Opus 5.5 motion-graphics demos reveal an agentic loop: plan, write code, run it, inspect, revise. Claude cybersecurity now depends on verification keeping pace.
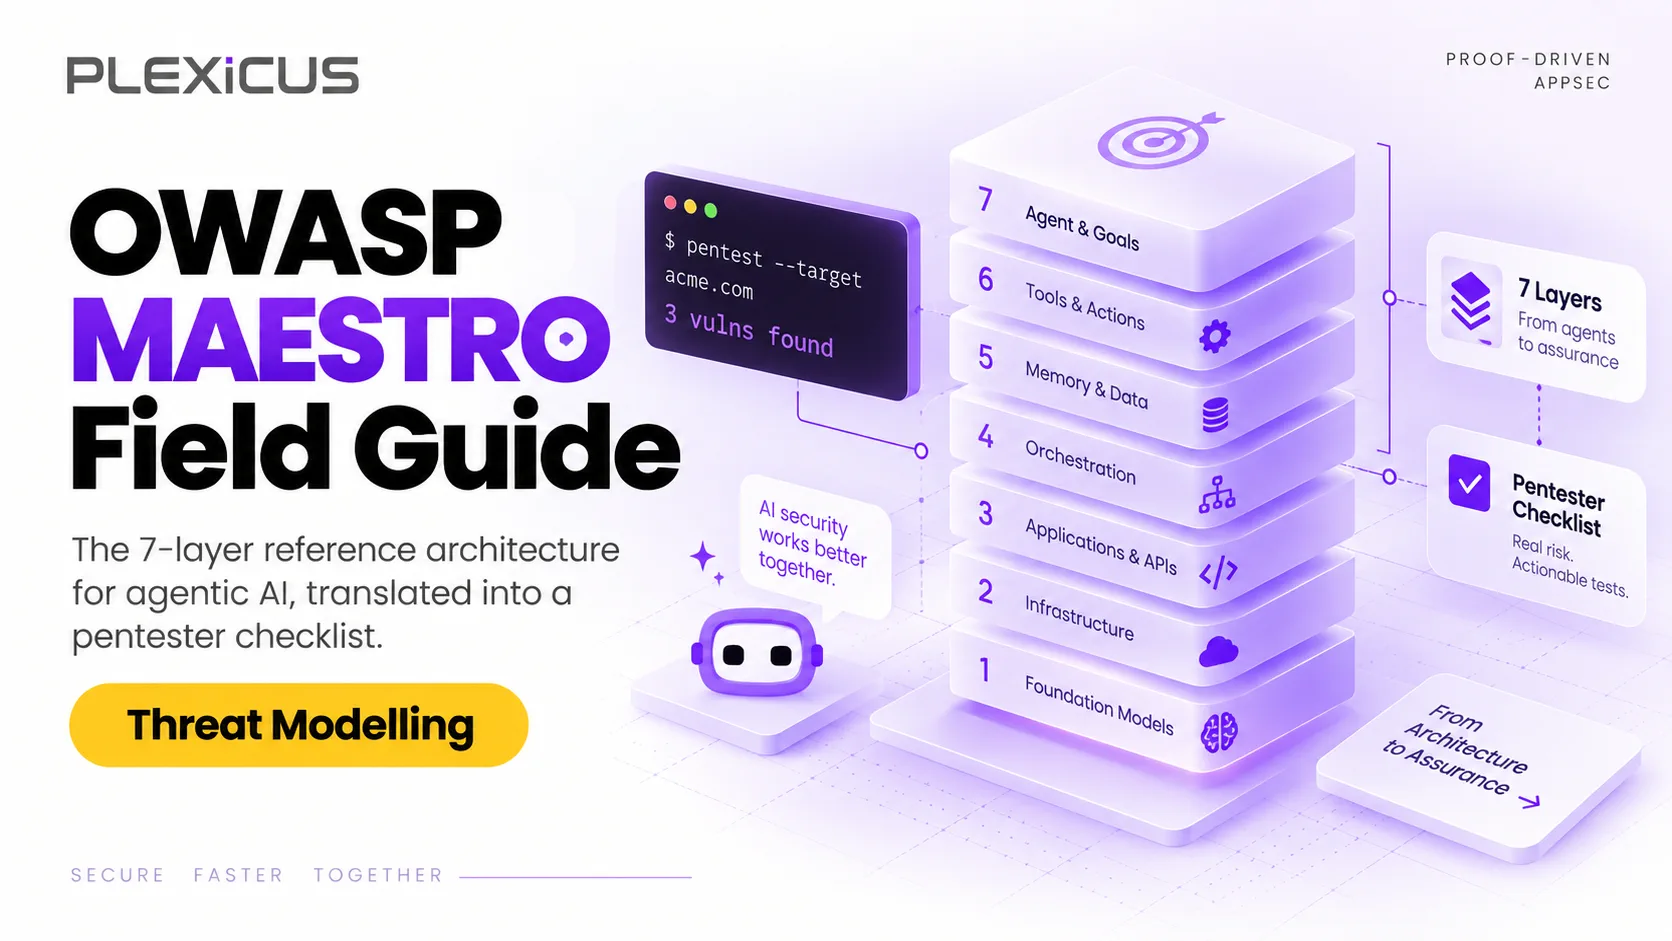
MAESTRO is the Cloud Security Alliance's 7-layer framework for agentic AI threat modeling, applied by the OWASP GenAI Security Project. This guide turns each layer into a pentest checklist.
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.
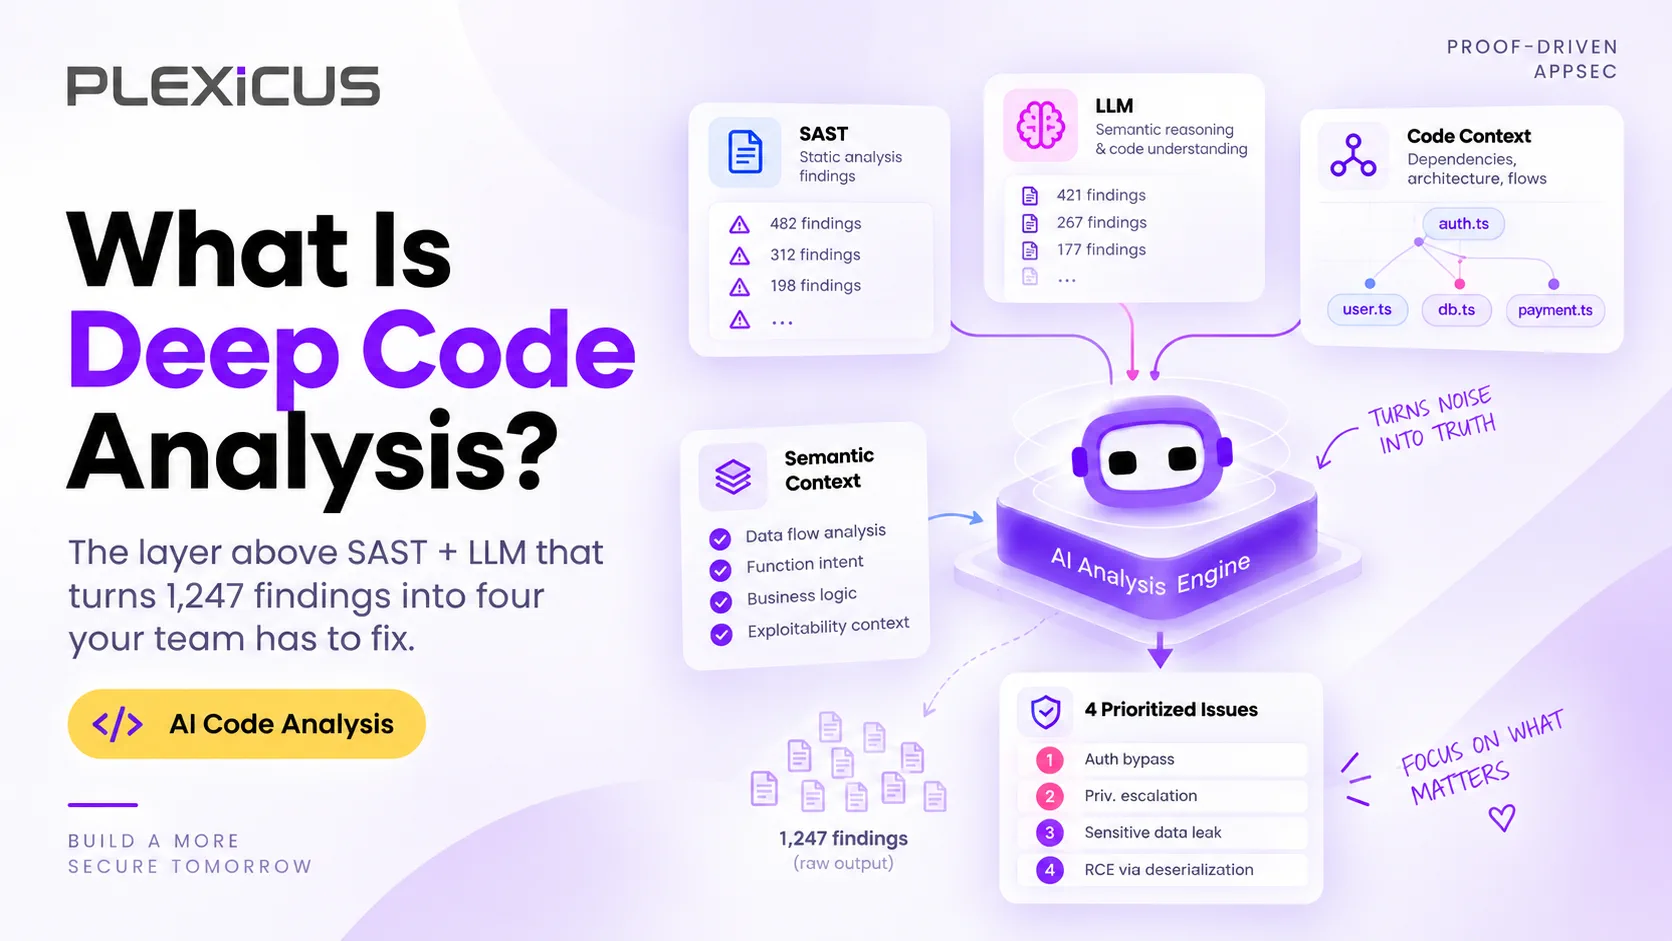
SAST false positives bury real bugs, and an LLM wrapper does not fix that. Deep Code Analysis uses reachability analysis to prove which findings are real, reachable, and worth fixing.
Hvis du bygger eller kjører programvare i dag, sjonglerer du sannsynligvis mikrotjenester, serverløse funksjoner, containere, tredjepartspakker og en lavine av samsvarssjekklister. Hver bevegelig del genererer sine egne funn, dashbord og sinte røde varsler. Før du vet ordet av det, føles risikosynlighet som å kjøre i San Francisco-tåke klokken 2 om natten - du vet at faren er der ute, men du kan ikke helt se den.
Et nytt samarbeid mellom Plexicus og Céfiros er satt til å forbedre applikasjonssikkerhet i 19 land i Latam og Iberia. Dette cybersikkerhetssamarbeidet bringer avanserte Application Security Posture Management (ASPM) løsninger til organisasjoner som ønsker å proaktivt forsvare seg mot cybertrusler.

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.