Tag:

application security

5 articles

AI Automation vs. AI Augmentation for Application Security
Application Security

AI Automation vs. AI Augmentation for Application Security

AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
What Is Deep Code Analysis? (And Why SAST + LLM Isn't Enough)
AI Code Analysis

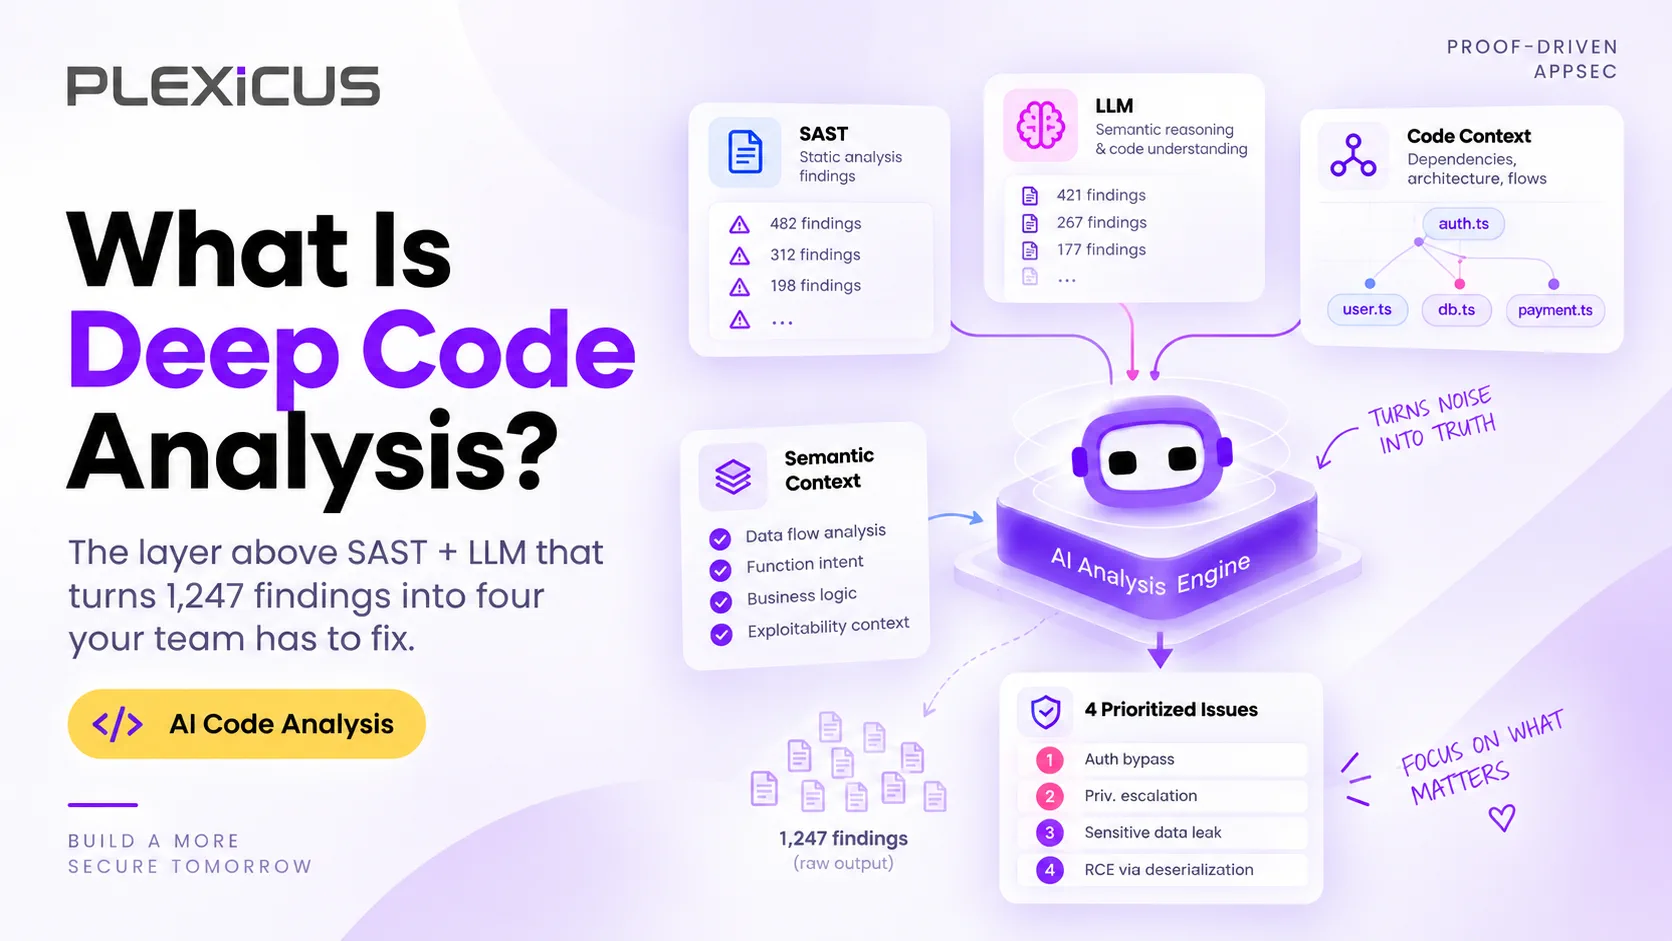
What Is Deep Code Analysis? (And Why SAST + LLM Isn't Enough)

Regex SAST gives you thousands of theory-class findings. LLM-assisted review gives you confident rewrites that may not run. Deep Code Analysis is the third layer: a structural model of your code that proves which findings are real, reachable, and worth fixing.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
应用安全态势管理(ASPM)的终极咨询指南
Application Security

应用安全态势管理(ASPM)的终极咨询指南

如果您今天正在构建或运行软件,您可能正在同时处理微服务、无服务器功能、容器、第三方包以及大量的合规性检查项。每个活动部件都会产生自己的发现、仪表板和愤怒的红色警报。很快,风险可见性就像在凌晨2点的旧金山雾中驾驶——您知道危险就在外面,但您看不太清楚。

José Palanco José Palanco ·
Plexicus和Céfiros加强19个国家的网络安全
Cybersecurity

Plexicus和Céfiros加强19个国家的网络安全

Plexicus和Céfiros之间的新合作将提升拉美和伊比利亚19个国家的应用安全性。此次网络安全合作为寻求主动防御网络威胁的组织带来了先进的应用安全态势管理(ASPM)解决方案。

José Palanco José Palanco ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit
Do you have a recent classic pentest you're not happy with?

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)