
Tag:

SAST

3 articles

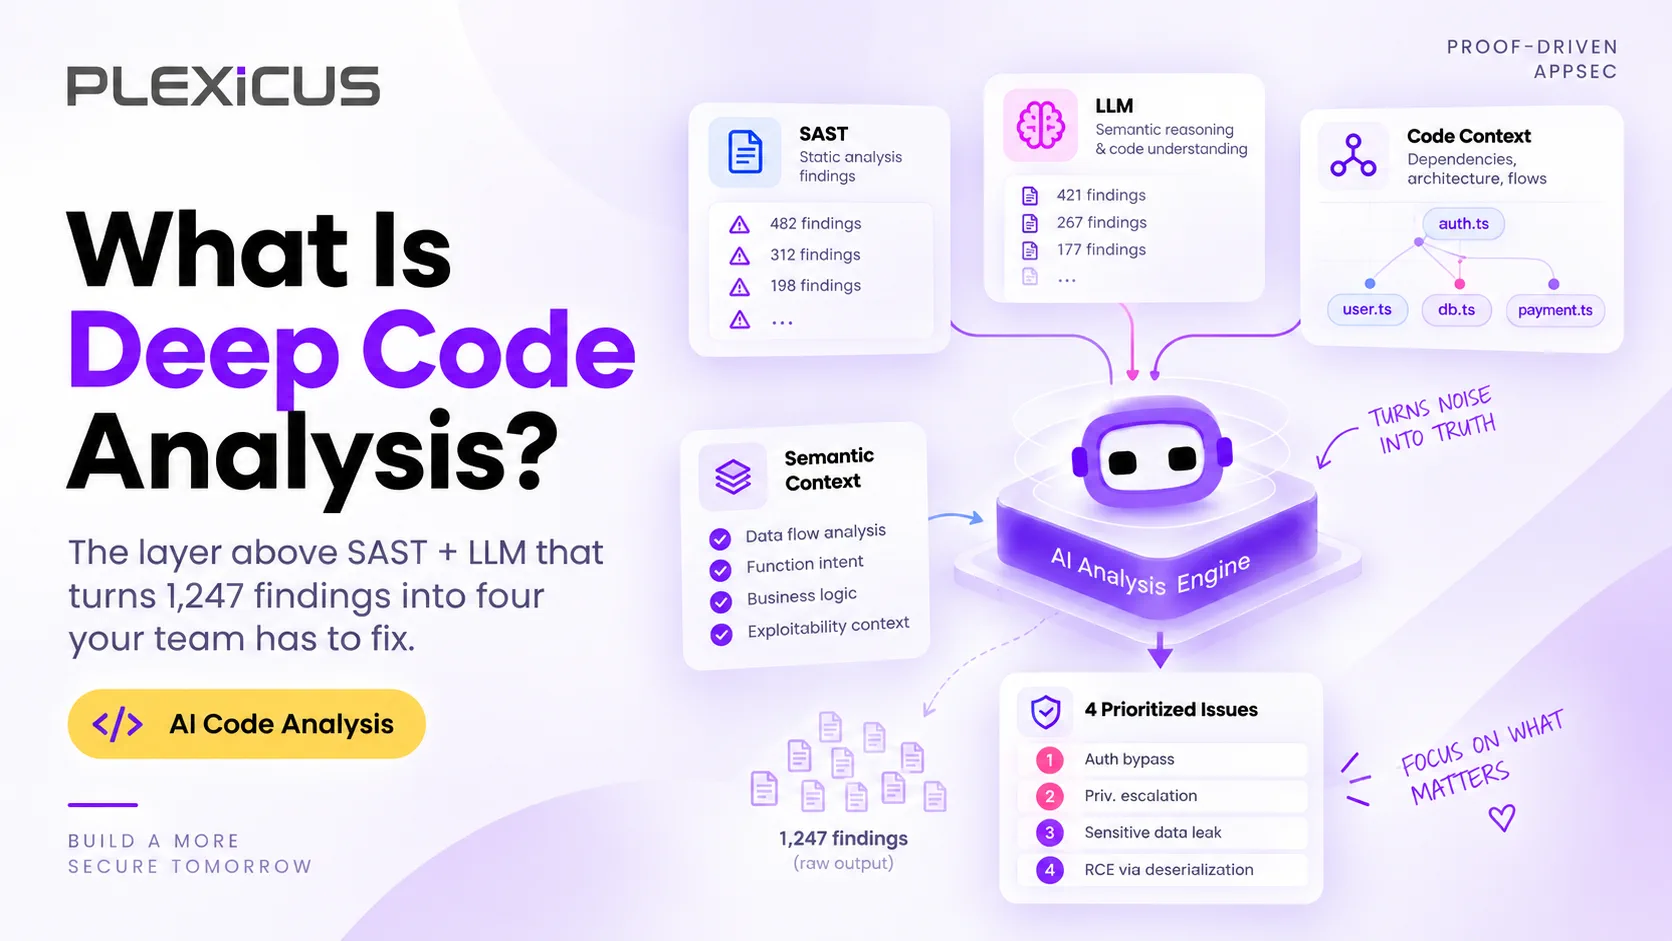
What Is Deep Code Analysis? (And Why SAST + LLM Isn't Enough)
AI Code Analysis

What Is Deep Code Analysis? (And Why SAST + LLM Isn't Enough)

Regex SAST gives you thousands of theory-class findings. LLM-assisted review gives you confident rewrites that may not run. Deep Code Analysis is the third layer: a structural model of your code that proves which findings are real, reachable, and worth fixing.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
如何大规模自动化SQL注入(SQLi)修复
Application Security

如何大规模自动化SQL注入(SQLi)修复

在本指南中,您将学习如何超越手动修补,构建一个使用AI驱动自动化来自动检测、优先处理和修复SQLi漏洞的工作流程。

Khul Anwar Khul Anwar ·
SAST 与 DAST:有什么区别及为何应同时使用
Cybersecurity

SAST 与 DAST:有什么区别及为何应同时使用

SAST 和 DAST 是用于保护应用程序免受攻击的安全测试方法。为了了解每种方法如何帮助应用程序安全性,我们来看看它们的区别以及它们在工作流程中的位置

José Palanco José Palanco ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit
Do you have a recent classic pentest you're not happy with?

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)




