José Palanco
Written by

José Palanco

José Ramón Palanco is the CEO/CTO of Plexicus, a pioneering company in ASPM (Application Security Posture Management) launched in 2024, offering AI-powered remediation capabilities. Previously, he founded Dinoflux in 2014, a Threat Intelligence startup that was acquired by Telefonica, and has been working with 11paths since 2018. His experience includes roles at Ericsson`s R&D department and Optenet (Allot). He holds a Telecommunications Engineering degree from the University of Alcala de Henares and a Master`s in IT Governance from the University of Deusto. As a recognized cybersecurity expert, he has been a speaker at various prestigious conferences including OWASP, ROOTEDCON, ROOTCON, MALCON, and FAQin. His contributions to the cybersecurity field include multiple CVE publications and the development of various open source tools such as nmap-scada, ProtocolDetector, escan, pma, EKanalyzer, SCADA IDS, and more.

Jev Doesn't Chat. It Decides. Why That Matters for Cybersecurity.
Application Security

Jev Doesn't Chat. It Decides. Why That Matters for Cybersecurity.

Jev is designed to return typed decisions instead of prose. That distinction could change where semantic judgment fits in security workflows, provided teams retain policy, fallbacks, verification, and human review.

José Palanco José Palanco ·
Top 15 AI Pentest Tools for 2026: Autonomous Agents Ranked & Compared
Review

Top 15 AI Pentest Tools for 2026: Autonomous Agents Ranked & Compared

The 2026 AI pentest market splits into three lanes: autonomous agents that exploit live systems, BAS platforms that emulate adversary techniques, and PTaaS vendors that wrap AI around human testers. We ranked 15 of them on signed-scope evidence, replay verification, and pricing transparency so you can pick the right one for your next pentest run.

José Palanco José Palanco ·
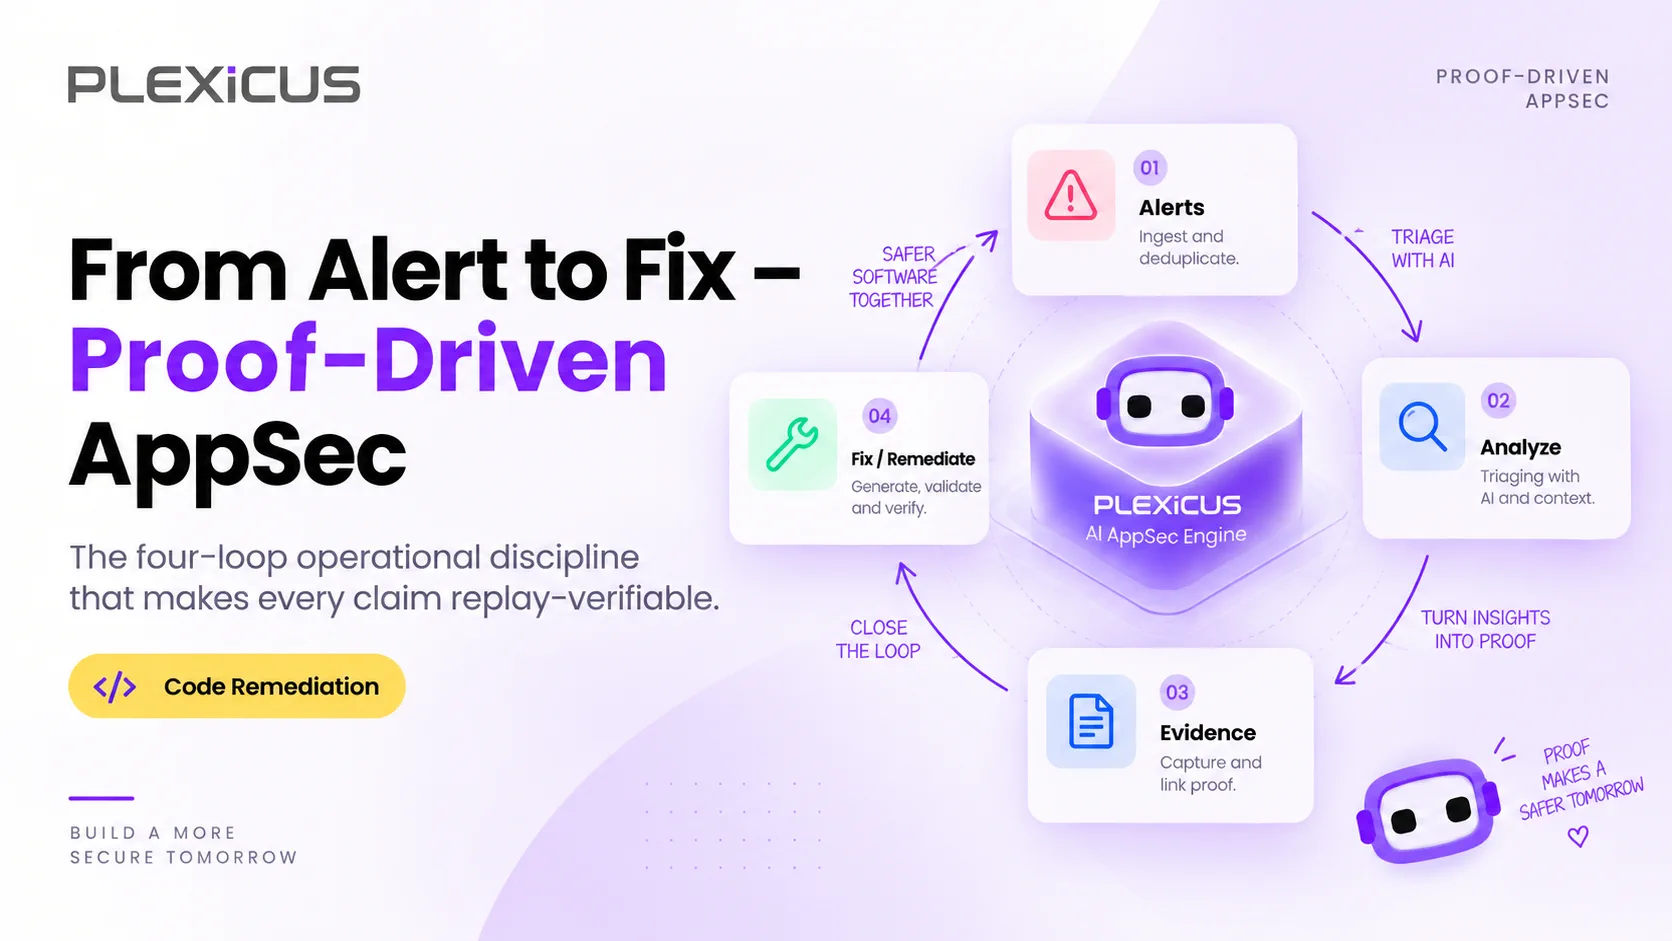
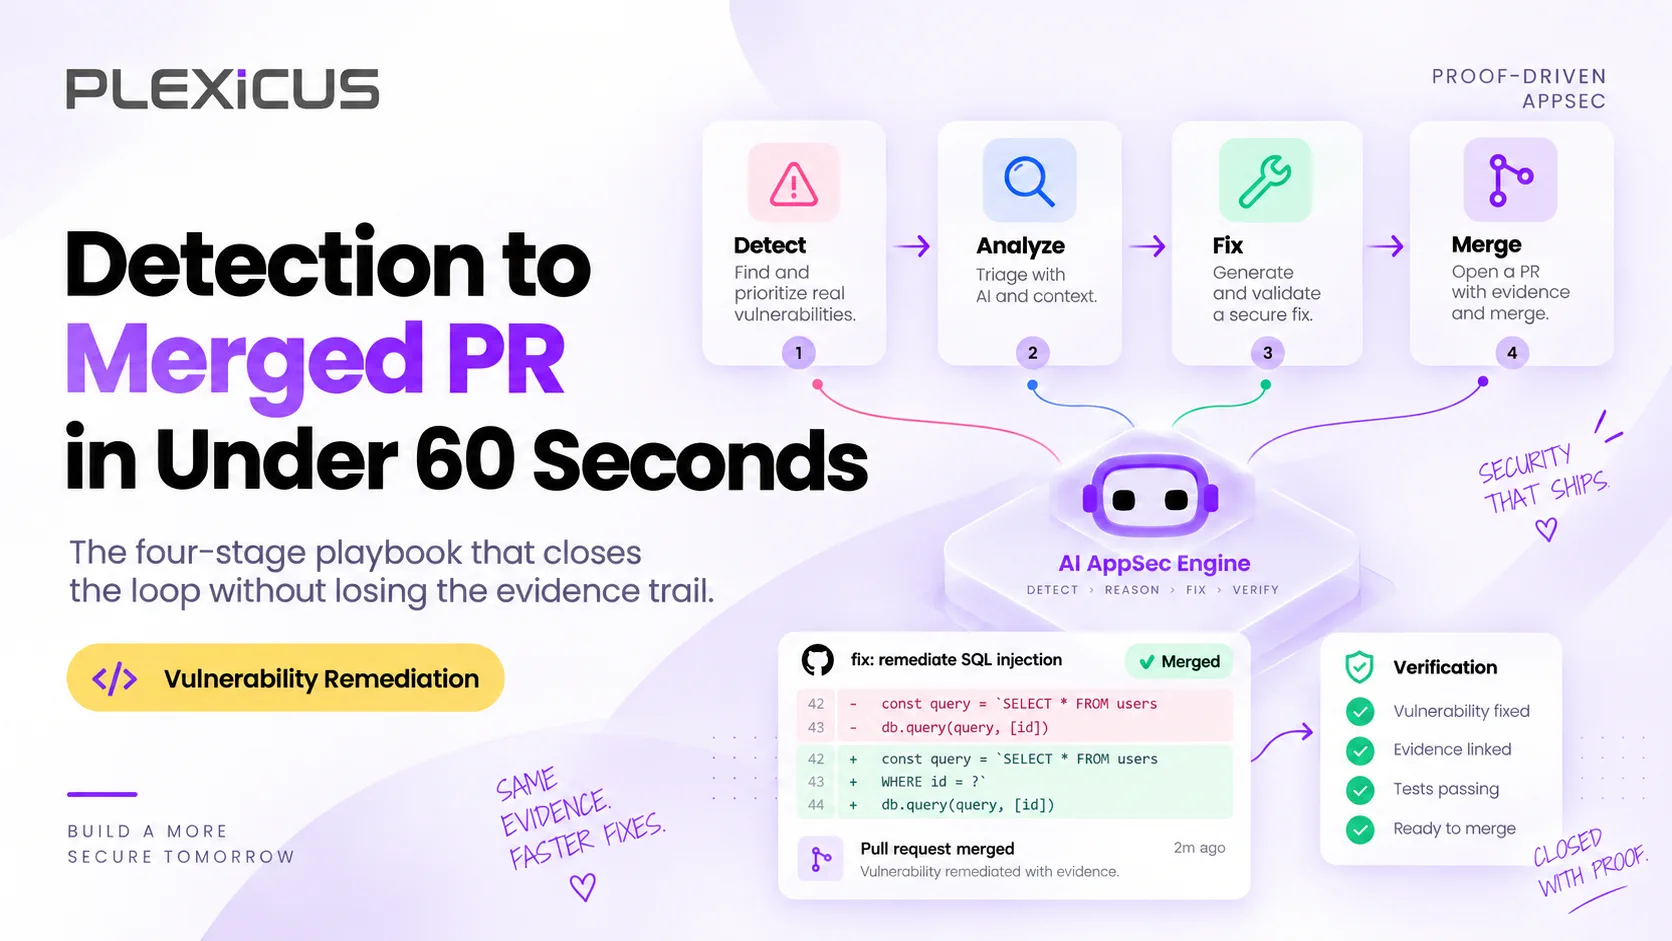
From Alert to Fix: Closing the Loop with Proof-Driven AppSec
Code Remediation

From Alert to Fix: Closing the Loop with Proof-Driven AppSec

Most security programs are a series of disconnected loops — alert, triage, fix, audit, fix again, audit again. Proof-Driven AppSec closes the loop once and makes every step provable. This is the canonical definition, the four-loop structure, and what it looks like in production.

José Palanco José Palanco ·
AI Automation vs. AI Augmentation for Application Security
Application Security

AI Automation vs. AI Augmentation for Application Security

AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.

José Palanco José Palanco ·
ארסנל ה-DevSecOps: מאפס לגיבור
Learn

ארסנל ה-DevSecOps: מאפס לגיבור

הרצת `trivy image` אינה DevSecOps8 אלא יצירת רעש. הנדסת אבטחה אמיתית עוסקת ביחס אות לרעש. מדריך זה מספק תצורות ברמת ייצור עבור 17 כלים סטנדרטיים בתעשייה כדי לעצור פגיעויות מבלי לעצור את העסק, מאורגן בשלושה שלבים: לפני התחייבות, שומרי סף CI וסריקות בזמן ריצה.

José Palanco José Palanco ·
חתוך את הרעש: הפוך את כלי האבטחה שלך לעובדים עבורך
Learn

חתוך את הרעש: הפוך את כלי האבטחה שלך לעובדים עבורך

התקנת כלי אבטחה היא החלק הקל. החלק הקשה מתחיל ב'יום השני', כאשר הכלי מדווח על 5,000 פגיעויות חדשות. מדריך זה מתמקד בניהול פגיעויות: כיצד לסנן התראות כפולות, לנהל חיוביות שגויות ולעקוב אחר המדדים שבאמת מודדים הצלחה. למד כיצד לעבור מ'מציאת באגים' ל'תיקון סיכונים' מבלי להעמיס על הצוות שלך.

José Palanco José Palanco ·
SAST מול DAST: מה ההבדל ולמה כדאי להשתמש בשניהם
Cybersecurity

SAST מול DAST: מה ההבדל ולמה כדאי להשתמש בשניהם

SAST ו-DAST הם שיטות בדיקות אבטחה המשמשות להגנה על יישומים מפני התקפות. כדי לראות כיצד כל אחת מהן מסייעת באבטחת יישומים, נבחן את ההבדלים ביניהן ואת מקומן בתהליך העבודה שלך.

José Palanco José Palanco ·
הכלים הטובים ביותר ל-SCA ב-2025: סריקת תלות, אבטחת שרשרת אספקת התוכנה שלך
Review

הכלים הטובים ביותר ל-SCA ב-2025: סריקת תלות, אבטחת שרשרת אספקת התוכנה שלך

יישומים מודרניים תלויים רבות בספריות צד שלישי וקוד פתוח. זה מאיץ את הפיתוח, אך גם מגדיל את הסיכון להתקפות. כל תלות יכולה להכניס בעיות כמו פגמי אבטחה לא מתוקנים, רישיונות מסוכנים או חבילות מיושנות. כלי ניתוח הרכב תוכנה (SCA) עוזרים להתמודד עם בעיות אלו.

José Palanco José Palanco ·
אבטחת יישומים ברשת: שיטות עבודה מומלצות, בדיקות והערכה לשנת 2026
Cybersecurity

אבטחת יישומים ברשת: שיטות עבודה מומלצות, בדיקות והערכה לשנת 2026

אבטחת יישומים ברשת חיונית להגנה על האפליקציות שלך מפני התקפות סייבר שמטרתן נתונים רגישים ושיבוש פעולות. מדריך זה מכסה את חשיבות אבטחת יישומים ברשת, פגיעויות נפוצות, שיטות עבודה מומלצות ושיטות בדיקה, ועוזר לך להבטיח את האפליקציה שלך, להבטיח תאימות ולשמור על אמון המשתמשים

José Palanco José Palanco ·
15 מגמות DevSecOps לאבטחת העסק שלך
Cybersecurity

15 מגמות DevSecOps לאבטחת העסק שלך

פרצת אבטחה סיוטית הפכה למציאות עבור חברות רבות באירופה. למד על 15 מגמות DevSecOps משנות צורה שאתה חייב להכיר כדי להישאר מחוץ לרשימת הפריצות.

José Palanco José Palanco ·
המדריך הייעוצי האולטימטיבי לניהול מצב אבטחת יישומים (ASPM)
Application Security

המדריך הייעוצי האולטימטיבי לניהול מצב אבטחת יישומים (ASPM)

אם אתה בונה או מפעיל תוכנה כיום, אתה כנראה מתמודד עם מיקרו-שירותים, פונקציות ללא שרת, מכולות, חבילות צד שלישי ומבול של תיבות סימון לציות. כל חלק נע יוצר ממצאים משלו, לוחות מחוונים והתראות אדומות זועמות. במהרה, נראות הסיכון מרגישה כמו נהיגה בערפל של סן פרנסיסקו בשעה 2 בלילה - אתה יודע שהסכנה שם, אבל אתה לא ממש רואה אותה.

José Palanco José Palanco ·
פליקסיקוס מקבלת השקעה של 150,000 דולר ממיקרוסופט
Investment

פליקסיקוס מקבלת השקעה של 150,000 דולר ממיקרוסופט

פליקסיקוס קיבלה השקעה של 150,000 דולר ממיקרוסופט להרחבת תשתית הענן שלה. המימון ישפר את ביצועי המערכת, יכולת ההתרחבות והאמינות, ויאפשר לפליקסיקוס לתמוך ביותר עסקים עם פתרונות ארגוניים מבוססי AI.

José Palanco José Palanco ·
פליקסיקוס וספירוס מחזקים את אבטחת הסייבר ב-19 מדינות
Cybersecurity

פליקסיקוס וספירוס מחזקים את אבטחת הסייבר ב-19 מדינות

שיתוף פעולה חדש בין פליקסיקוס לספירוס צפוי לשפר את אבטחת היישומים ב-19 מדינות בלטם ואיבריה. שיתוף פעולה זה בתחום אבטחת הסייבר מביא פתרונות מתקדמים לניהול מצב אבטחת יישומים (ASPM) לארגונים המבקשים להגן באופן יזום מפני איומי סייבר.

José Palanco José Palanco ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

Teams with fewer than 50 developers: start a 14-day Trial instead of booking a demo. Start a 14-day Trial →

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)