Dependabot Can Update AI Agent Skills. Who Reviews What Changed?
Dependabot can propose version updates for agent dependencies. The change puts skills and instructions into an existing review workflow.

Beyond ASPM
Proof-Driven AppSec for teams building with AI
Plexicus uses AI Swarm Pentest to explore authorized application paths, validate what is exploitable, and give teams evidence they can use to prioritize remediation.
Explore AI Swarm PentestOn November 3, GitHub announced Dependabot version updates for Agent Package Manager. This brings a familiar pull request workflow to declared agent skills, prompts and instructions. It also raises a useful question: who verifies what an agent will do after an update is merged?
What GitHub added
Agent Package Manager (APM) declares agent dependencies in apm.yml. For supported Git dependencies in that manifest, Dependabot can open pull requests proposing newer versions. When apm.lock.yaml exists, Dependabot regenerates it as part of the update. GitHub says the integration is available on GitHub.com for all plans and planned for GitHub Enterprise Server 3.24.
This is support for version updates, not security updates. An update pull request is not a vulnerability alert or proof that a dependency is safe. GitHub documents which APM dependencies and update behaviours are supported.
Why an instruction change deserves review
A package can provide an agent with instructions or skills that shape its work. A version change can therefore change the context an agent receives, even when the application source code is unchanged. That does not mean every update is malicious; it means teams should review the changed material and its source, not approve it solely because a bot opened the pull request.
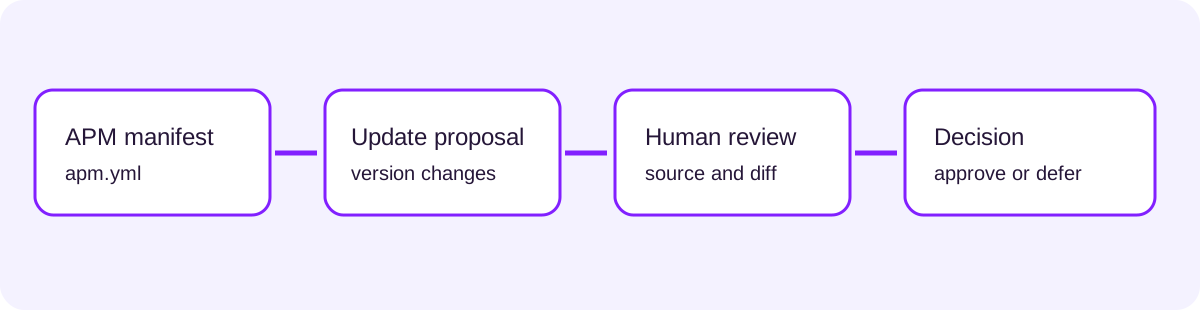
The APM documentation describes its manifest and lockfile. The following is a practical review process, not a claim that Dependabot or Plexicus automatically performs every step:
- Assign an owner for
apm.ymland decide which sources and maintainers are acceptable. - Inspect the proposed dependency and lockfile diff. Check the upstream revision and read changed instructions, scripts and package metadata.
- Evaluate whether the new material requests tools, permissions, network access or secret access beyond its intended job. Test in an appropriately isolated environment when relevant.
- Record the decision and keep rollback information. A scheduled version update does not replace vulnerability monitoring or incident response.
Keep the evidence with the decision
APM dependency review belongs alongside, not inside, the security assessment of the application itself. Plexicus AI Swarm Pentest describes evidence-backed testing of authorized applications and APIs; Plexicus remediation supports reviewable fixes for validated application findings. Neither link establishes that an application scan validates every agent package or Dependabot proposal.
Treat agent context as a reviewable dependency and give the update a named owner. Explore Plexicus remediation for workflows around validated application fixes.
Thumbnail: original Agent Package Manager documentation, Microsoft, MIT License: https://github.com/microsoft/apm/blob/main/LICENSE (license copy). The documentation image illustrates APM; it does not show a Dependabot update or imply endorsement.




