AFTER THE EVIDENCE

Detecting is not Fixing.

Once a finding is verified, Plexicus prepares the remediation context and a suggested change for your team. Your team keeps merge control — Plexicus never pushes to production.

THE PIPELINE

From a validated finding to a reviewer-ready change.

Each step keeps the original evidence attached so engineers and reviewers see the same context.

01

Validated finding

Only findings with clear supporting evidence move into the remediation workflow.

02

Context preserved

Scope, impact, and the relevant source location travel with the proposal.

03

Plexicus drafts

A proposed diff, tests, and an explanation are prepared for engineering review.

04

Human approval

The change returns to your existing repository workflow for review and merge.

LIVE PRODUCT VIEW

See the remediation workflow in context.

Live product views of the Plexicus Remediation workflow.
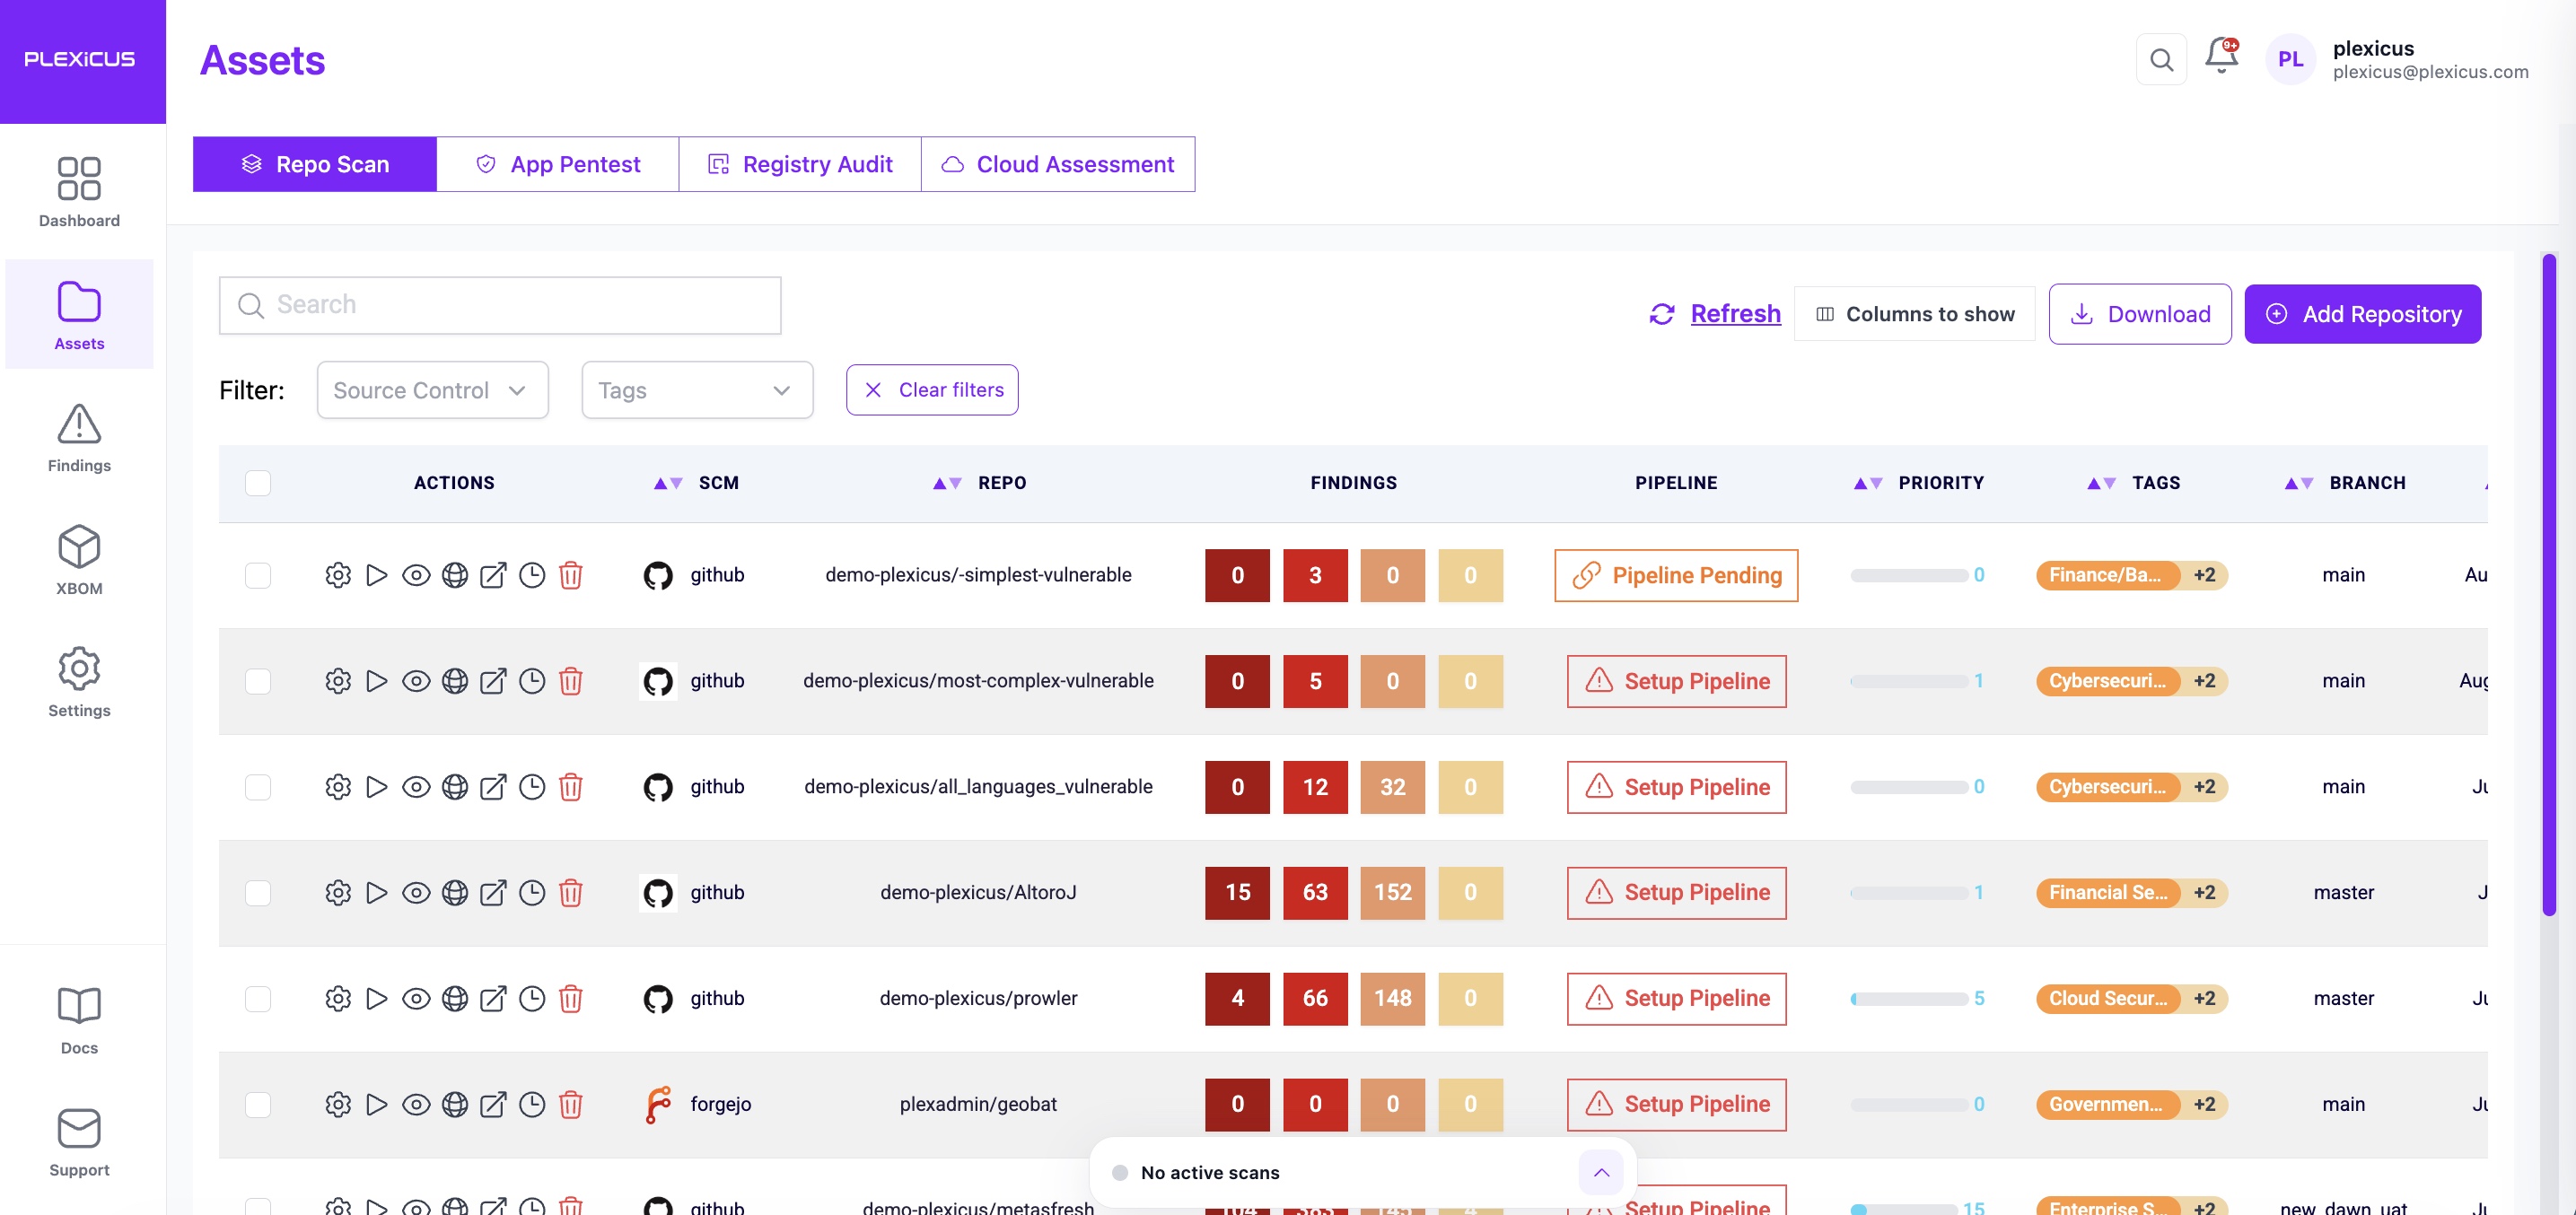
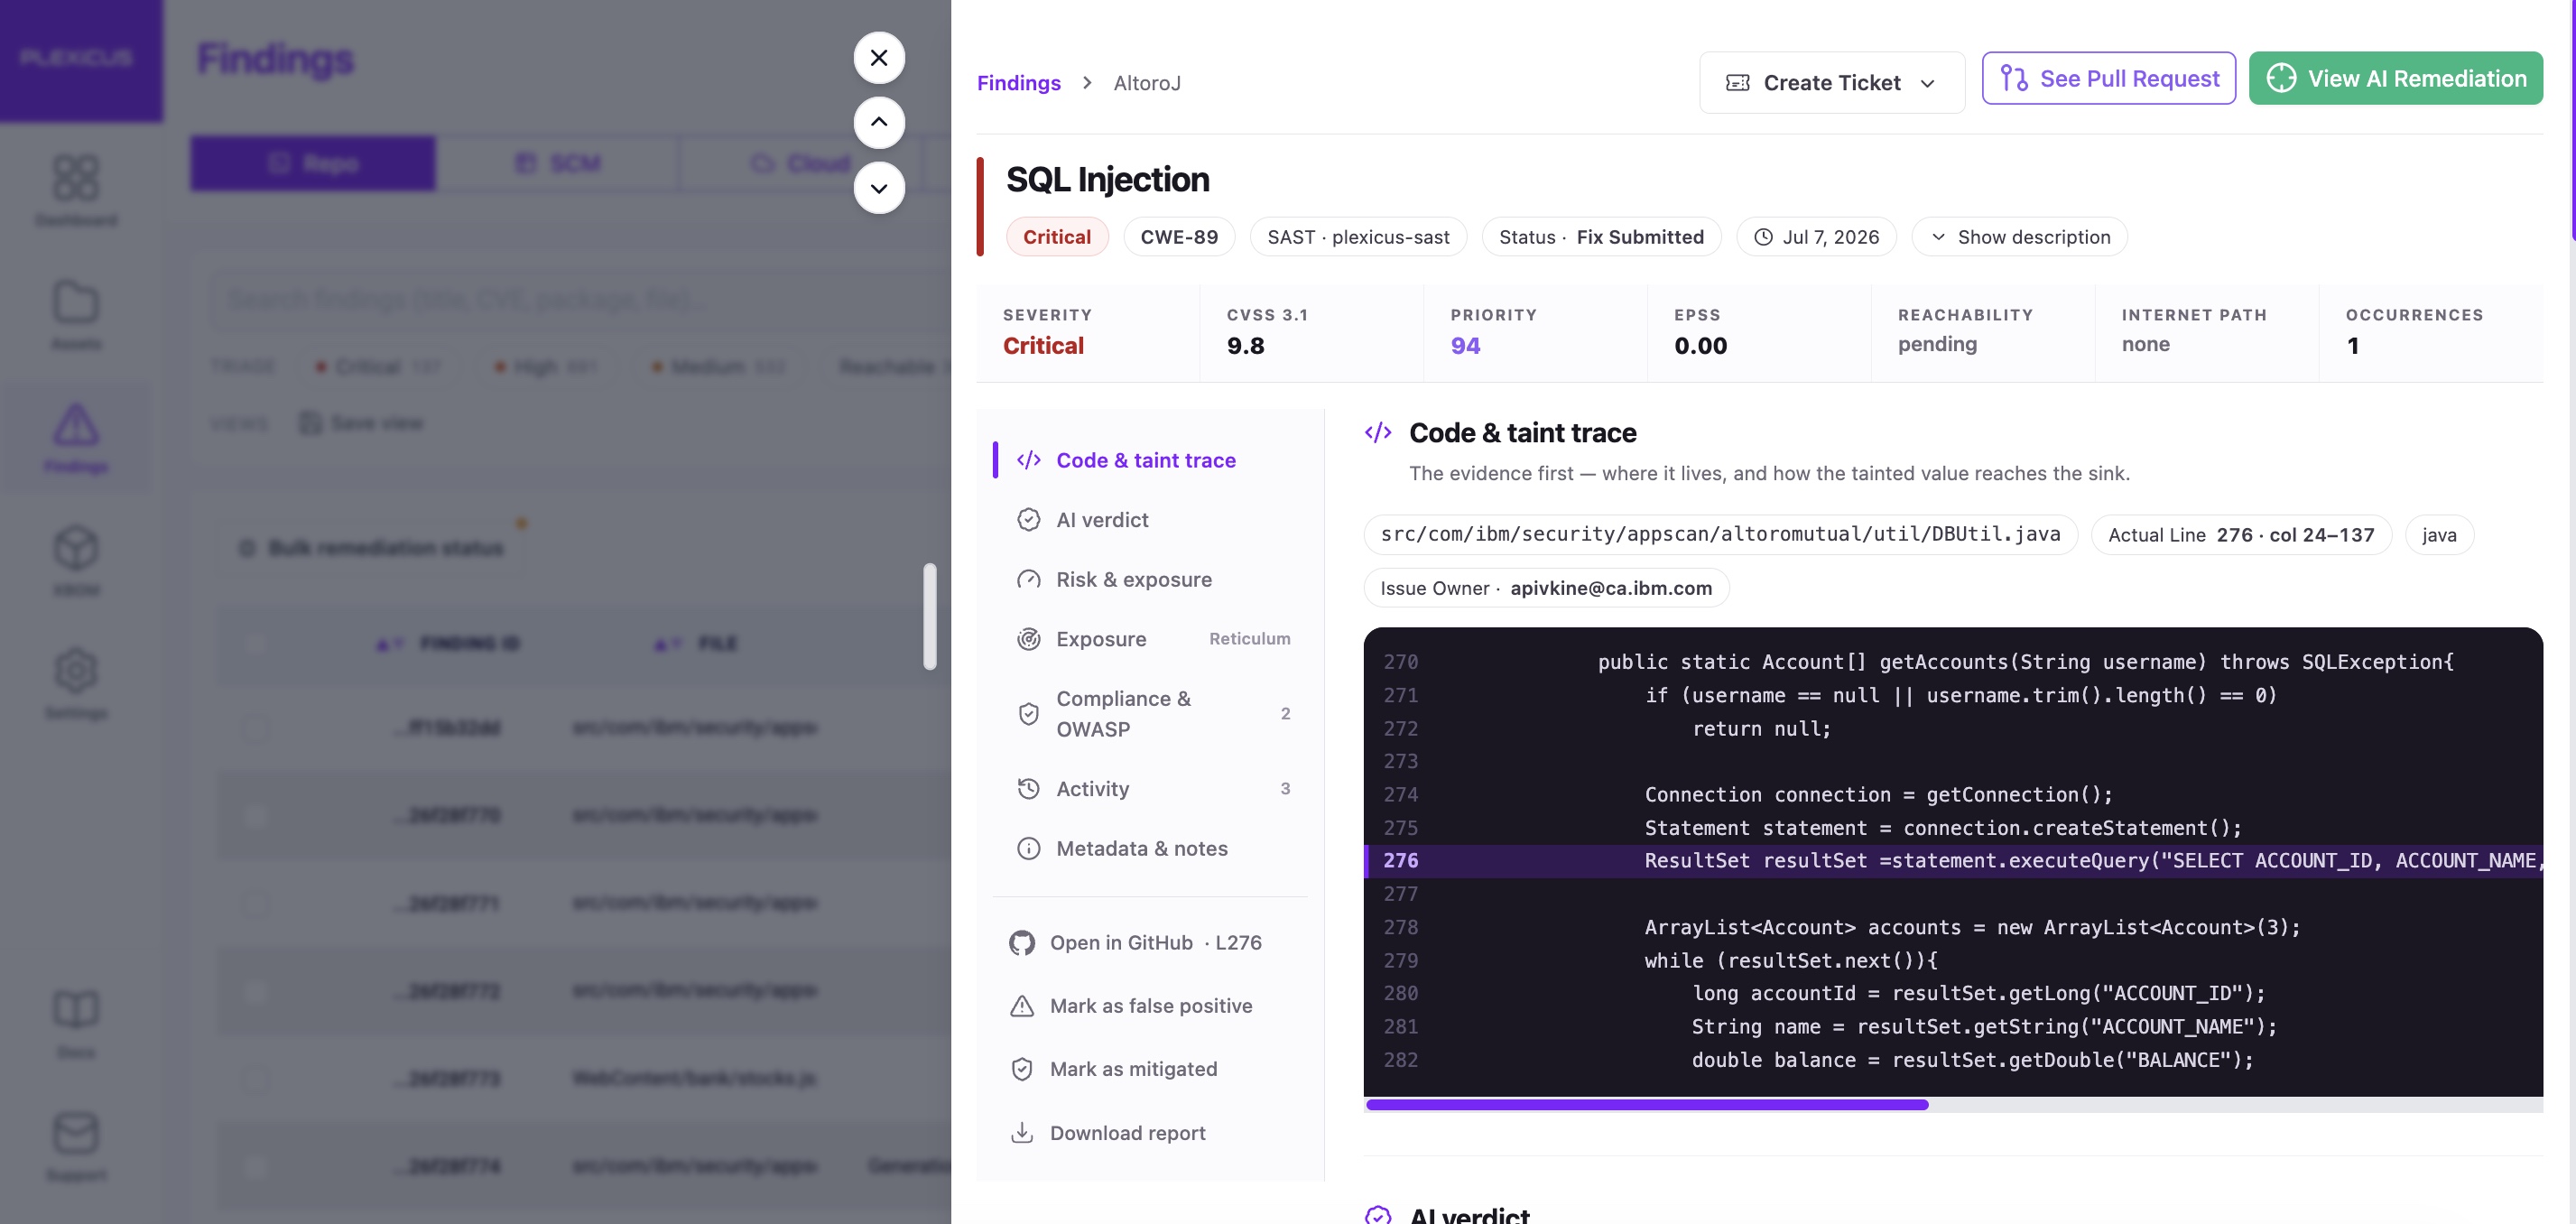
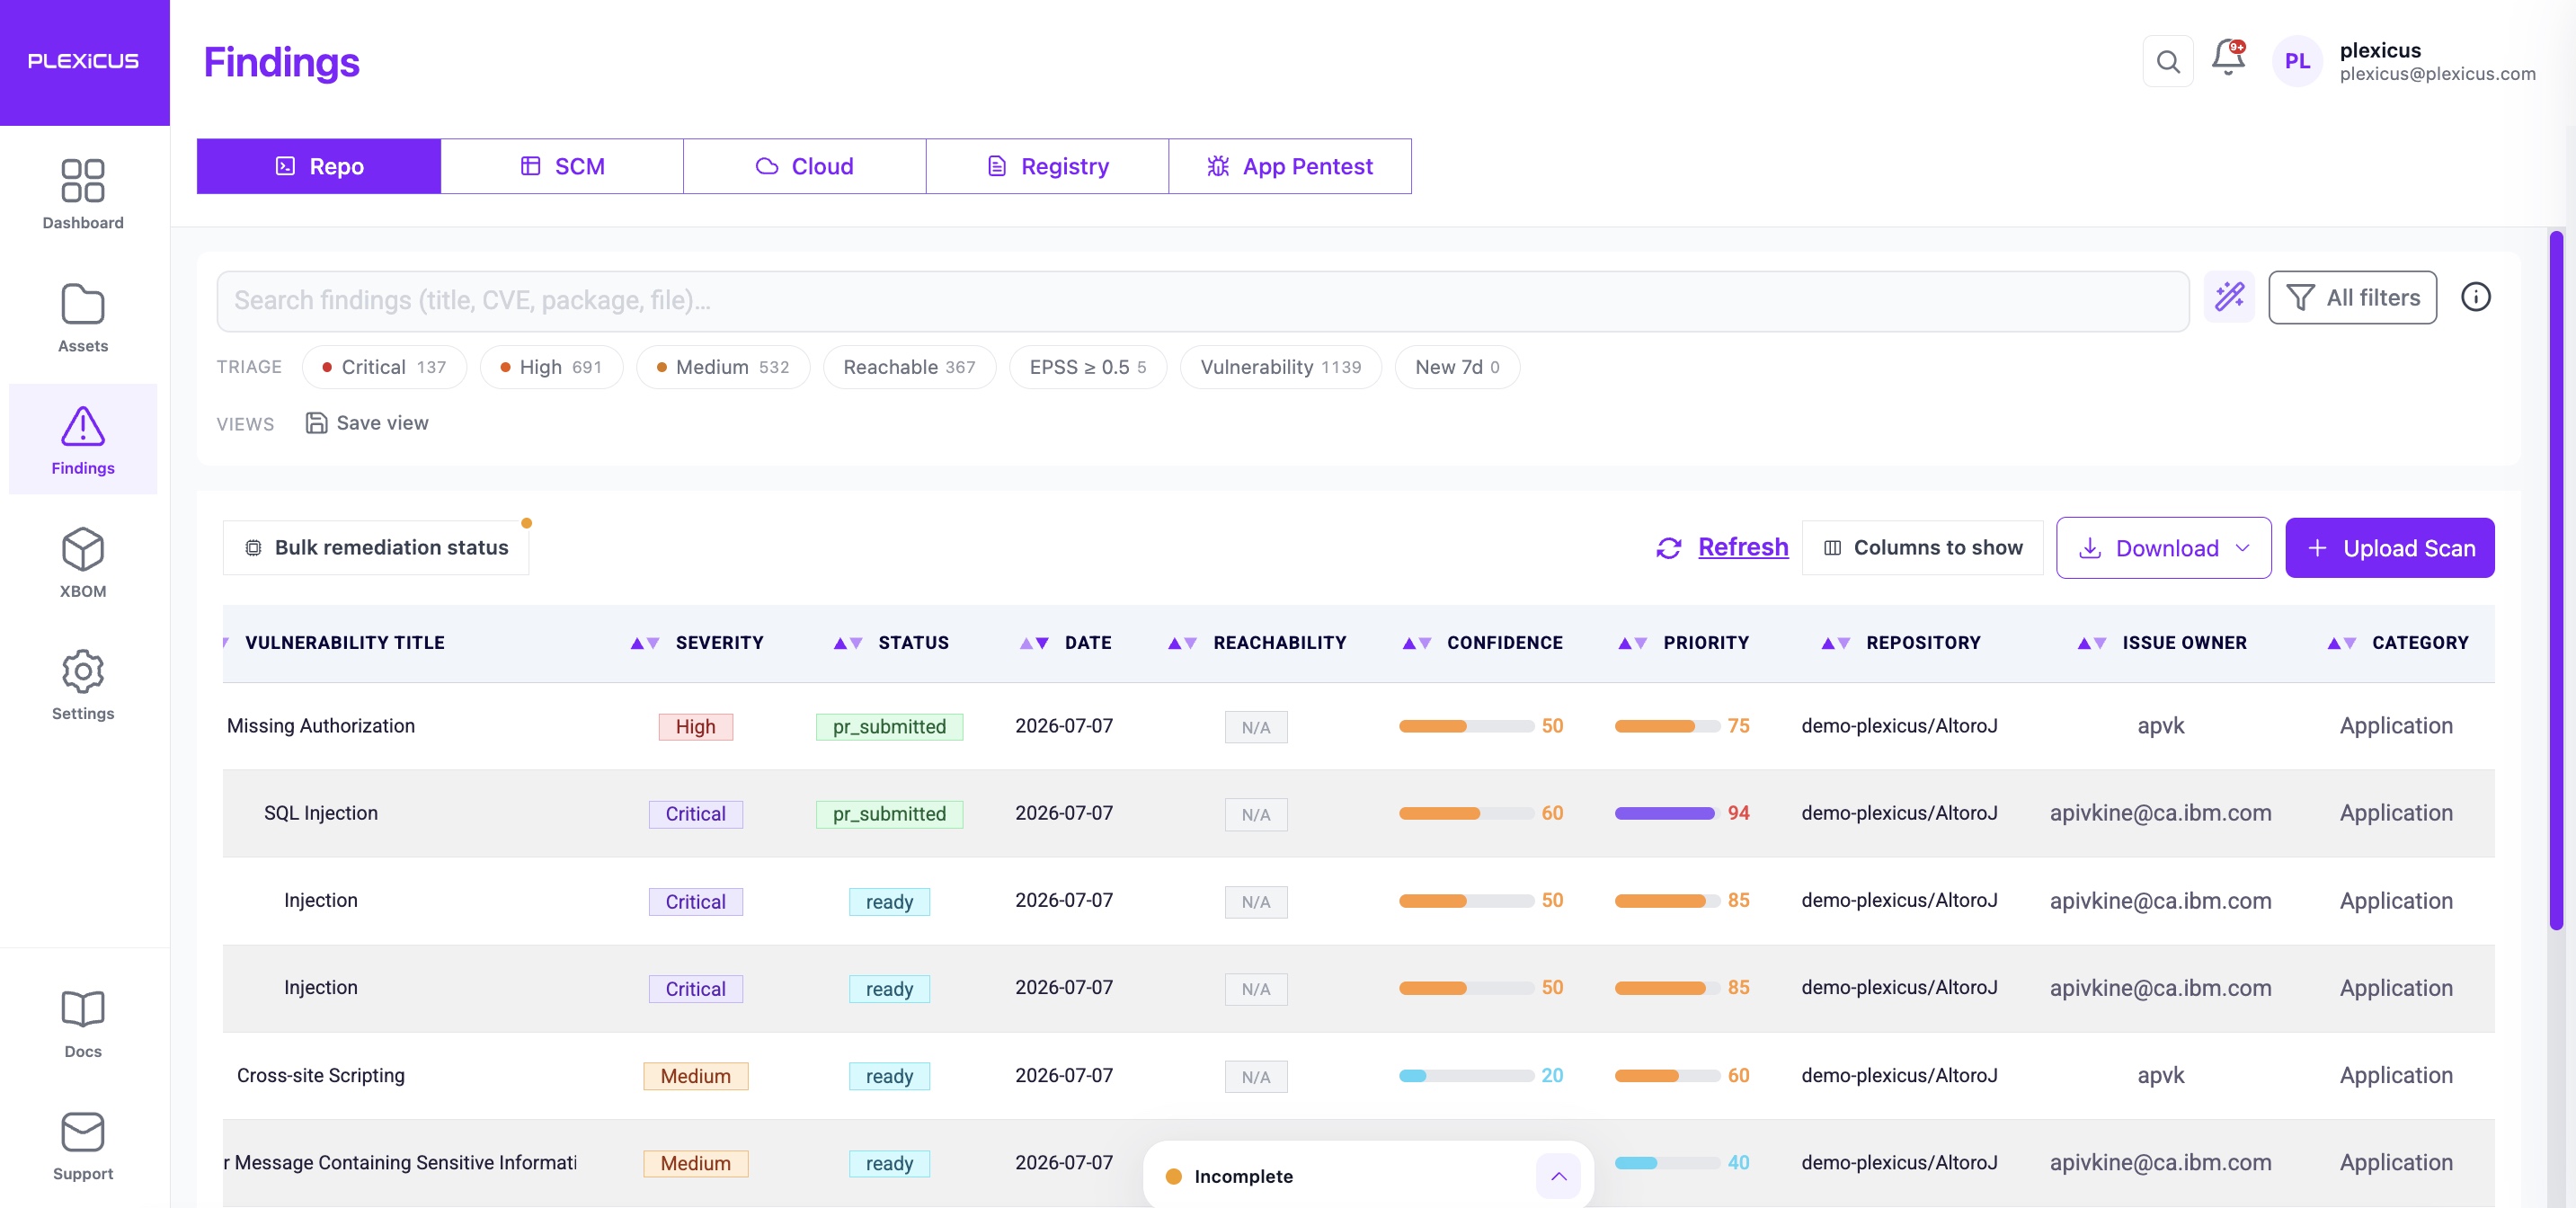
Plexicus product view showing security context and reviewed evidence
STEP 01 Security context
Plexicus findings view showing severity and review context
STEP 02 Validated finding context
Plexicus finding detail showing a remediation proposal for review
STEP 03 Reviewer-ready change

Live product view of the Plexicus Remediation workflow.
WHAT GETS FIXED

Remediation patterns for modern software teams.

Plexicus connects the proposed change to the evidence so your team can review the reason, scope, and expected outcome.

FIX 01

AI-introduced flaws

Address unsafe patterns introduced while building with AI coding tools.

FIX 02

Classic application flaws

Prepare fixes for common injection, access-control, and validation issues.

FIX 03

Business-logic flaws

Preserve the context needed to review authorization and workflow changes.

FIX 04

Dependency exposure

Keep version changes and test coverage attached to the remediation proposal.

THE PROOF

Every proposed change carries the evidence that produced it.

Evidence Observed behavior and supporting evidence attached
Risk context Impact, scope, and surrounding controls reviewed
Fix explanation The proposed change and the reason it addresses the finding
Review scope Relevant source locations linked for the reviewer
Handover Tests and follow-up checks included for human approval
THE WORKFLOW

From validated finding to reviewer-ready change.

Keep the original evidence attached while a proposed fix, tests, and review handover are prepared.

01

Validate the finding and preserve its evidence

02

Draft the change with tests and review context

03

Return control to your engineering reviewer

WORKFLOW

Fits the tools your team already uses.

Proposed changes and evidence stay in the repository and review systems your engineers already trust.

Repos GitHub · GitLab · Bitbucket
Tracker Linear · GitHub Issues
Chat Slack · Microsoft Teams
Alerting PagerDuty · Opsgenie
GRC Drata · Vanta · Tugboat Logic
REMEDIATION

See how validated evidence becomes a reviewer-ready change.

Book a walkthrough to review the evidence, proposed fix, and human approval flow against a synthetic sample.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit
Do you have a recent classic pentest you're not happy with?

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)