Tag:

application security

5 articles

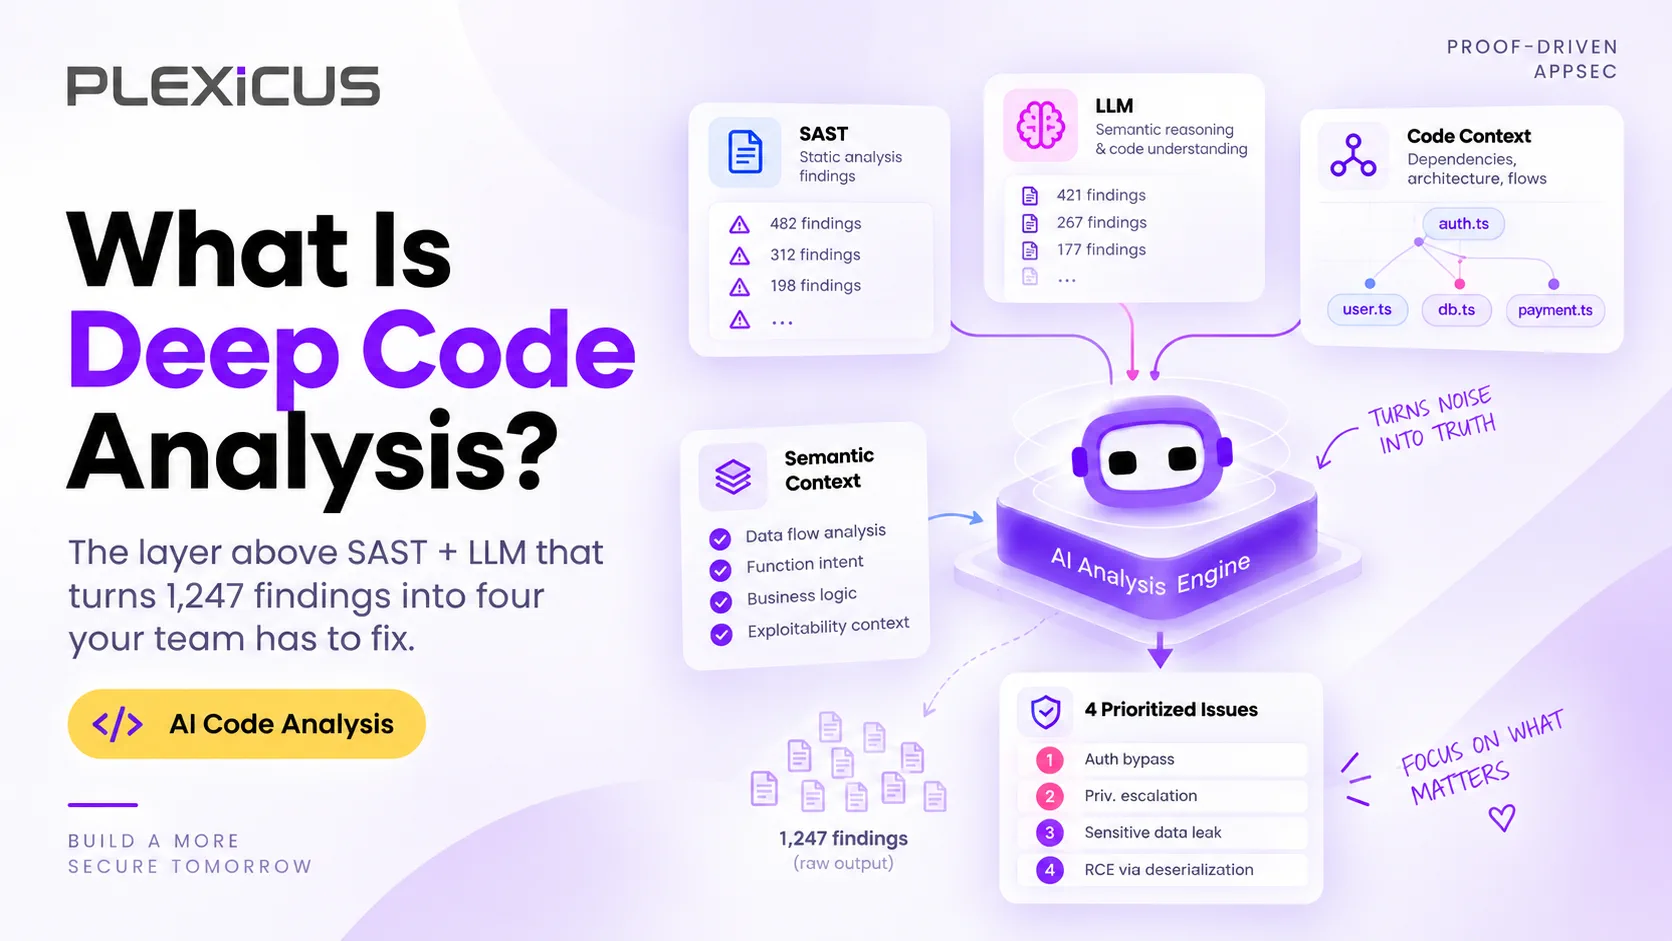
What Is Deep Code Analysis? (And Why SAST + LLM Isn't Enough)
AI Code Analysis

What Is Deep Code Analysis? (And Why SAST + LLM Isn't Enough)

Regex SAST gives you thousands of theory-class findings. LLM-assisted review gives you confident rewrites that may not run. Deep Code Analysis is the third layer: a structural model of your code that proves which findings are real, reachable, and worth fixing.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
Ostateczny przewodnik konsultacyjny po zarządzaniu postawą bezpieczeństwa aplikacji (ASPM)
Application Security

Ostateczny przewodnik konsultacyjny po zarządzaniu postawą bezpieczeństwa aplikacji (ASPM)

Jeśli dziś tworzysz lub prowadzisz oprogramowanie, prawdopodobnie żonglujesz mikroserwisami, funkcjami bezserwerowymi, kontenerami, pakietami zewnętrznymi i lawiną pól wyboru zgodności. Każda ruchoma część generuje własne ustalenia, pulpity i gniewne czerwone alerty. Wkrótce widoczność ryzyka przypomina jazdę we mgle w San Francisco o 2 nad ranem — wiesz, że niebezpieczeństwo jest tam, ale nie możesz go do końca dostrzec.

José Palanco José Palanco ·
Plexicus i Céfiros wzmacniają cyberbezpieczeństwo w 19 krajach
Cybersecurity

Plexicus i Céfiros wzmacniają cyberbezpieczeństwo w 19 krajach

Nowa współpraca między Plexicus a Céfiros ma na celu zwiększenie bezpieczeństwa aplikacji w 19 krajach w Ameryce Łacińskiej i na Półwyspie Iberyjskim. Ta współpraca w zakresie cyberbezpieczeństwa wprowadza zaawansowane rozwiązania do zarządzania postawą bezpieczeństwa aplikacji (ASPM) dla organizacji dążących do proaktywnej obrony przed zagrożeniami cybernetycznymi.

José Palanco José Palanco ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

Teams with fewer than 50 developers: start a 14-day Trial instead of booking a demo. Start a 14-day Trial →

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)