Tag:

Application Security

12 articles

AI in Application Security: Automation vs. Augmentation
Application Security

AI in Application Security: Automation vs. Augmentation

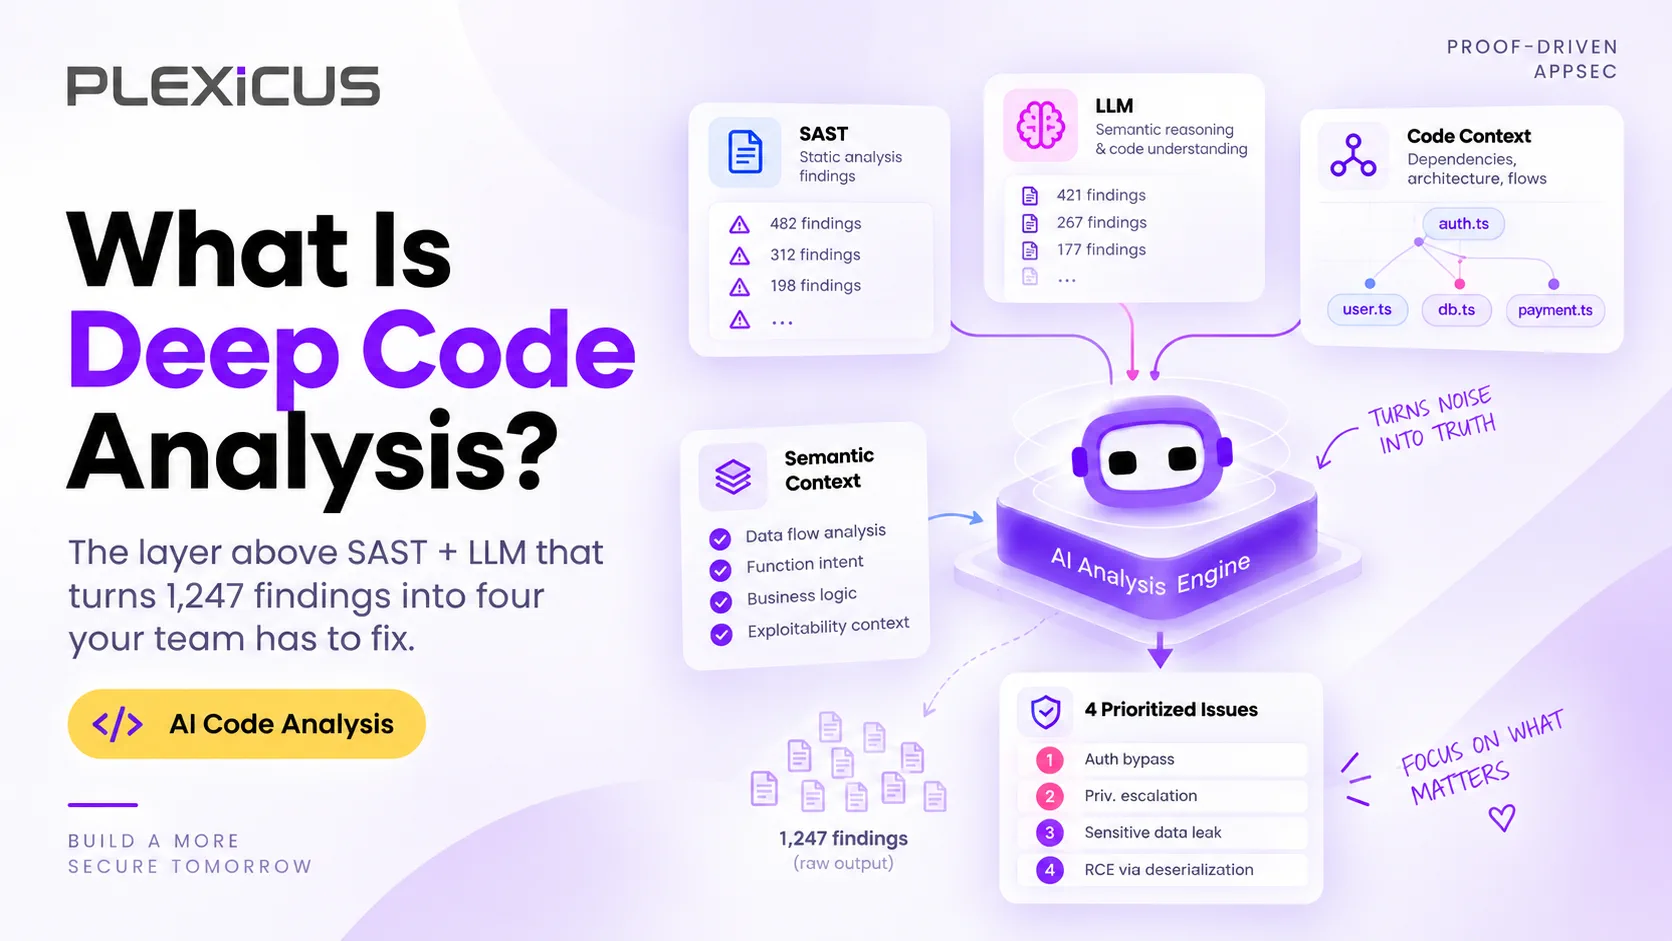
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.

José Palanco José Palanco ·
Uygulama Güvenliği Duruş Yönetimi (ASPM) için Nihai Danışmanlık Rehberi
Application Security

Uygulama Güvenliği Duruş Yönetimi (ASPM) için Nihai Danışmanlık Rehberi

Bugün yazılım geliştiriyor veya çalıştırıyorsanız, muhtemelen mikro hizmetler, sunucusuz işlevler, konteynerler, üçüncü taraf paketler ve bir uyum kontrol listesi seliyle uğraşıyorsunuzdur. Her hareketli parça kendi bulgularını, panolarını ve kızgın kırmızı uyarılarını doğurur. Kısa sürede, risk görünürlüğü San Francisco sisinde sabah 2'de araba kullanmak gibi hissettirir—tehlikenin orada olduğunu biliyorsunuz ama tam olarak göremiyorsunuz.

José Palanco José Palanco ·
Plexicus ve Céfiros 19 ülkede Siber Güvenliği Güçlendiriyor
Cybersecurity

Plexicus ve Céfiros 19 ülkede Siber Güvenliği Güçlendiriyor

Plexicus ve Céfiros arasında yeni bir iş birliği, Latam ve İberya'daki 19 ülkede uygulama güvenliğini artırmayı hedefliyor. Bu siber güvenlik iş birliği, siber tehditlere karşı proaktif savunma arayan kuruluşlara gelişmiş Uygulama Güvenliği Duruş Yönetimi (ASPM) çözümleri sunuyor.

José Palanco José Palanco ·
Ready to validate what matters?

Ready to validate what matters?

Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorized target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)
Private Round For investors