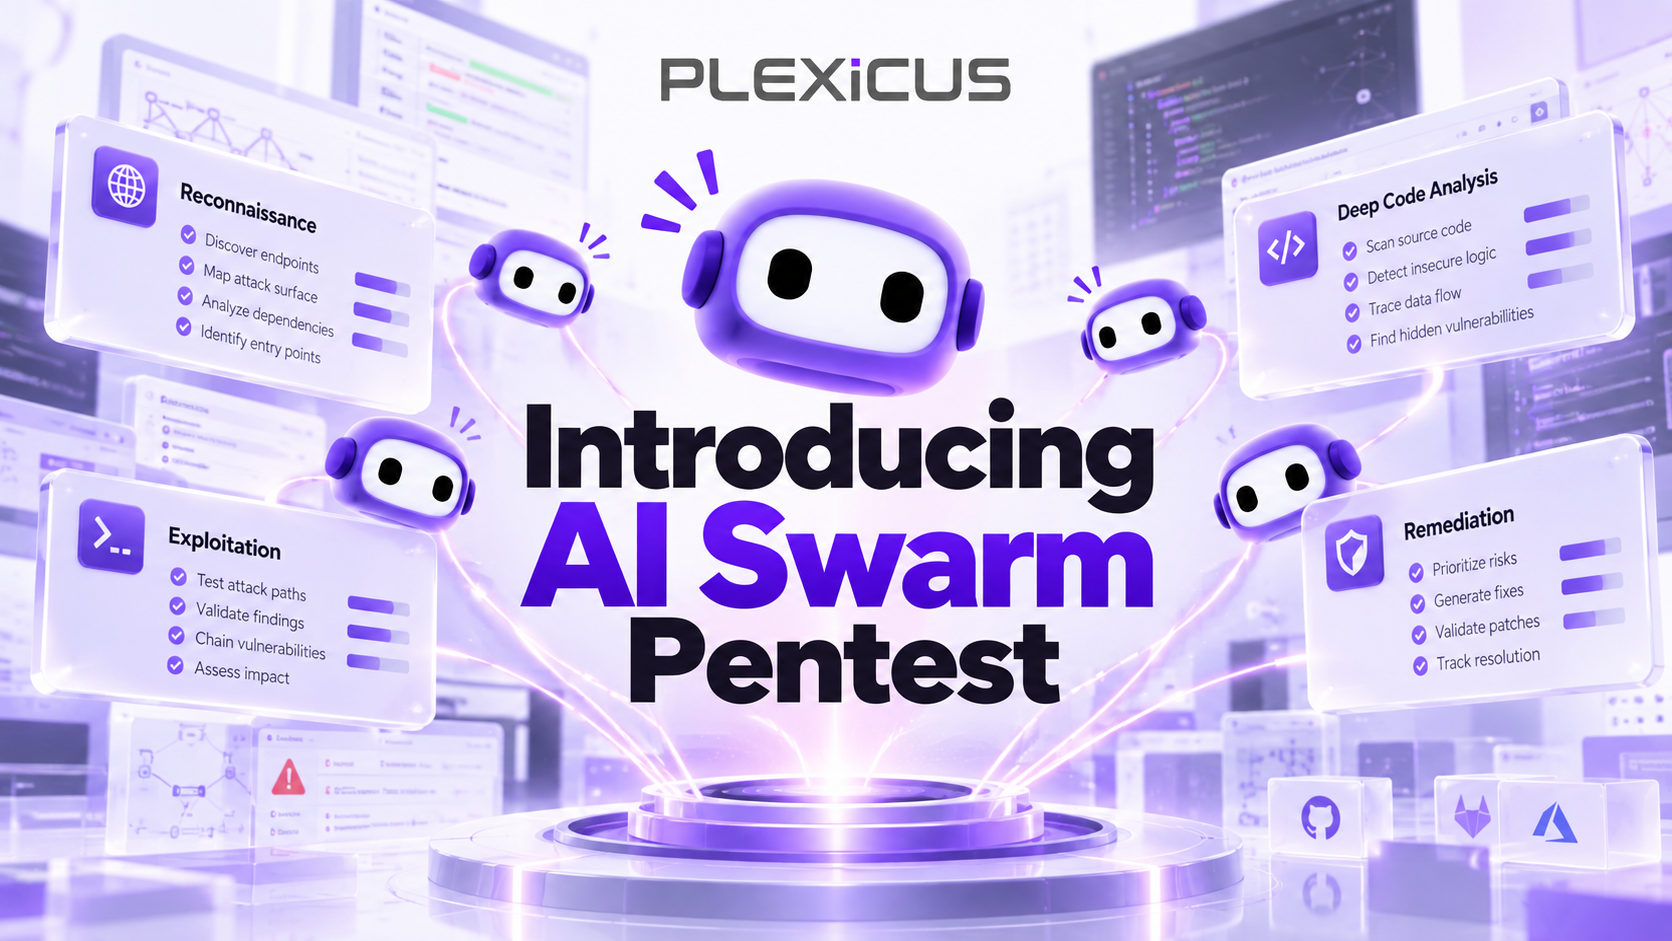
Introducing AI Swarm Pentest: From One AI Pentester to an Orchestrated Team of Attack Agents
How specialized attack agents share context, challenge hypotheses, and independently verify attack paths inside the Plexicus Proof-Driven AppSec workflow.
10 articles
How specialized attack agents share context, challenge hypotheses, and independently verify attack paths inside the Plexicus Proof-Driven AppSec workflow.
A complete guide to application security in 2026, from secure design and software supply chains to testing, exploit validation, remediation, and Proof-Driven AppSec.
A fruit-fly connectome offers a vivid test of a security principle: a demo is not proof until controls show what the advertised system contributes.
DevDay 2026 connected persistent agents, cloud coding, plugins, events, and shared work. Here is what shipped, what is still coming, and where AppSec boundaries lie.
Opus 5.5 motion-graphics demos reveal an agentic loop: plan, write code, run it, inspect, revise. Claude cybersecurity now depends on verification keeping pace.
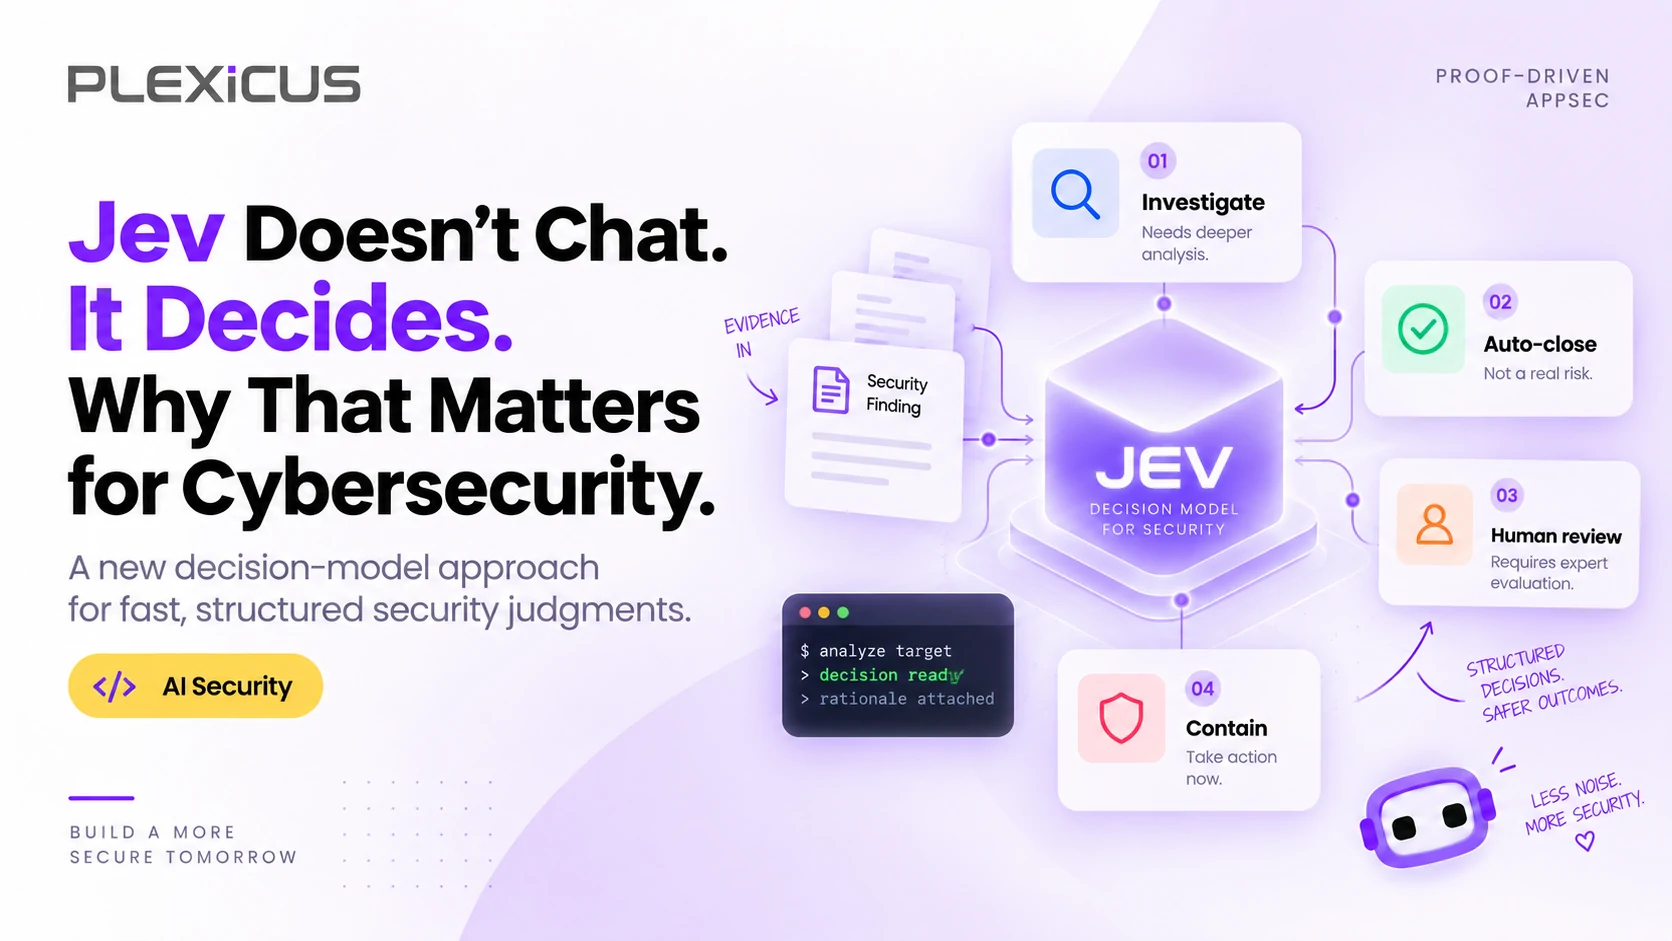
Jev AI returns typed decisions instead of prose. That could change where semantic judgment fits in security workflows, if teams keep policy, fallbacks, verification, and human review.
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.
Bezpečnostní nástroje mají pověst hlučných překážek. Když vývojář nasadí kód a CI/CD pipeline selže s přiloženou 500stránkovou PDF zprávou, jejich přirozenou reakcí není opravit problémy. Je to ignorovat je nebo vynutit sloučení kódu.
V tomto průvodci se naučíte, jak se posunout od ručního opravování a vytvořit pracovní postup, který automaticky detekuje, prioritizuje a napravuje zranitelnosti SQLi pomocí automatizace řízené AI.
Pokud dnes vyvíjíte nebo provozujete software, pravděpodobně žonglujete s mikro-službami, serverless funkcemi, kontejnery, balíčky třetích stran a lavinou kontrolních políček pro dodržování předpisů. Každá pohyblivá část generuje vlastní nálezy, dashboardy a rozzlobené červené výstrahy. Než se nadějete, viditelnost rizik se cítí jako řízení v mlze v San Franciscu ve 2 ráno - víte, že nebezpečí je tam venku, ale nemůžete ho úplně vidět.
Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.