Microsoft's Only Exploited Patch Tuesday Bug Scored 6.5. 861 Other CVEs Scored Higher
Microsoft's exploited Outlook zero-day scored 6.5. We ranked the 1,085 scored CVEs published that day and found 861 above it.
Beyond ASPM
Proof-Driven AppSec for teams building with AI
Plexicus uses AI Swarm Pentest to explore authorized application paths, validate what is exploitable, and give teams evidence they can use to prioritize remediation.
Explore AI Swarm PentestOn November 10, Microsoft shipped its November security update. It flags one flaw in the update as exploited: CVE-2026-124194, an Outlook spoofing bug. Microsoft rated it Moderate with a CVSS base score of 6.5.
We pulled Microsoft’s own update data and ranked the CVEs it published that day. Of the 1,085 that carry a base score, 861 scored higher than the bug under attack. None of the 23 CVEs scored 9.0 or above is flagged as exploited.
Severity tells you how bad a bug could be, not whether anyone is using it. Rapid7 made a version of this point about volume on release day. This post adds a ranking of the exploited bug and a 23-month series, then turns both into a triage rule.
How big was Microsoft’s November 10 update?
The answer depends on who counts. CyberScoop and SecurityWeek report 1,094. Rapid7 reports 1,092 own-product vulnerabilities, and CrowdStrike reports 1,252.
We counted from the source. Microsoft publishes each monthly update as a machine-readable document through its Security Response Center API. We retrieved the November document on November 16 (SHA-256 starting 0e75cdf1) and grouped CVE IDs by the date of the earliest entry in each record’s RevisionHistory.
| Count | What it covers |
|---|---|
| 1,094 | CyberScoop and SecurityWeek, as stated in each article |
| 1,092 | Rapid7, “own-product” vulnerabilities |
| 1,252 | CrowdStrike, as stated in its analysis |
| 1,096 | Our count: CVE IDs first published on November 10 |
| 1,093 | The same, limited to the 08 release batch |
| 1,644 | Every CVE ID in the document on November 15, after later revisions |
The 08
batch holds 1,093 IDs, within one of the 1,092 to 1,094 that three outlets report. Our 1,096 adds three third-party IDs stamped seven hours earlier. The document holds 252 more IDs first published between November 4 and 9, and 296 added between November 11 and 13.We use the 1,096 throughout, because the same rule works for all 23 months. The 08
batch gives 860 CVEs above 6.5, not 861. October lands within three: CyberScoop reports a record 1,413 and we count 1,416.Microsoft’s release-day count averaged 98 CVEs a month in 2025. From June to November 2026 it averaged 844, and it peaked at 1,416 in October.
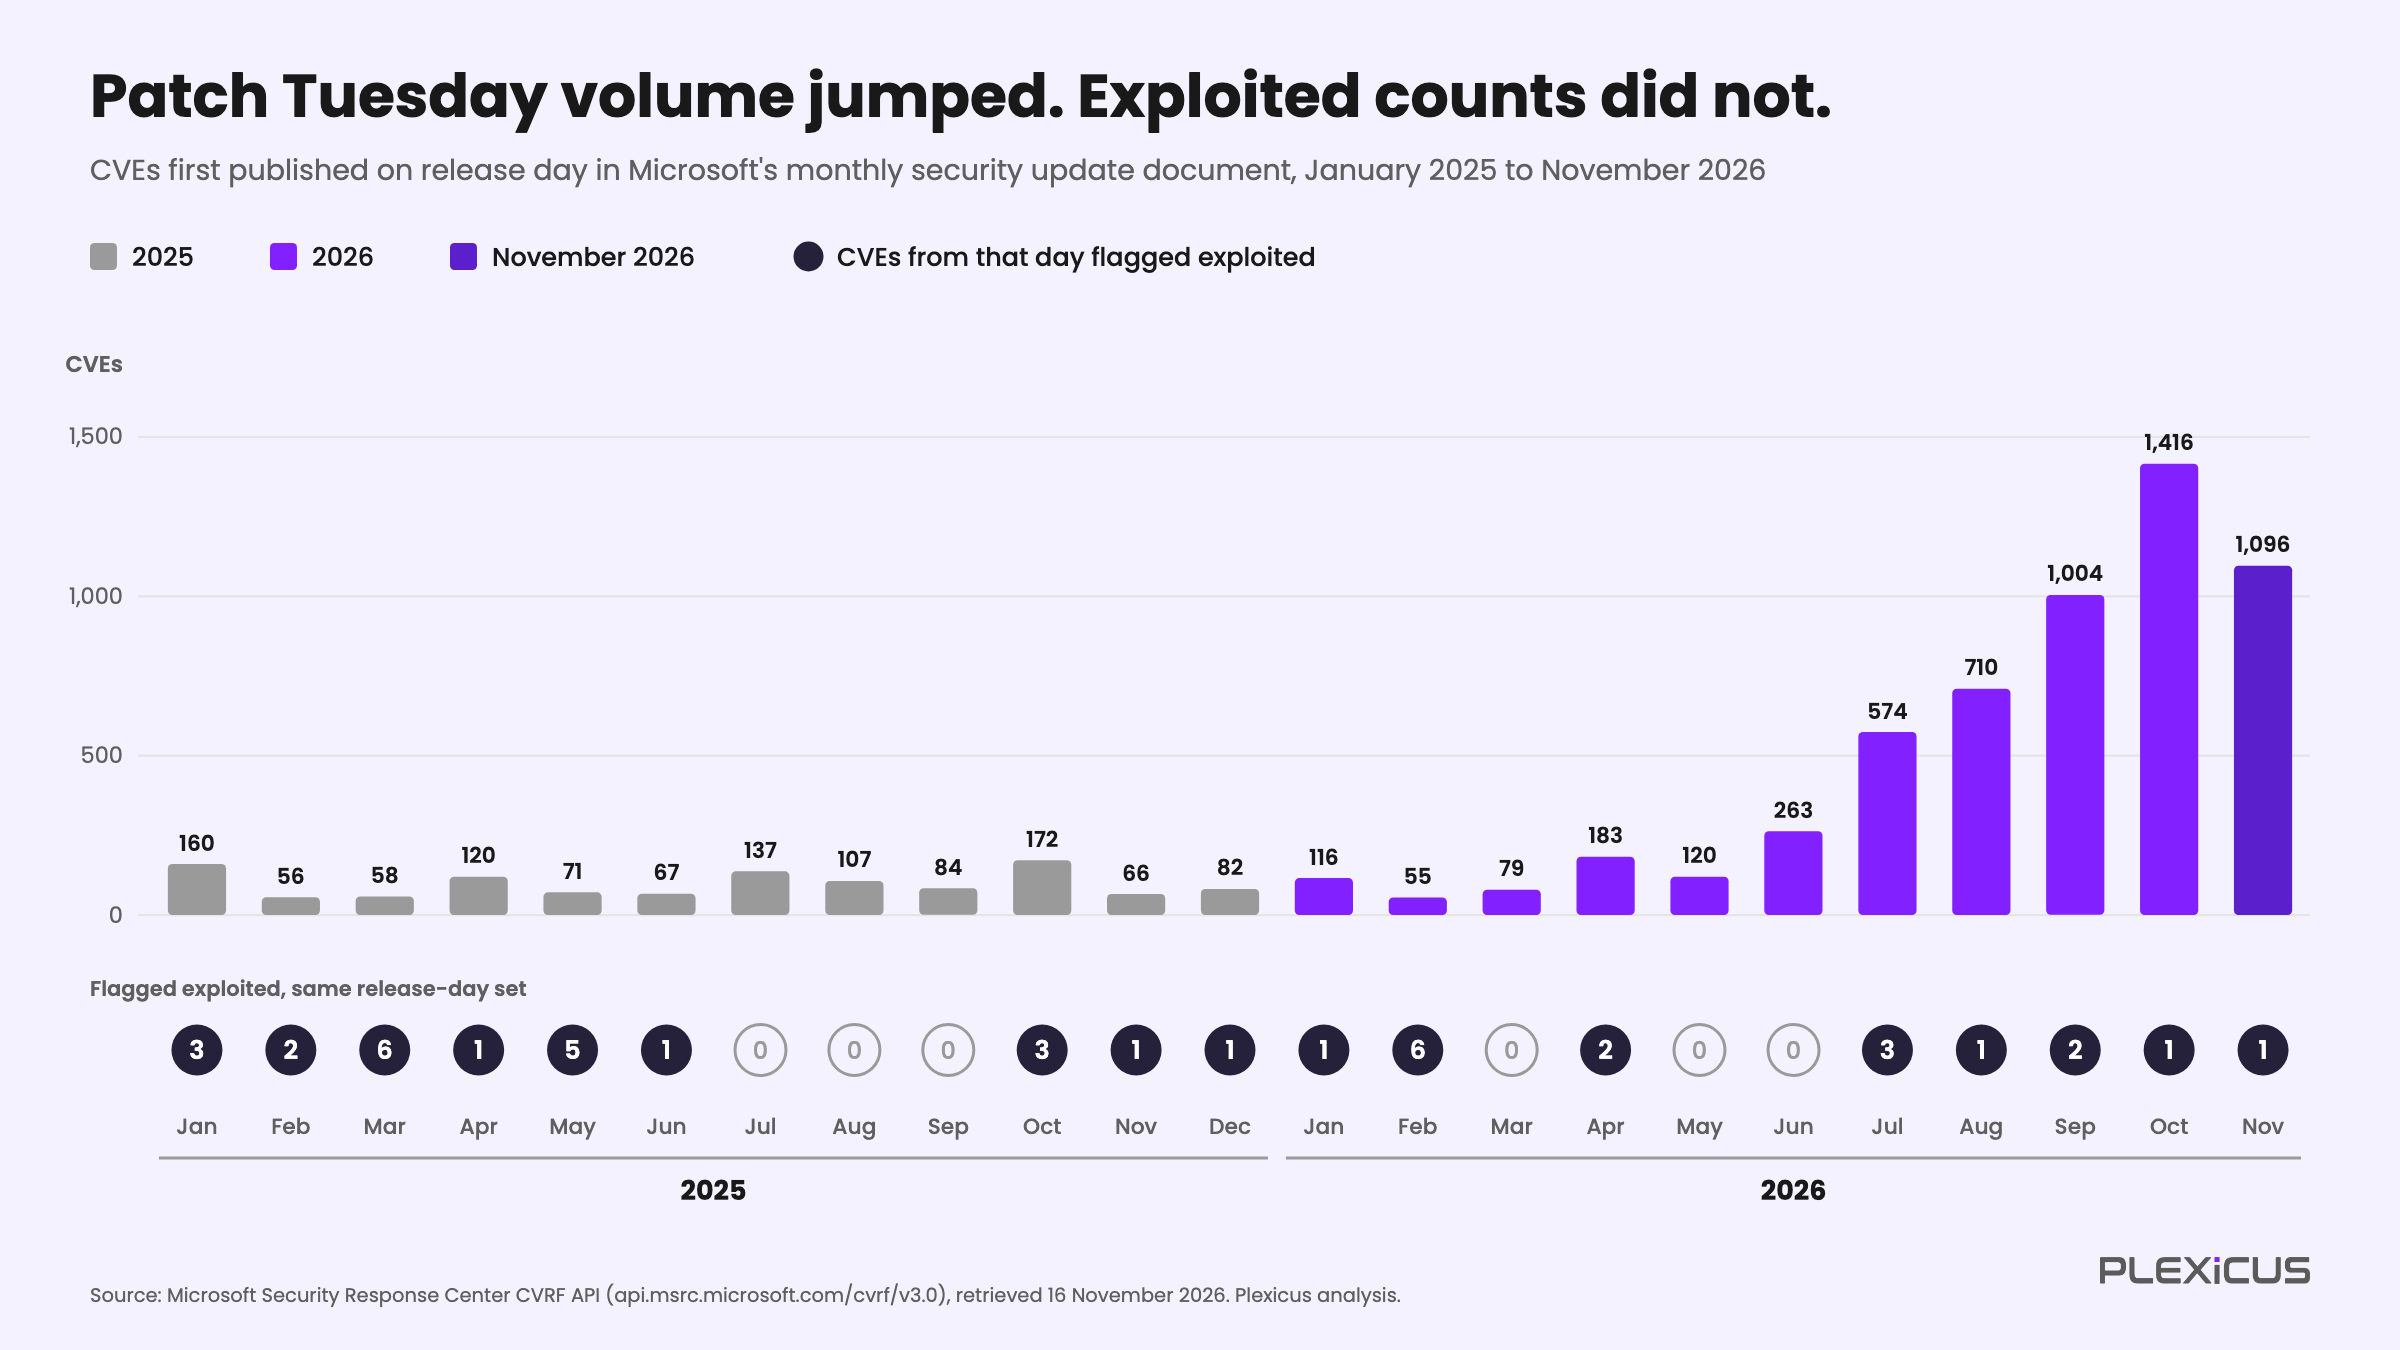
Original Plexicus chart built from Microsoft’s MSRC update documents, retrieved November 16, 2026. It is not a Microsoft chart.
Not every ID carries an exploitation assessment. The ones that do not include third-party components listed for Edge and Azure Linux. From June to November 2026, 4,653 of the 5,063 release-day IDs carry one, and eight of those are flagged exploited: 0.17%. In 2025 the same measure is 23 of 1,141, or 2.0%.
The pile of CVEs grew about eightfold. Flagged exploited bugs held at 1.9 a month in 2025 and 1.3 a month from June to November 2026.
How does the Outlook bug work, and why is it only Moderate?
Microsoft’s advisory says an attacker sends a crafted message file and persuades a user to open it. Outlook then connects to a network location the attacker controls, without the usual external-content warning. Microsoft says the flaw discloses the user’s NTLMv2 hash, which the attacker could use to authenticate as that user.
CrowdStrike and Rapid7 repeat that account, and CrowdStrike adds that the Preview Pane is not an attack vector. SecurityWeek notes that the advisory gives no detail about observed attacks, and no source names the protocol that carries the hash out.
The weakness is CWE-356: the product UI does not warn the user of an unsafe action. The base vector explains the 6.5. The bug needs a network path and a user who opens the file, and it affects confidentiality only.
Microsoft’s vector also carries temporal metrics: High exploit code maturity and an official fix. They give a temporal score of 6.2, and this is the only CVE published that day with the High maturity flag. Ranked by temporal score, 627 CVEs still sit above it, against 861 by base score.
The base score does not move when attacks start. Rapid7 calls 6.5 relatively low and says it does not tell the full story, because the bug serves both commodity and targeted attackers.
Outlook has leaked NTLM material before. Microsoft’s 2023 guidance for CVE-2023-23397 describes a crafted message that triggers a Net-NTLMv2 hash leak over SMB. That was a different bug.
Where does a 6.5 rank among the 1,085 scored CVEs?
The chart below plots every CVE first published on November 10 that carries a base score. CVE-2026-124194 is one of 59 that scored exactly 6.5, and another 165 scored lower. The other 861, or 79%, scored higher.
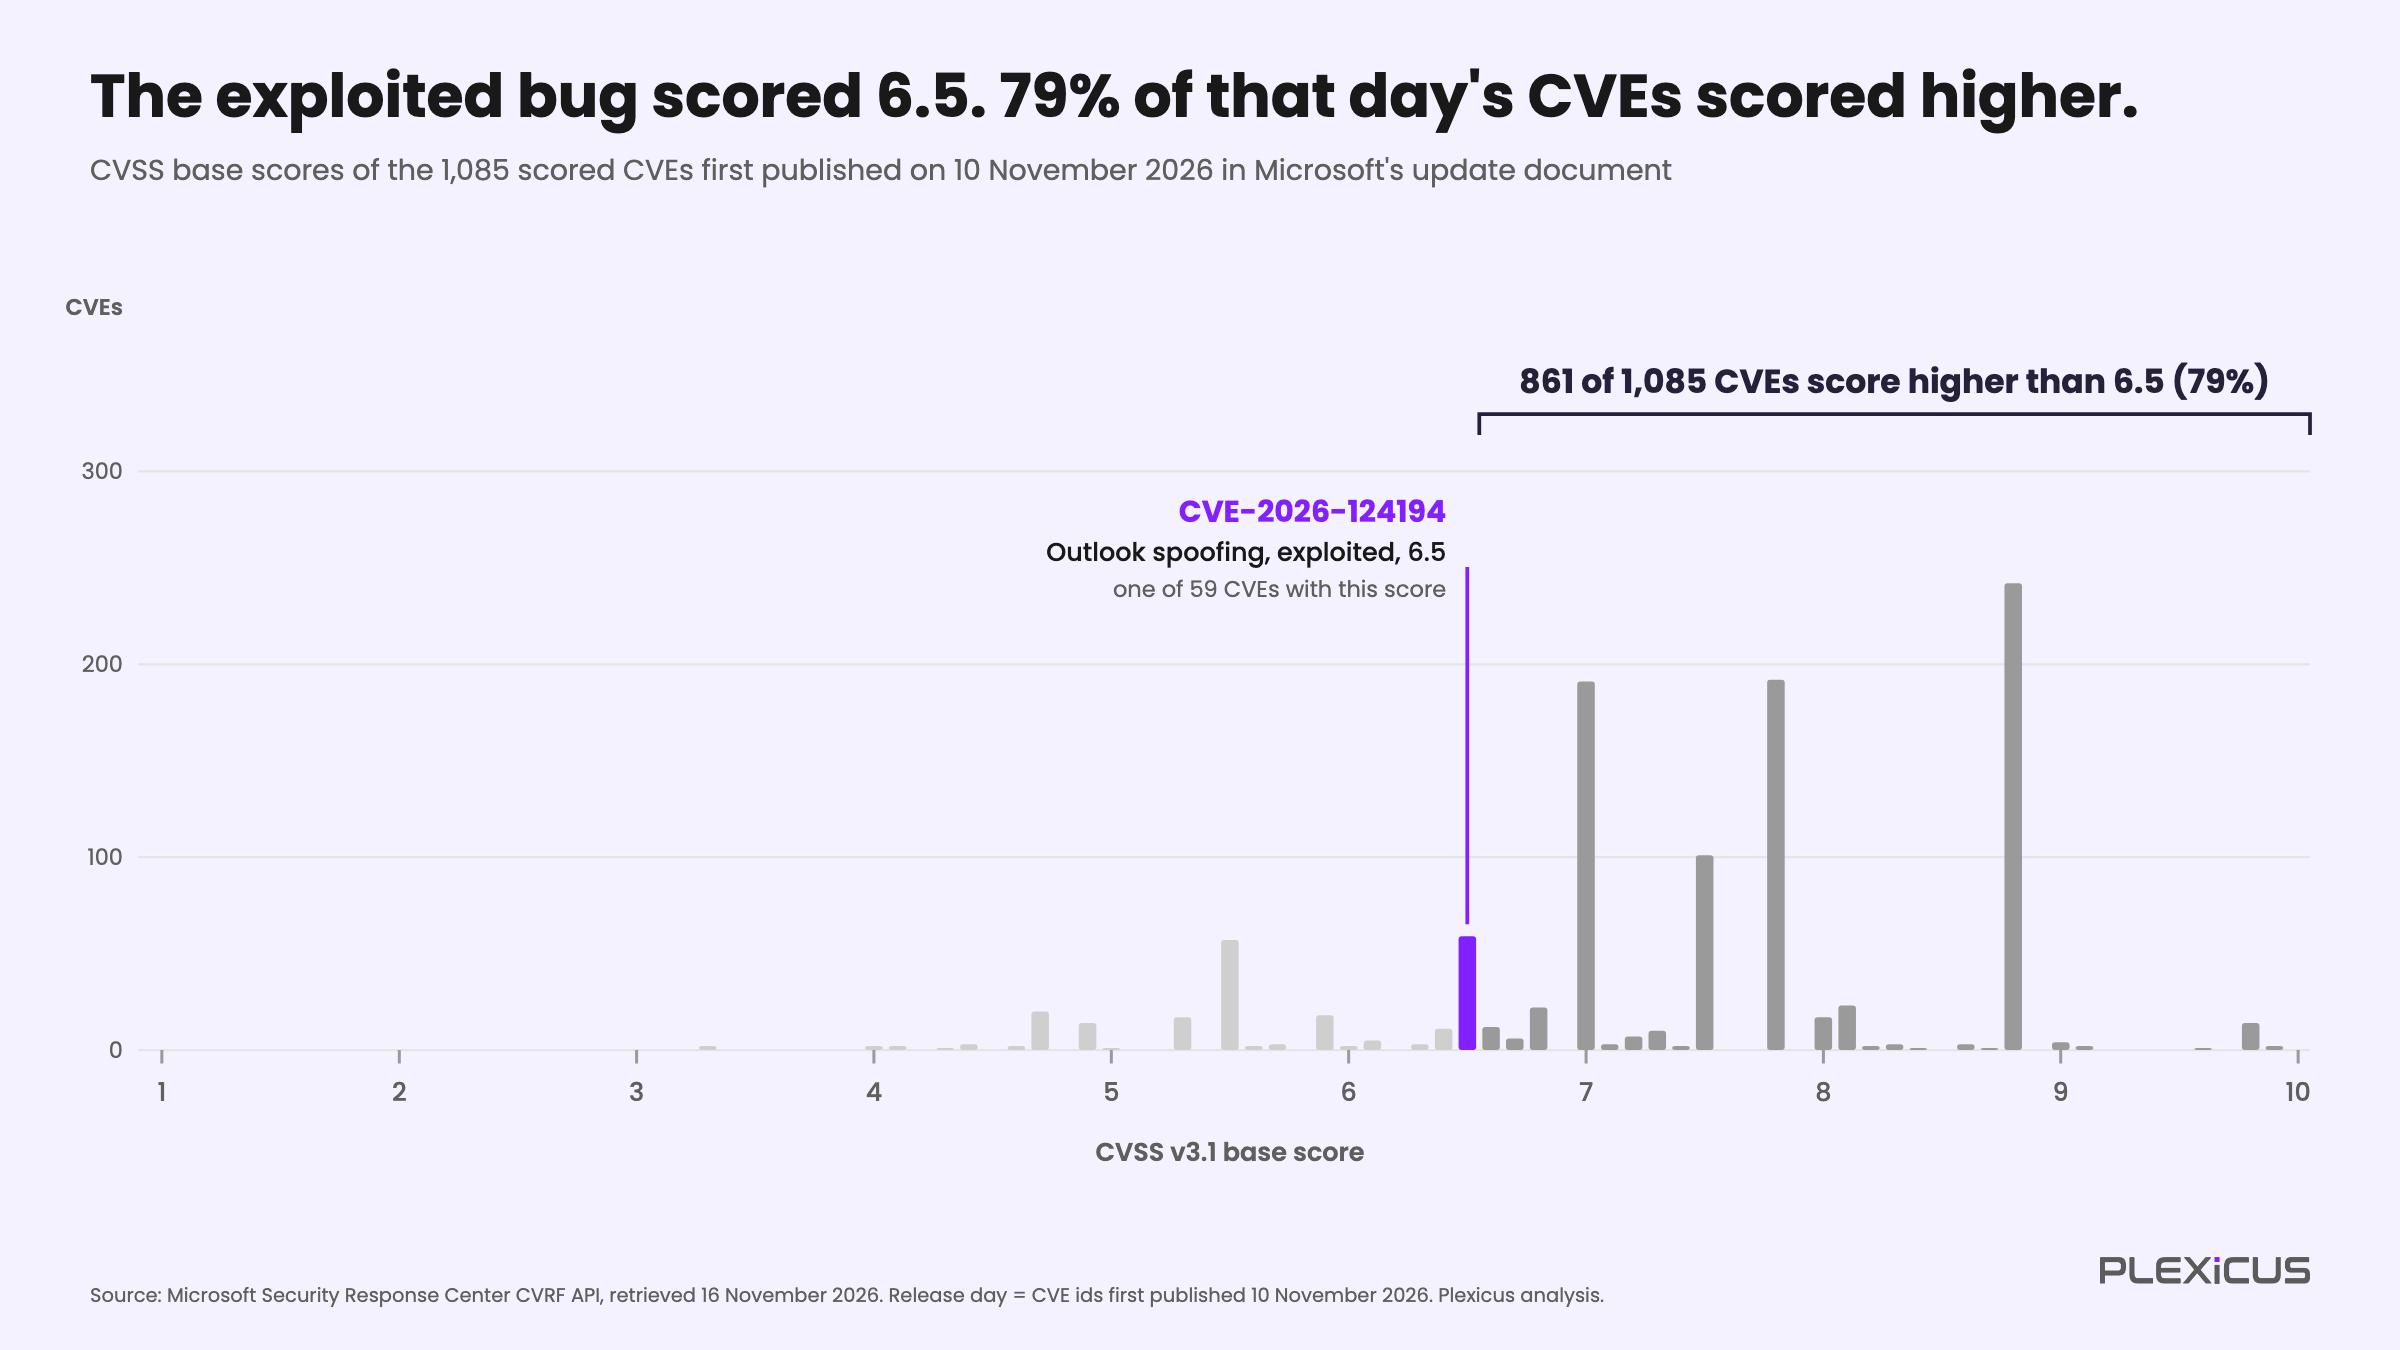
Original Plexicus chart built from Microsoft’s MSRC update document for November 2026, retrieved November 16, 2026. It is not a Microsoft chart.
None of the 23 CVEs that scored 9.0 or higher is flagged by Microsoft or listed in KEV. The table shows four of them, the two at 9.9 and two at 9.8 that CyberScoop discusses, next to the Outlook bug.
| CVE | Product and impact | CVSS | Microsoft’s exploitability call | EPSS, November 15 |
|---|---|---|---|---|
| CVE-2026-109467 | Azure DevOps Server, remote code execution | 9.9 | N/A | 0.7% |
| CVE-2026-120002 | SharePoint Server, elevation of privilege | 9.9 | Exploitation less likely | 0.9% |
| CVE-2026-116928 | Windows Search, remote code execution through Exchange | 9.8 | Exploitation less likely | 1.2% |
| CVE-2026-119958 | Windows LDAP, remote code execution | 9.8 | Exploitation less likely | 1.3% |
| CVE-2026-124194 | Outlook, spoofing | 6.5 | Exploitation detected | 1.6% |
EPSS, the model FIRST.org publishes, put the Outlook bug above all 23 CVEs at 9.0 or higher, at 1.6% against 0.6% to 1.3%. Even so, 1.6% is a small probability, and a model estimate is not an observed attack.
Is November typical?
One month can mislead, so we ran the same ranking on all 23 monthly documents. Microsoft flags 40 release-day CVEs as exploited across them, and all 40 carry a base score.
Score is a real signal. In the median case about a quarter of that month’s scored CVEs ranked above the exploited one, and 20 of the 40 sat in their month’s top quarter. It is also an incomplete signal: nine of the 40 scored below 7.0, the lowest at 4.3, and 13 had more than half of their month above them.
What changed is depth. Before June 2026, a queue sorted by score reached the exploited CVE after a median of about 17 others, and never after more than 181. Since June it took a median of 285, and November’s 861 is the deepest of the 40.
Part of that is arithmetic: the same share of a bigger pile is a bigger number. That is the point, because the pile grew eightfold and flagged exploitation did not.
What does exploitation evidence give you that a score cannot?
Two sources named this bug on the day of release. Microsoft’s advisory marks it exploited and not publicly disclosed. CISA added it to its Known Exploited Vulnerabilities catalog the same day, with a November 24 due date for US federal agencies.
CISA’s record in NVD adds its decision data: exploitation active, technical impact partial, and automatable no, meaning CISA judged the attack cannot run at scale without a person in the loop.
Each says something a score cannot: someone is doing this now. Each has limits too. Microsoft’s flag reflects what Microsoft observed and covers the CVEs it assesses. KEV is broader: CISA adds a CVE when it has evidence of active exploitation.
The two can differ. Microsoft’s November document also lists third-party components, and two of them are in KEV without a Microsoft flag. CVE-2026-125350 is a Chromium bug listed for Microsoft Edge, and CVE-2026-123158 is an OpenSSH bug listed for Azure Linux packages. Neither was first published on November 10, and absence from either list is not evidence of safety.
CISA’s alert says its directive for federal agencies, BOD 26-04, requires them to prioritize rapid remediation of CVEs in KEV, and it encourages every organization to do the same. That supports a triage order. The November data tests only the first step:
- Confirmed exploitation, from the vendor or KEV. Fix first. Microsoft flagged one of the 1,096 CVEs published on November 10, and KEV lists two more third-party CVEs in the same document.
- Reachable in your environment, with a working proof of exploit. Fix next. This is our recommendation, and Microsoft’s data cannot test it.
- Score and EPSS. Use them to order what is left.
A team that sorted November by base score alone would have started with 23 CVEs scored 9.0 or higher. It would have reached the Outlook bug after 861 others.
The volume problem is not specific to Microsoft. OpenAI’s account of its Linux kernel pipeline, published on November 4, puts about 26% of its stated spend on finding candidates and the rest on validating, assessing and exploiting them. Those are OpenAI’s figures for one prototype, and none of our sources links that work to Microsoft’s volume.
What should your team do this week?
- Patch Outlook. Install Microsoft’s November update through your normal channel. The CVE record lists fixed builds: Office LTSC 2021 at 16.0.14334.21048 or later and Office LTSC 2024 at 16.0.17932.21140 or later. For Microsoft 365 Apps, check Microsoft’s release page.
- Harden against NTLM leaks. Microsoft’s record lists no workaround. Its 2023 guidance for CVE-2023-23397 recommended blocking outbound TCP 445 and adding high-value accounts to the Protected Users group, which blocks NTLM for them and can break applications that need it. Treat both as hardening for this class of leak, not as guidance written for this CVE.
- Hunt. Search firewall logs for outbound SMB attempts from user workstations to external addresses. This is a hypothesis: the 2023 guidance names firewall logs and SMB client events as places to look for the earlier bug.
- Test your own code. If your application opens a remote path or URL taken from untrusted content, such as attachments, previews or import features, check what happens with a UNC path or a
file://URL. A missing warning is the weakness CWE-356 describes. We have not tested this against any product. - Change your triage order. Put confirmed exploitation first, a working proof second and scores last. Count your open findings that pass the first two tests, and start there.
We build one part of this order into the product: no PoC, no finding. AI Swarm Pentest runs a swarm of agents that exploit what they identify, with real proofs of concept.
Deep Code Analysis covers your code and dependencies in depth, and Remediation produces automatic patches and ready-to-merge pull requests. We did not test CVE-2026-124194 ourselves, and this post does not claim that Plexicus detects it.
Related reading: reviewing secret-scanning alerts as evidence, why a runtime patch matters for PHP2Shell and proving a privilege boundary.
What do these numbers not show?
- They are Microsoft’s data at one point in time. Flags reflect each document’s revision as retrieved on November 16, and a CVE attacked later may not be flagged yet. June to August have had three to five months to collect flags and still show 4 of 1,178 assessed CVEs (0.34%).
- “Exploited” means exploited as far as Microsoft knows. It covers the CVEs Microsoft assesses, so two third-party CVEs in the document are in KEV without a flag. Counting every ID the documents hold, they flag 25 CVEs in 2025 and 13 from January to May 2026, because some were first published on other days.
- “Release day” is our rule, not a Microsoft field. A CVE counts if its earliest
RevisionHistoryentry falls on the release date. The 08 batch alone is 1,093 CVEs, 1,084 scored and 860 above 6.5, so the conclusion holds. - The scores are Microsoft’s, as published. We did not rescore anything. Our ranking covers the 1,085 of 1,096 CVEs with a base score, and the whole document has 1,561 scored CVEs, 1,134 of them above 6.5.
- The cause of the volume rise is not established. Dustin Childs of TrendAI’s Zero Day Initiative wrote that fewer exploited zero-days does not mean less exploitation, and CyberScoop quotes his view that AI helps attackers more with diffing patches than with finding flaws in closed-source code. That is one analyst’s reading, and we did not test it.
- We did not reproduce the attack, and 40 cases are not all attacks. The mechanism comes from Microsoft, CrowdStrike and Rapid7, and Microsoft has not published details of the attacks it saw. The 40 are the bugs Microsoft flagged, so we read them as a trend in ranking depth, not as proof about attacker behavior.
Frequently asked questions
Is CVE-2026-124194 a zero-day?
Microsoft’s document marks it exploited and not publicly disclosed at release. CyberScoop reports that none of the November vulnerabilities were publicly known beforehand. That fits the usual meaning of zero-day.
Why did Microsoft rate it Moderate when attackers are using it?
The base score describes the bug’s characteristics: a network path, a user who opens a file and confidentiality impact only. It does not change when attacks start, although the temporal score, which includes exploit maturity, came out at 6.2. Microsoft publishes the exploited flag as a separate field from its severity label.
Does a mid-range CVSS score mean I can defer a fix?
No. A 6.5 is Medium on the CVSS scale, where High starts at 7.0. Check the exploited flag and KEV before you defer anything. Of the 40 release-day CVEs Microsoft flagged over 23 months, nine scored below 7.0.
Does this matter if I only ship web applications?
The triage lesson applies to any backlog. The mechanism is a hypothesis worth testing: on Windows, an application that resolves a path or URL from untrusted input may attempt authentication to the destination. We have not tested that here.
Sources
- Microsoft Security Response Center, November 2026 security update document (CVRF API), retrieved November 16, 2026, and the CVE-2026-124194 advisory
- CISA, CISA Adds Six Known Exploited Vulnerabilities to Catalog, November 10, 2026, and the Known Exploited Vulnerabilities catalog
- NIST, NVD record for CVE-2026-124194, the CVE Program record and MITRE’s CWE-356
- CyberScoop, report on Microsoft’s November 2026 Patch Tuesday, November 10, 2026
- SecurityWeek, coverage of the exploited Outlook zero-day, November 10, 2026
- Rapid7, Patch Tuesday, November 2026, November 10, 2026
- CrowdStrike, November 2026 Patch Tuesday analysis, November 10, 2026
- Microsoft, Microsoft 365 Apps security updates, and Microsoft Defender Experts, Guidance for investigating attacks using CVE-2023-23397, March 24, 2023
- FIRST.org, EPSS API, scores dated November 15, 2026
- OpenAI, A thousand fewer paths to root, November 4, 2026