Etiqueta:

proof-driven AppSec

2 articles

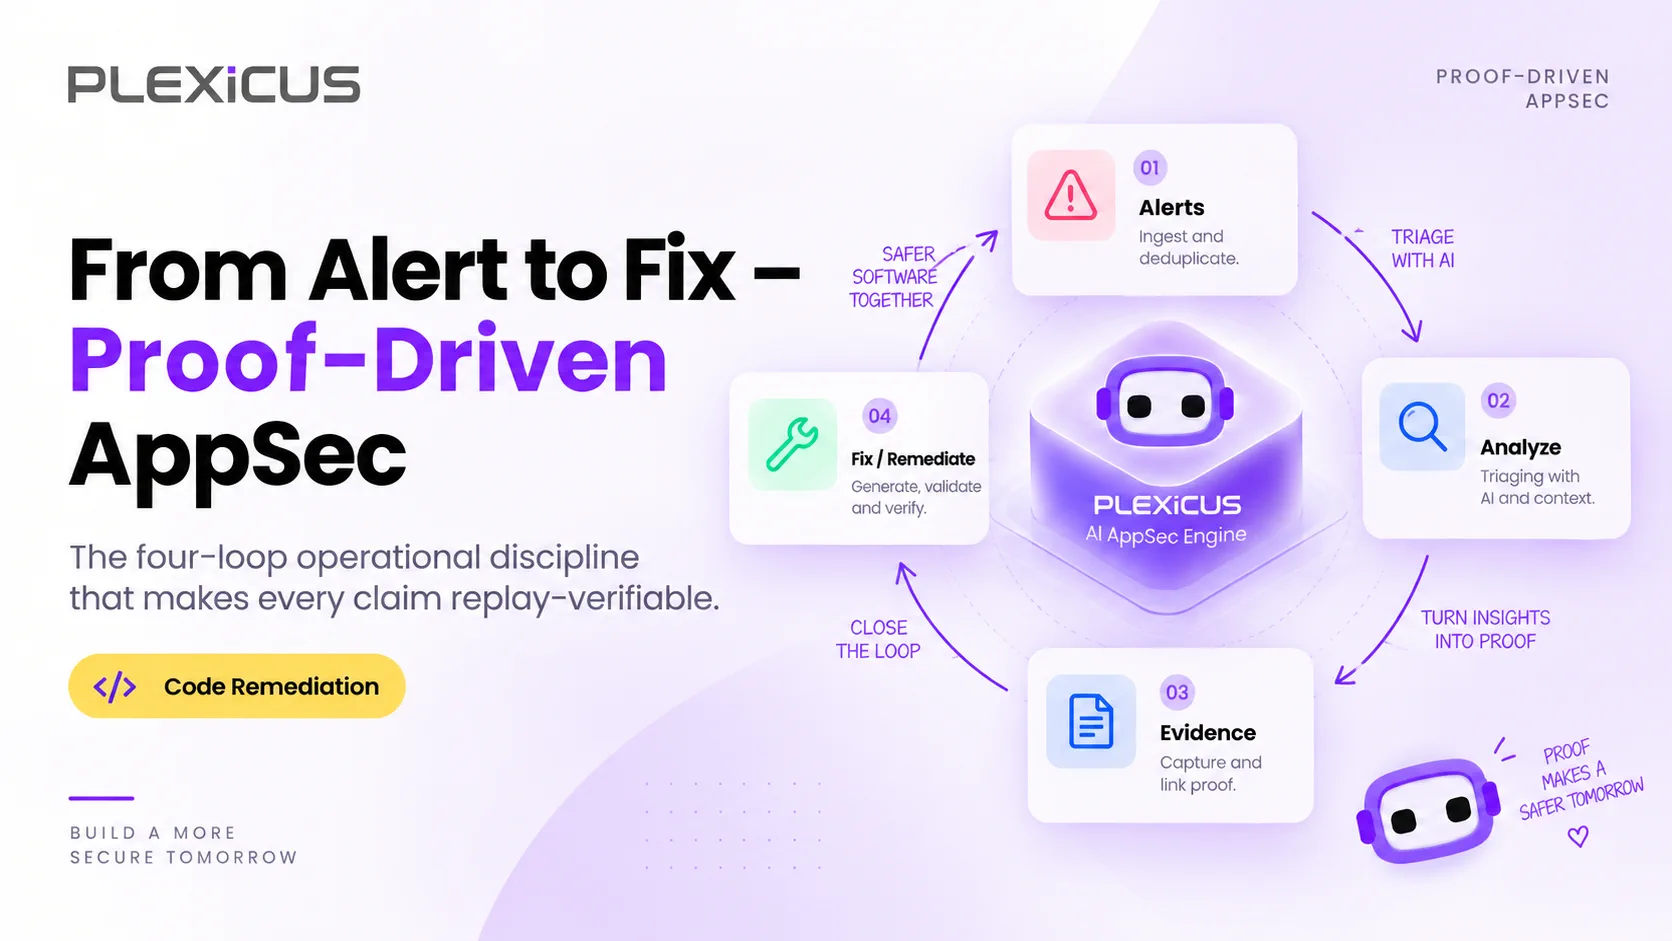
De la alerta a la corrección: cerrando el ciclo con AppSec basada en pruebas
Code Remediation

De la alerta a la corrección: cerrando el ciclo con AppSec basada en pruebas

La mayoría de los programas de seguridad son una serie de bucles desconectados: alerta, triaje, corrección, auditoría, otra corrección, otra auditoría. AppSec basada en pruebas cierra el ciclo de una vez y hace que cada paso sea demostrable. Esta es la definición canónica, la estructura de cuatro bucles y cómo se ve en producción.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
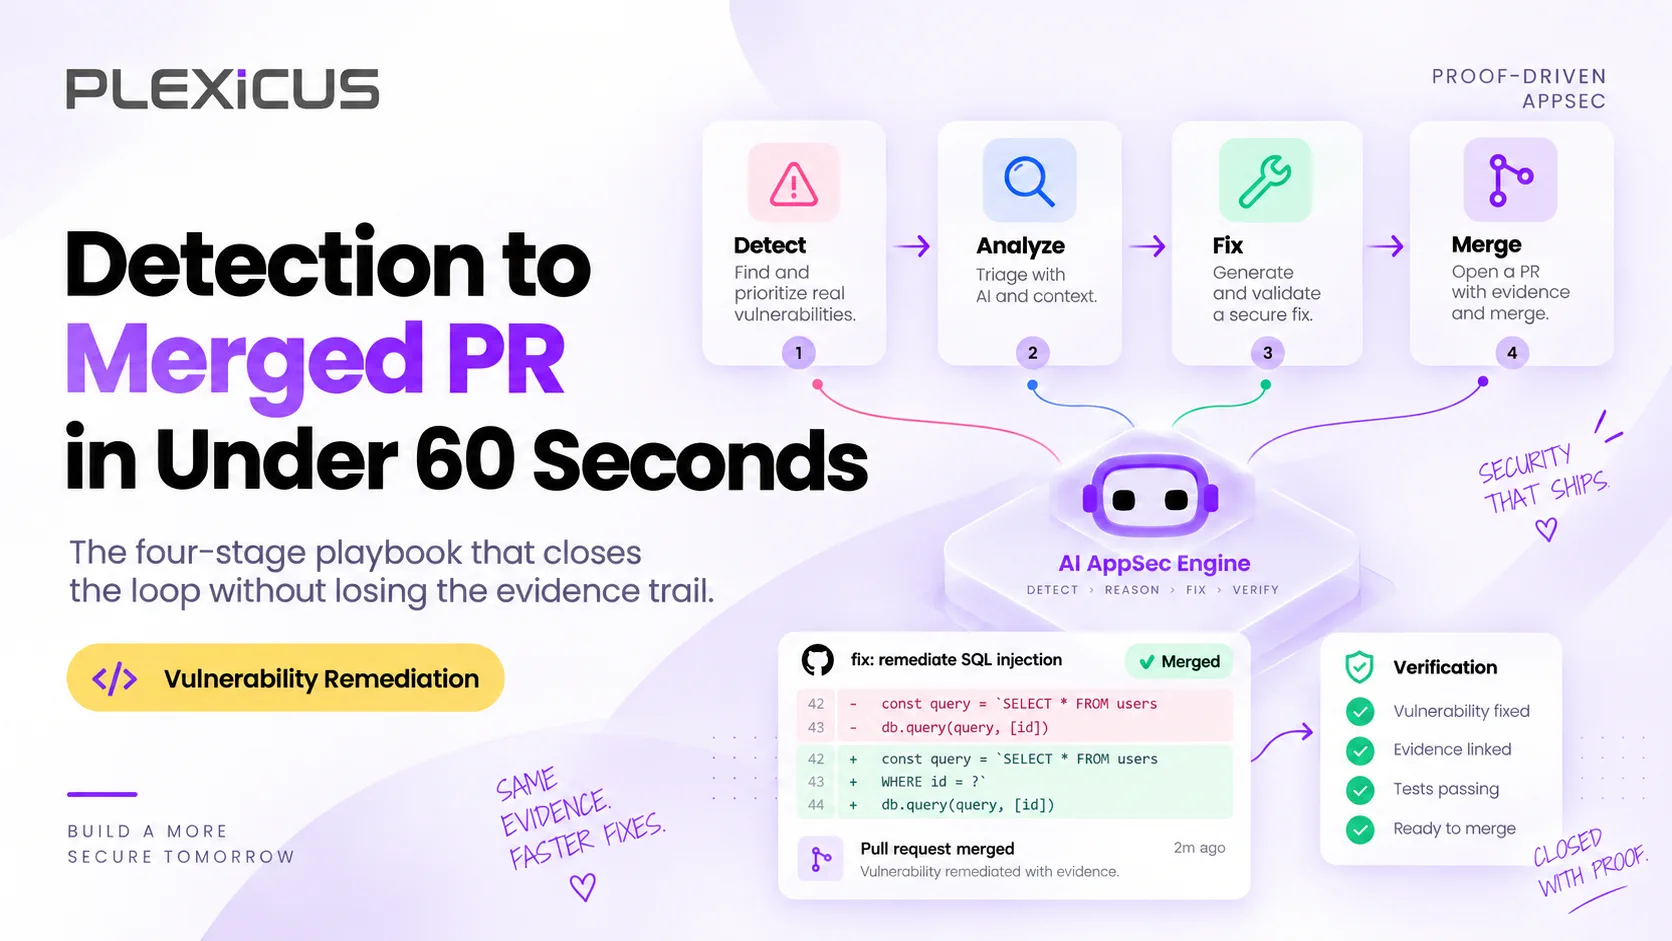
The Autonomous Remediation Playbook: From Detection to Merged PR in Under 60 Seconds
Vulnerability Remediation

The Autonomous Remediation Playbook: From Detection to Merged PR in Under 60 Seconds

The autonomous remediation playbook is the operational pattern that closes the loop from detection to merged PR in under 60 seconds. It is not magic. It is a four-step pipeline that turns a verified finding into a reviewer-ready patch without losing the evidence along the way.

Josuanstya Lovdianchel Josuanstya Lovdianchel ·
¿Listo para validar lo que importa?

Listo para validar lo que importa.

Plexicus es Proof-Driven AppSec: hallazgos validados, comprensión contextual y remediación revisada — anclada en evidencia, acotada contigo.

Calificación

Comprueba si el AI Swarm Pentest encaja en tu entorno.

Déjanos el contexto mínimo. Revisaremos el alcance y te indicaremos el siguiente paso comercial.

Antes de enviar — verifica que encajas
¿Tienes un pentest clásico reciente con el que no estás satisfecho?

0 / 280

Sin compromiso. Si no encajas, te lo decimos.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)