AI Swarm Pentest Deep Code Analysis Remediación

AppSec
Dirigida por Pruebas.

Validar. Entender.

Compatible con
Cursor
Copilot
Claude
Devin
Windsurf
Replit
Lovable
Codex
v0
+ 50 más

Equipos de seguridad confían en nosotros para cada base de código

Plexicus Platform · plexicus.ai

Tu plataforma
AppSec Proof-Driven fullstack.

Un recorrido guiado por la plataforma Plexicus: AI Swarm Pentest explora una ruta de ataque autorizada, Deep Code Analysis añade contexto y Remediación envía una corrección revisada.

Dashboard
Synthetic target · evidence view
Synthetic demo data · not from a live customer environment
Your value
7d30d90dAll

What Plexicus has saved you, and what is still on the table.

Validated attack paths
what your team can review
Reviewable evidence
attached to every finding
Reviewer-ready fixes
merge or reject with context
Compliance posture
NIS2 · DORA · EU AI Act · CRA
Risk Posture Score
58 / 100
Appetite: 25
Fix 14 findings to reach appetite
New vs Fixed
New Fixed
May 25Jun 1Jun 8Jun 15Jun 22Jun 29Jul 6Jul 13
Findings Report
2026 Apr, 28 - 2026 May, 12
Total Findings
132
Findings
130
Remediations
0
Ready to Remediate
2
Findings Ready to Remediate Remediations
Apr 28May 2May 6May 9May 12
Top Risky Repositories
demo-project/sample-app 92
Risk score
demo-project/checkout-api 71
Risk score
demo-project/portal 48
Risk score
Total Findings
Total
143
Aggregated
132
Prioritized
98
132 Findings severity
  • Critical 12
  • High 34
  • Medium 58
  • Low 28
Nexus evidence view
Illustrative product view A clear handover from exploration to evidence. Synthetic Nexus runtime — illustrative representation, not from a live customer environment.
Reservar Pentest Empieza con un engagement acotado, evidencia validada y una ruta de remediación lista para auditoría.
El flujo Proof-Driven

Validar. Entender. Remediar.

Valida el riesgo real, entiende el impacto y remedia con evidencia en cada base de código.

AUTHORISED
EVIDENCE VERIFIED
01 / 03
Validar

AI Swarm Pentest

AI Swarm Pentest explora rutas autorizadas en tu aplicación y captura la evidencia detrás de cada ruta de ataque verificada.

  • Misiones con scope controlado y revisión humana en los guardarraíles
  • Evidencia adjunta a cada hallazgo
  • Contexto compartido para handoffs consistentes
Explorar AI Swarm Pentest
deep_code_analysis finding context
01 context Relevant input identified
02 review Security decision checked
03 impact Controls assessed
04 handover Evidence attached
outcome: ready for review
02 / 03
Entender

Deep Code Analysis

Deep Code Analysis añade contexto de código y lógica de negocio a cada hallazgo validado.

  • Análisis profundo de código asistido por IA con contexto semántico
  • Modos para lógica de negocio, autorización, SAST clásico o combinado
  • Cola de triage priorizada por lo que merece la pena
Explorar Deep Code Analysis
fix_pr .diff
+12+ reviewer control added
+ 3+ request validation added
- 4- unreviewed operation
+ 8+ rationale attached
CI: passing PR: #142
03 / 03
Remediar

Remediación

Plexicus prepara correcciones revisadas y listas para fusionar, y soporta re-tests de verificación.

  • Patches revisados y listos para fusionar, con una justificación clara
  • Flujo de pull request con asignación de revisor
  • Re-tests de verificación confirman que la corrección se mantiene
Explorar Remediación
AI Swarm Pentest

Descubre lo que un atacante puede alcanzar realmente.

Plexicus prueba la superficie autorizada de tu aplicación, valida los caminos relevantes y entrega evidencia que tu equipo puede revisar y usar.

  1. 01
    Explora la superficie autorizada.

    Comprobaciones independientes examinan la aplicación, la API y los caminos de código dentro del alcance acordado.

  2. 02
    Conserva solo la evidencia que se sostiene.

    Los hallazgos avanzan solo cuando se puede revisar la evidencia de respaldo.

  3. 03
    Da a cada equipo una siguiente acción clara.

    Tu equipo recibe contexto de impacto, guía de remediación y una entrega lista para revisión.

Reservar Pentest

Alcance definido con tu equipo. Sin cambios en producción sin revisión.

VISTA DE PRODUCTO SINTÉTICA · ENTORNO DE DEMO AUTORIZADO
01 Camino validado 02 Evidencia adjunta 03 Listo para la entrega

Caminos de ataque validados. Evidencia que tu equipo puede usar.

Deep Code Analysis

Ve el contexto detrás del hallazgo.

El Análisis Profundo de Código conecta el código, el flujo de datos y el impacto de negocio para que tu equipo se enfoque en los hallazgos que importan.

Finding review / FINDING-001

Request validation finding

Open High priority Needs review
TL;DR

The endpoint accepts user input without the validation the workflow requires. The team can review the evidence and proposed control.

IMPACT

The issue could let an attacker reach an unintended operation. Impact and scope are shown for review.

LOCATION

sample-project · review context

GET request input
SEVERITY High
CVSS High
FIX EFFORT Low
DISCOVERED Synthetic demo

Discover & Validate

Review priority findings against the agreed scope, with supporting evidence and a clear next action.

Suggested remediation Evidence review
WHAT'S NEXT?

Drafts a reviewer-ready change for the priority finding, scoped to your team's review workflow.

reviewer-ready change Copy
23manual step
24context cleared
24+reviewer control added
25+validation rule attached
26+evidence included
27handed back to your team
28+ready for review
25 29change returned to reviewer
Validation status: ready for review

Reviewed Remediation

Drafts a remediation for review. Your team decides whether to merge.

Ver AI Swarm Pentest →

Remediación

Parches revisables preparados para tu equipo.

Plexicus prepara el trabajo — tu equipo es dueño del merge.

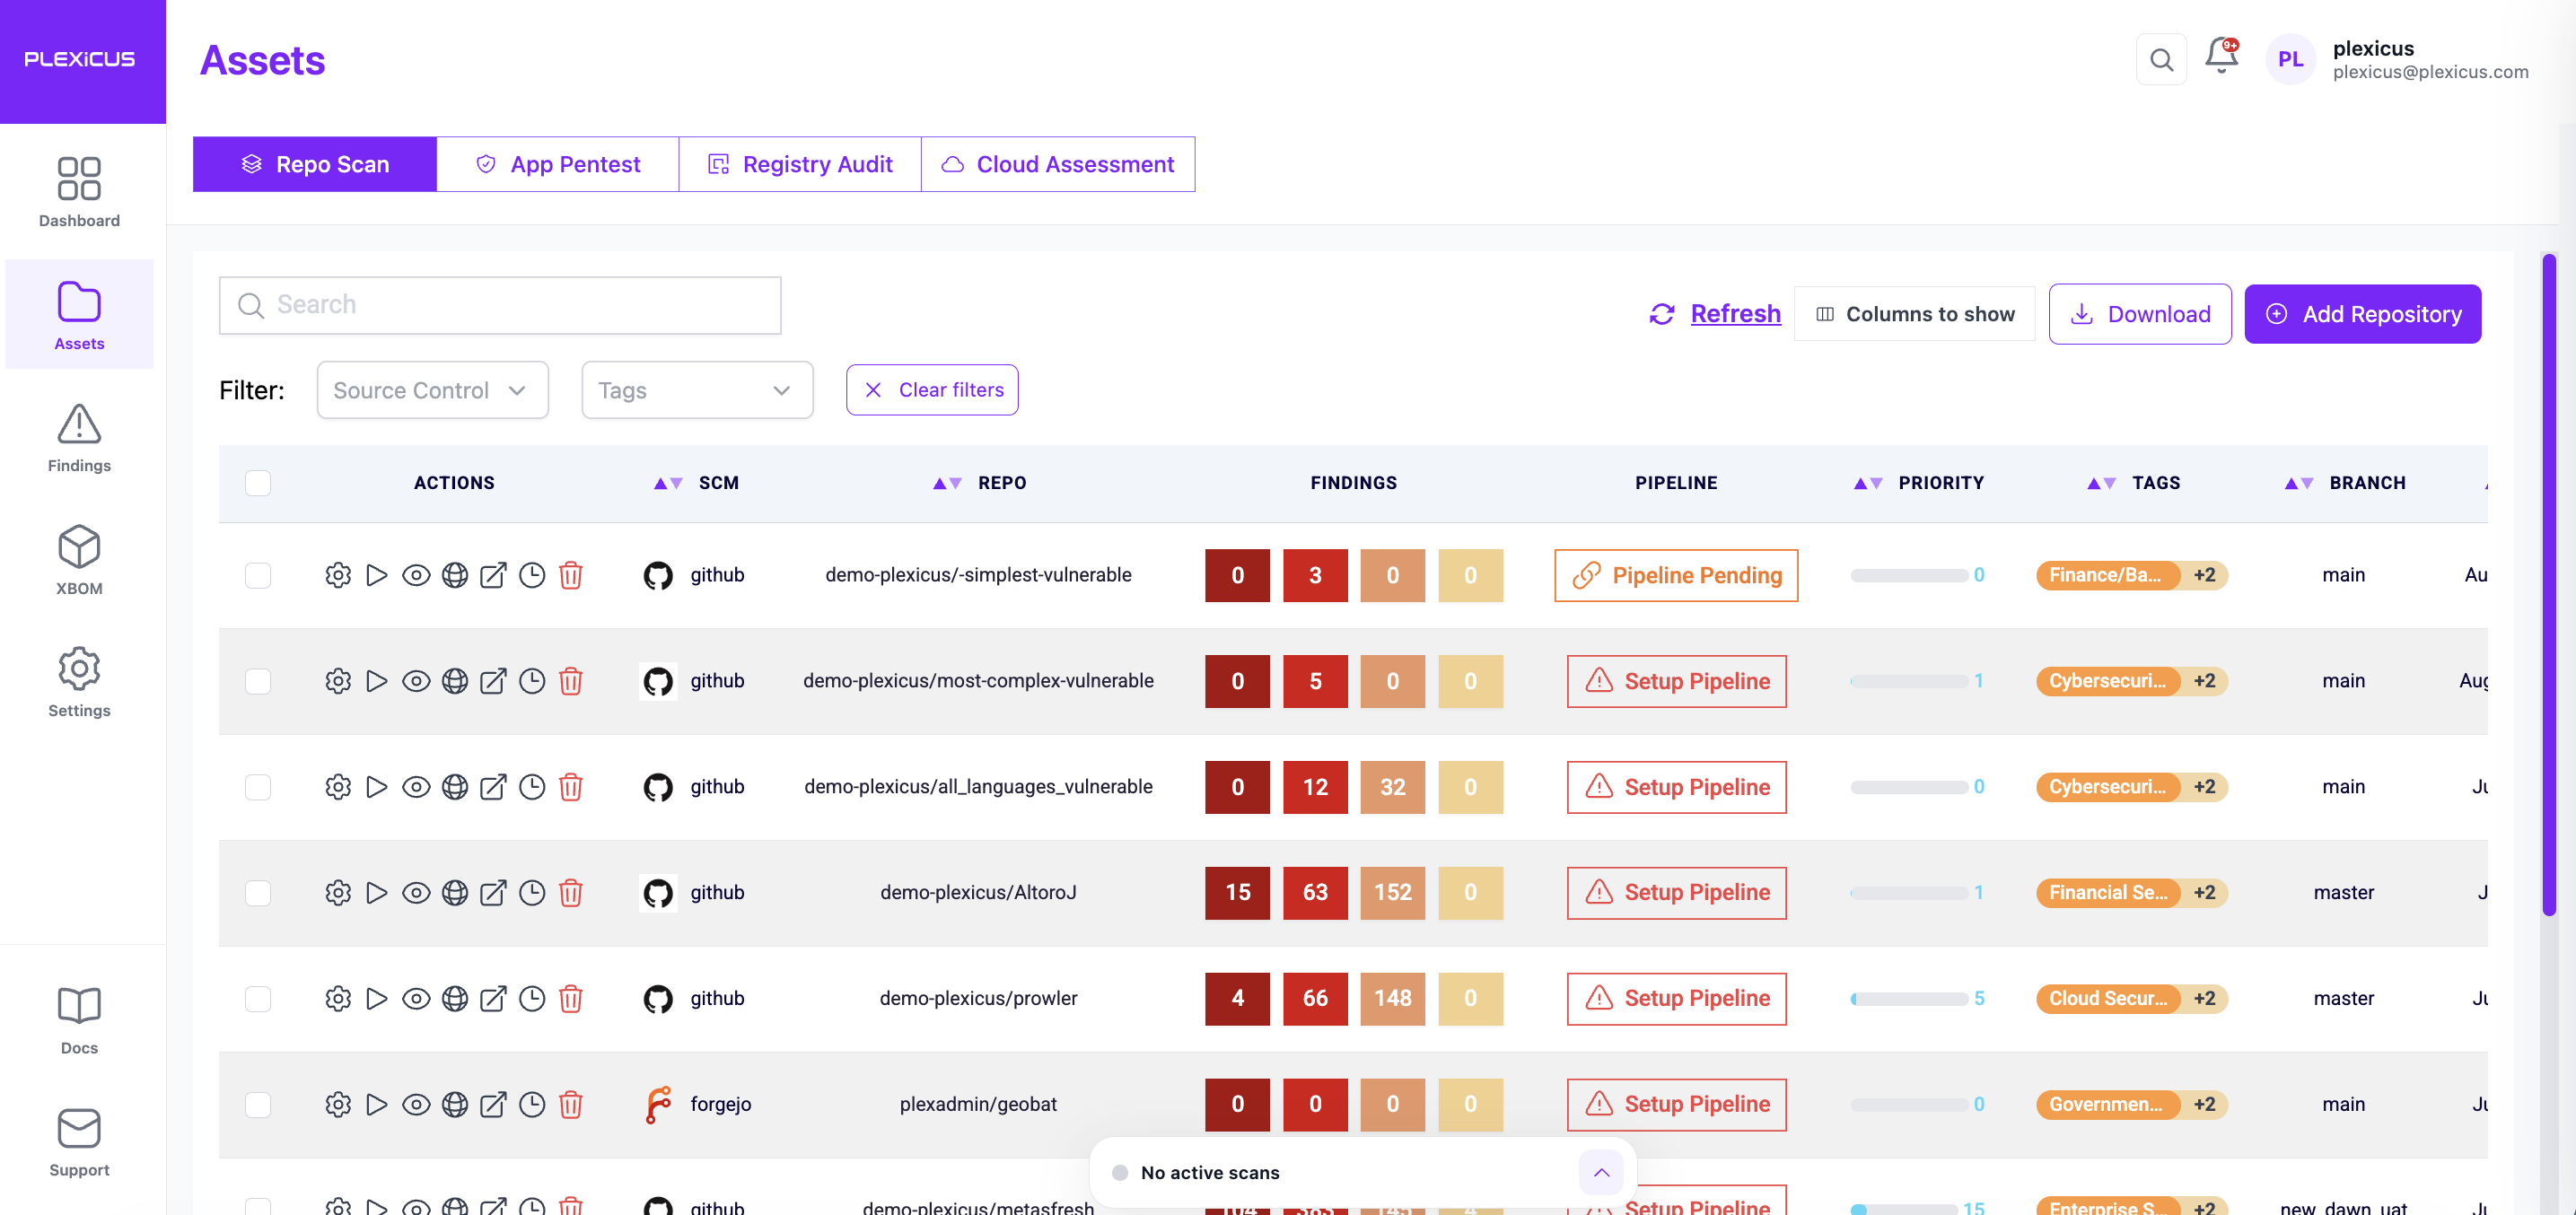
Plexicus Assets view: repo scan, app pentest, and code insights, with pipeline status and finding counts per asset.
Synthetic demonstration data. Sensitive identifiers and customer data are not shown.
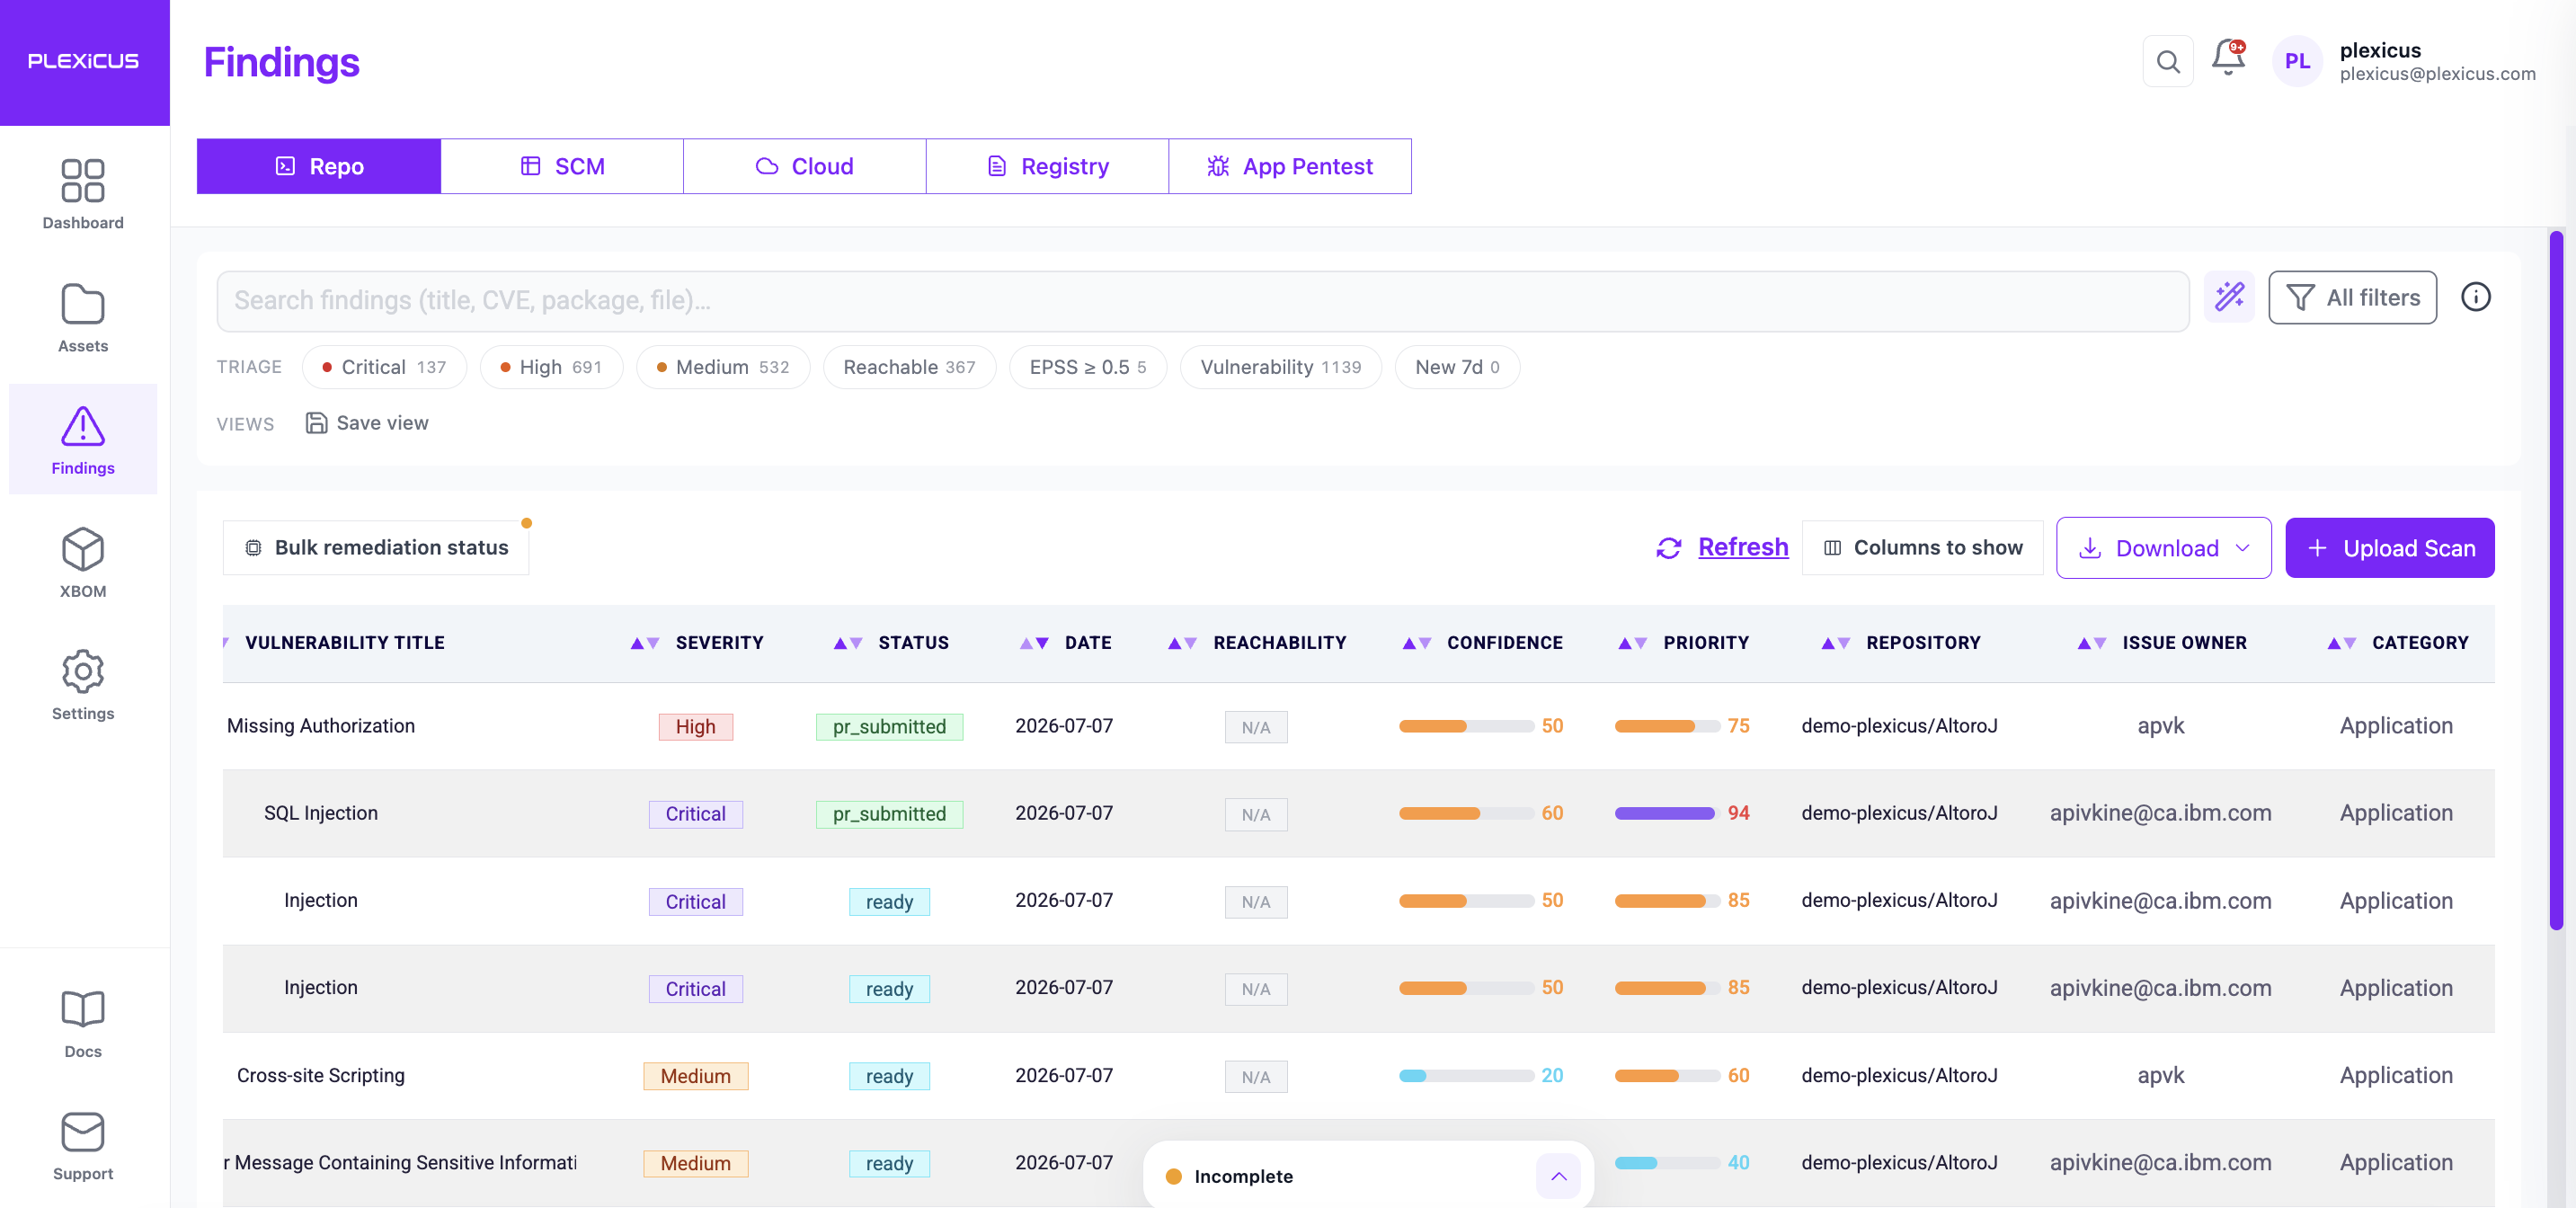
Plexicus Findings view: vulnerability table with severity, status, date, reachability, confidence, priority, repository
Live view from app.plexicus.ai — findings table with severity, status, reachability, confidence, and priority per row.
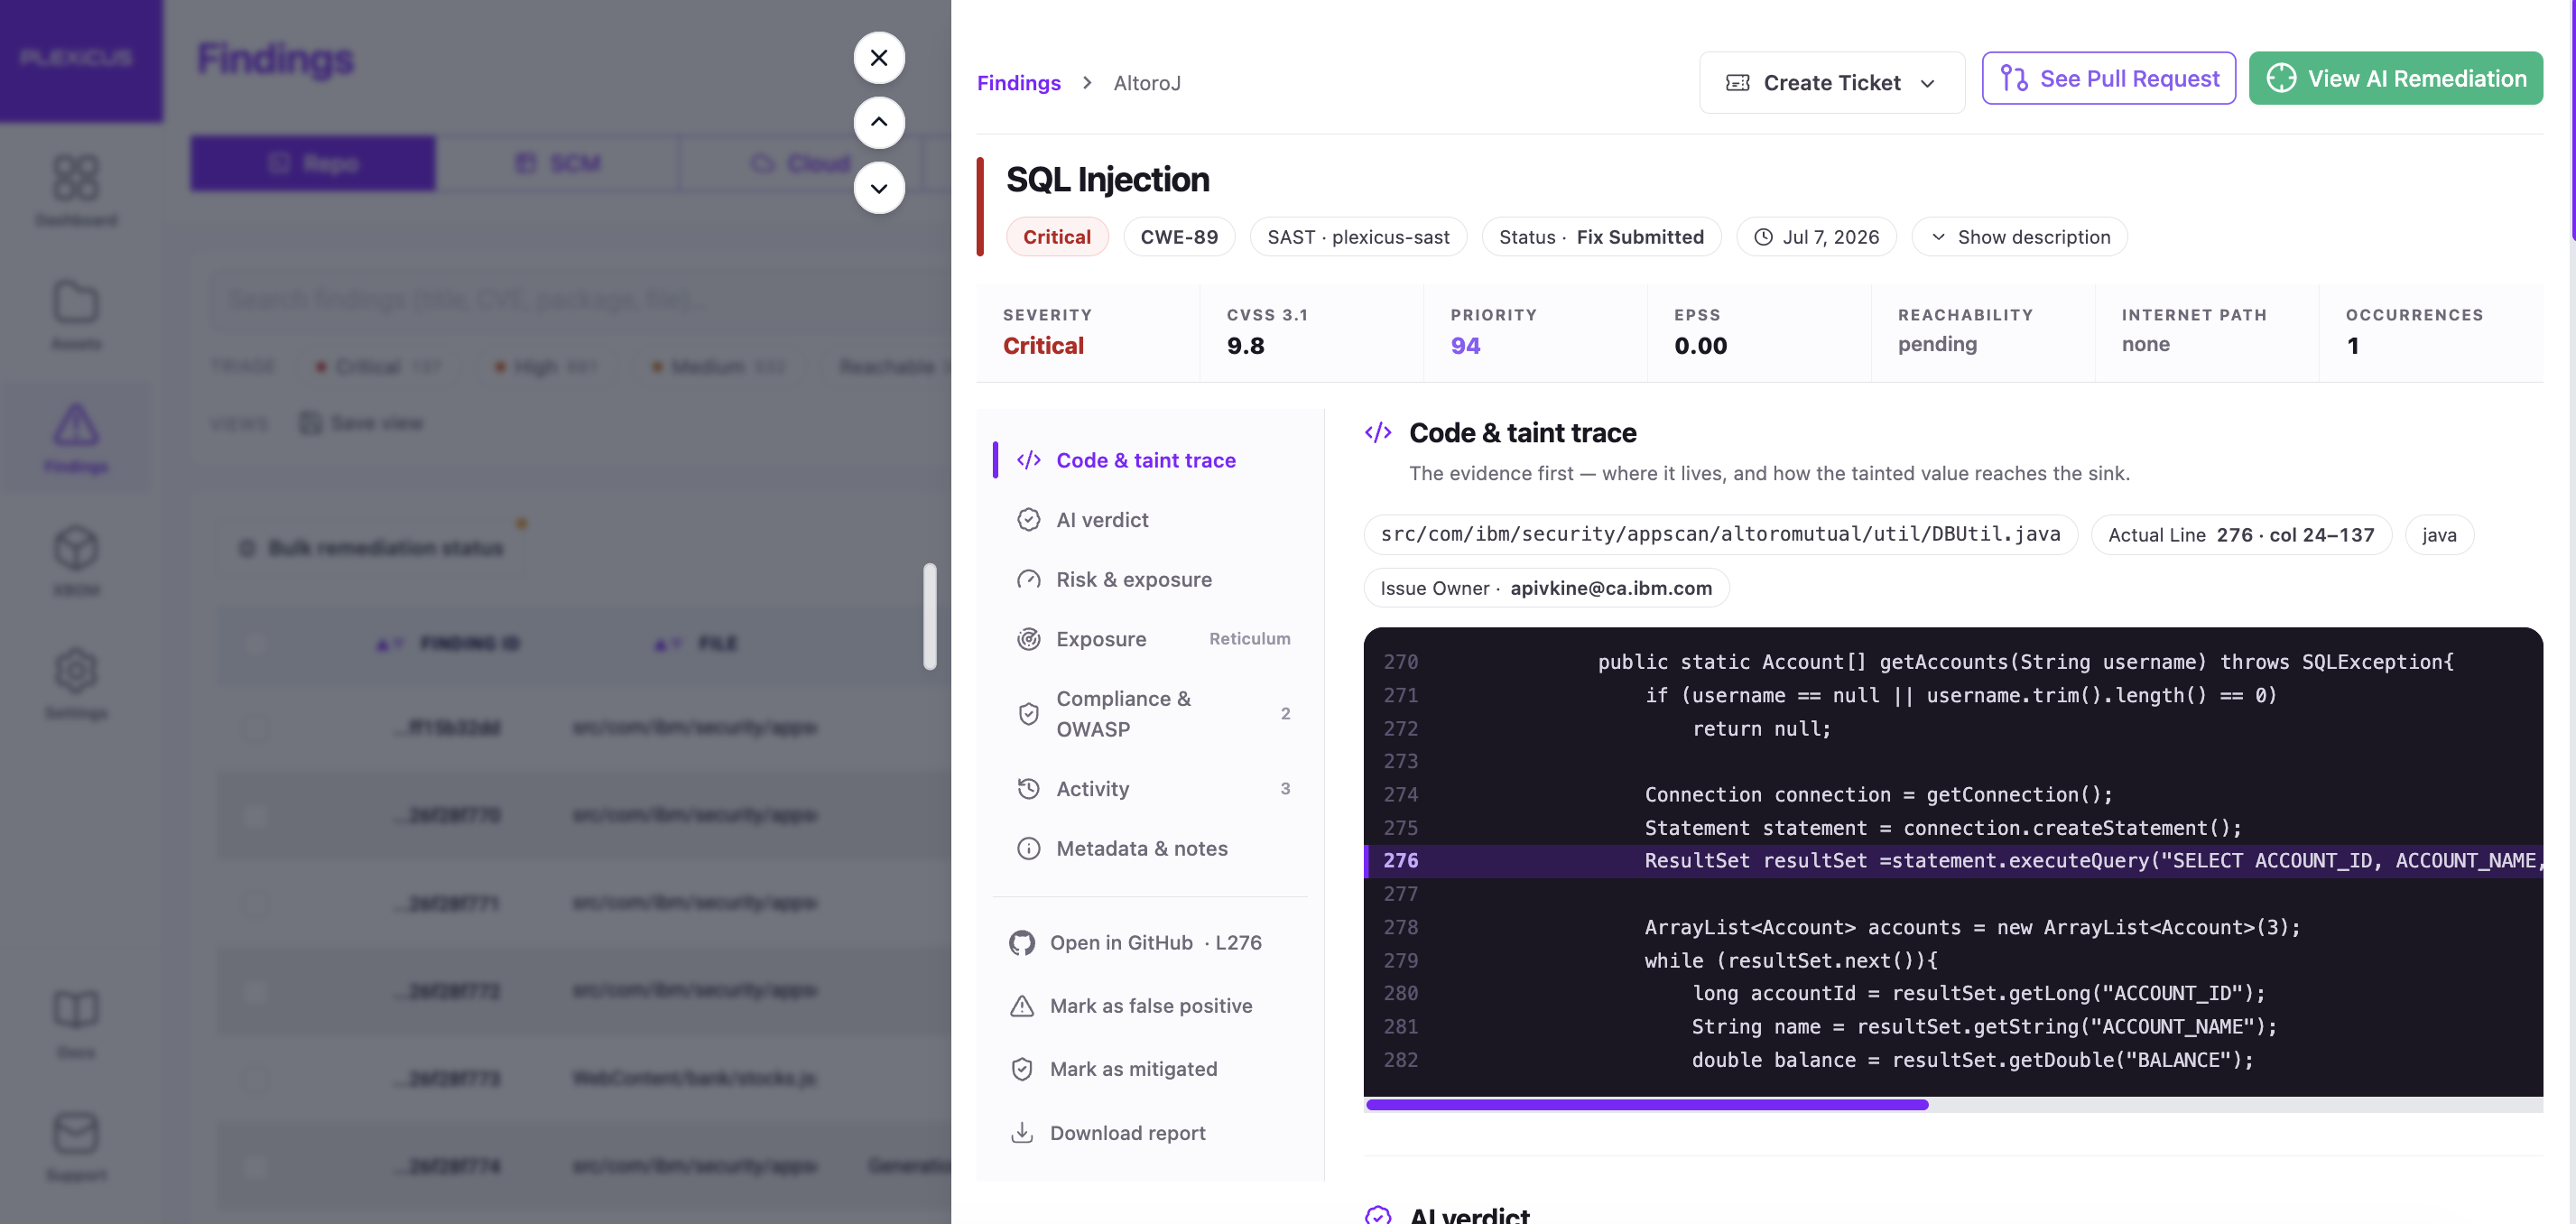
Plexicus finding detail: SQL Injection with severity, CVSS, EPSS, code & taint trace, and source line
Live view from app.plexicus.ai — finding detail with code & taint trace, the evidence first, showing how the tainted value reaches the sink.

Para el líder de seguridad

Control empresarial sin frenar la entrega.

Cadena de evidencia adjunta a cada hallazgo cerrado.

Despliega según tus necesidades

SaaS, autoalojado, local o aislado.

Tu código sigue siendo tuyo

Cero retención de datos. No entrenamos con tu código. Residencia de datos en la UE por defecto.

Soporte dedicado

Incorporación estructurada, SLA personalizados y documentación de seguridad.

Listo para auditoría

Certificación SOC 2 Tipo II. Cualificación CPSTIC en curso.

Visita el Trust Center →
Coverage · Integrations · Standards
SAST Compliance XBOM Commercial Connector SCA AI Code Security OWASP Top 10 AI Swarm Pentest Deep Code Analysis Remediation
Synthetic inventory data · illustrative only
XBOM

Cada componente, algoritmo y modelo
en un inventario respaldado por evidencia.

SBOM + CBOM + AIBOM, con declaraciones VEX, watchlists, diffs y exportación CycloneDX / SPDX / PDF. Construido para EU CRA, CISA 2025, PCI DSS 6.3.2 y EU AI Act.

One source

SBOM · CBOM · AIBOM

Changes traced

VEX and inventory diffs

Ready to act

CycloneDX · SPDX · PDF

Explorar XBOM
LIVE INVENTORY REPOSITORY / demo workspace
SBOM · CBOM · AIBOM
VEX ATTACHED Synthetic demo data · illustrative
demo-library Dependency · review required Evidence → component status → next action
Exportable proof CycloneDX · SPDX · PDF

XBOM

Every component, algorithm and model in one evidence-backed inventory. VEX statements, watchlists, diffs, and CycloneDX / SPDX / PDF export — for EU CRA, CISA 2025, PCI DSS 6.3.2 and EU AI Act.

La confianza de equipos de seguridad en cada base de código

Equipos que confían en Plexicus para asegurar el código que escribe su IA — y el código que heredaron.

Plexicus is the most innovative AI-native platform we've evaluated. Their pace of evidence-backed remediation context is what sets them apart.

Toni de la Fuente
Toni de la Fuente
Founder, Prowler
five stars

The AI agent gives our team verified findings with the evidence attached. Our engineers review with confidence instead of chasing noise.

David Wilson
David Wilson
Head of Security, HuMaIND
five stars

As one of Plexicus's first customers, we've witnessed firsthand how their platform has evolved into an indispensable security solution. Reviewed changes with prioritized context have dramatically reduced our vulnerability management overhead and allowed our security team to focus on strategic initiatives.

Jose Fernando Dominguez
CISO, Ironchip
five stars

Plexicus's powerful vulnerability management allows us at Puffin Security to deliver more advanced cybersecurity services to our clients, creating a perfect security partnership.

Ricardo Stefanescu
Ricardo Stefanescu
CEO, Puffin Security
five stars

Plexicus has streamlined our remediation review process — our team has more hours back every week to focus on the changes that matter.

Alejandro Aliaga
Alejandro Aliaga
CTO, Ontinet
five stars

The integration is seamless, and the reviewed change workflow with full evidence attached has made our security review cycle measurably faster.

Michael Chen
Michael Chen
DevSecOps Lead, Devtia
five stars

Plexicus has become an essential part of our security toolkit. It's like having an expert security engineer available 24/7.

Jennifer Lee
Jennifer Lee
CTO, Quasar Cybersecurity
five stars

Since implementing Plexicus, we've seen a dramatic improvement in our security posture with less effort from our team. Verified findings with evidence attached are what we wanted from a modern security platform.

Alejandro Acosta
Alejandro Acosta
CTO, Wandari
five stars
¿Listo para validar lo que importa?

Listo para validar lo que importa.

Plexicus es Proof-Driven AppSec: hallazgos validados, comprensión contextual y remediación revisada — anclada en evidencia, acotada contigo.

Calificación

Comprueba si el AI Swarm Pentest encaja en tu entorno.

Déjanos el contexto mínimo. Revisaremos el alcance y te indicaremos el siguiente paso comercial.

Antes de enviar — verifica que encajas

Equipos con menos de 50 desarrolladores: empieza una prueba de 14 días en lugar de reservar una demo. Empieza una prueba de 14 días →

0 / 280

Sin compromiso. Si no encajas, te lo decimos.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorised target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)



